
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
On an MSI system, Secure Boot cannot be enabled reliably until Windows is using UEFI firmware and the system disk uses the GPT partition style. If Windows is installed in Legacy/CSM mode on an MBR disk, changing the firmware setting first can leave the PC unable to boot.
Use the checks below before changing BIOS settings. The menu names differ between MSI motherboards and laptops, but the required order is the same: check Windows, confirm GPT, switch to UEFI, enable Secure Boot, then verify the result.
Before enabling Secure Boot
Check the current boot configuration from Windows first.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →- Press Win + R, type
msinfo32, and press Enter. - In System Information, find BIOS Mode.
- Note the value of Secure Boot State.
For Secure Boot, BIOS Mode should be UEFI. If it says Legacy, do not enable Secure Boot yet.
#1 Best Overall

- AMD AM4 Socket and PCIe 4.0: The perfect pairing for 3rd Gen AMD Ryzen CPUs.Bluetooth v5.2
- Robust Power Design: 8+2 DrMOS power stages with high-quality alloy chokes and durable capacitors to provide reliable power for the last AMD high-count-core CPUs
- Optimized Thermal Solution: Fanless VRM and PCH heatsink, multiple hybrid fan headers and fan speed management with Fan Xpert 4 or the UEFI Q-Fan Control utility
- High-performance Gaming Networking: WiFi 6 (802.11ax), 2.5 Gb LAN with ASUS LANGuard
- Best Gaming Connectivity: Supports HDMI 2.1 (4K@60HZ) and DisplayPort 1.2 output, featuring dual M.2 slots (NVMe SSD)—one with PCIe 4.0 x4 connectivity, front panel USB 3.2 Gen 1 connector, USB 3.2 Gen 2 Type-C & Type-A ports and Thunderbolt 3 header, 1 x SPI TPM header
Check whether the system disk is GPT
- Right-click the Start button and open Disk Management.
- Right-click the disk containing the Windows installation. This is usually Disk 0, but confirm rather than assuming.
- Select Properties, open the Volumes tab, and inspect Partition style.
The result should be GUID Partition Table (GPT). If it is Master Boot Record (MBR), convert the system disk before changing MSI from Legacy/CSM to UEFI.
Enable Secure Boot on an MSI motherboard
These steps apply to MSI desktop motherboards using the current Click BIOS layout. Your exact BIOS version may use slightly different wording for the Secure Boot page.
- Restart the computer.
- When the MSI logo appears, repeatedly press Delete to enter BIOS.
- If BIOS opens in EZ Mode, press F7 for Advanced mode.
- Open Settings → Advanced → Windows OS Configuration.
- Set BIOS CSM/UEFI Mode to UEFI.
- Open the Secure Boot menu. Depending on the board and BIOS version, it may be under Security → Secure Boot or Settings → Security → Secure Boot.
- Set Secure Boot to Enabled.
- Press F10, confirm saving the changes, and allow the computer to restart.
Changing BIOS CSM/UEFI Mode to UEFI is important. On many MSI motherboards, the Secure Boot option does not appear until CSM has been disabled in this way.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteEnable Secure Boot on an MSI laptop
MSI laptops generally use a shorter menu path:
- Restart the laptop and repeatedly press Delete when the MSI logo appears.
- Open Security → Secure Boot.
- Set Secure Boot to Enabled.
- Press F10 to save and reboot.
Some laptop firmware versions show a different arrangement, so look under the BIOS Security section if the option is not immediately visible. The laptop must still be configured for UEFI boot.
If Windows is installed on an MBR disk
Microsoft’s MBR2GPT.exe can convert a supported Windows system disk from MBR to GPT without deleting the data on that disk. It converts the system disk only; it is not a general-purpose converter for any attached MBR drive.
Back up important files first. If BitLocker is active, suspend protection before conversion. Microsoft notes that existing BitLocker protectors must be recreated after the conversion before protection is resumed.
Rank #2

- AM4 socket: Ready for AMD Ryzen 3000 and 5000 series, plus 5000 and 4000 G-series desktop processors.Bluetooth v5.2
- Best gaming connectivity: PCIe 4.0-ready, dual M.2 slots, USB 3.2 Gen 2 Type-C, plus HDMI 2.1 and DisplayPort 1.2 output
- Smooth networking: On-board WiFi 6E (802.11ax) and Intel 2.5 Gb Ethernet with ASUS LANGuard
- Robust power solution: 12+2 teamed power stages with ProCool power connector, high-quality alloy chokes and durable capacitors
- Renowned software: Bundled 60 days AIDA64 Extreme subscription and intuitive UEFI BIOS dashboard
Convert from a normal Windows session
- Open Command Prompt as administrator. Search for
Command Prompt, right-click it, and choose Run as administrator. - Validate the system disk:
mbr2gpt /validate /allowFullOS- If validation succeeds, run the conversion:
mbr2gpt /convert /allowFullOSThe /allowFullOS switch is required when the command runs inside the full Windows environment rather than Windows PE. If the PC has more than one possible system disk and you need to target a particular disk, the syntax supports a disk number, for example:
mbr2gpt /validate /disk:0 /allowFullOSDo not guess the disk number. Confirm it in Disk Management first.
A failed validation commonly means the disk has more than three primary partitions, an extended or logical partition, insufficient space for GPT metadata, invalid boot configuration data, an unsupported partition type, or active BitLocker protection. Resolve the reported problem rather than proceeding directly to BIOS.
Switch the firmware to UEFI after conversion
Conversion alone does not finish the process. Restart, enter MSI BIOS with Delete, and set:
Settings → Advanced → Windows OS Configuration → BIOS CSM/UEFI Mode → UEFI
Then open the Secure Boot menu, enable Secure Boot, press F10, and reboot. The firmware must be in UEFI mode or the converted Windows installation may not start.
Rank #3
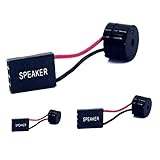
- [Quick PC Diagnostic Tool] Is your new PC build showing a black screen? This motherboard speaker translates silent hardware failures into clear BIOS beep codes. Instantly identify if your RAM, CPU, or GPU is causing the boot failure without guessing.
- [Essential for DIY PC Builders] Modern motherboards often lack built-in audio alerts. Plugging in this mini piezo buzzer before your first boot ensures you hear the satisfying “single beep” of a successful POST, giving builders immediate peace of mind.
- [Universal 4-Pin Header Compatibility] Wondering if it fits your board? It features a standard 4-pin female connector (with 2 active wires) that perfectly matches the “SPEAKER” or “SPK” front panel header on almost all ATX, Micro-ATX, and Mini-ITX motherboards.
- [Clean Wiring & Loud Alarm] Designed with an approx. 3-inch cable, it is long enough to easily plug into the motherboard but short enough to reduce PC case wiring clutter. The premium piezo element delivers a loud, crisp beep that is impossible to miss.
- [Valuable 3-Pack for IT Repair] Includes 3 internal BIOS buzzers in one pack. Perfect for IT technicians keeping spare diagnostic tools in their repair kits, or PC enthusiasts testing multiple rigs. A cost-effective solution to save hours of troubleshooting.
Confirm that Secure Boot is active
- After Windows starts, press Win + R.
- Enter
msinfo32and press Enter. - Check that BIOS Mode says UEFI.
- Check that Secure Boot State says On.
If the state says Off, return to BIOS and check that Secure Boot is enabled and that the machine is not still using CSM or Legacy mode.
Secure Boot and TPM are different
Secure Boot checks whether boot software is trusted. TPM 2.0 is a separate security feature used by Windows and applications such as BitLocker. Turning on one does not automatically turn on the other.
On the MSI MAG B550 TOMAHAWK example, the TPM path is:
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsSettings → Security → Trusted Computing → Security Device Support → Enabled
Press F10 to save and restart. From Windows, press Win + R, run tpm.msc, and check the result. AMD fTPM 2.0 indicates an available, enabled TPM on a supported AMD system; Compatible TPM cannot be found indicates that Windows has not detected one.
Optional: change MSI’s Secure Boot policy
Most users only need Secure Boot enabled. MSI also provides an image policy setting on applicable firmware. It can appear at either:
Rank #4

- Ready for Advanced AI PC: Designed for the future of AI computing, with the power and connectivity needed for demanding AI applications
- AMD AM5 Socket: Ready for AMD Socket AM5 for AMD Ryzen 9000 & 8000 & 7000 Series Desktop Processors
- Enhanced Power Solution: 14+2+1 80A DrMOS power stages, 8-layer PCB, 8+8 pin ProCool power connectors, alloy chokes and durable capacitors for stable power delivery
- Latest M.2 Support: One onboard PCIe 5.0 M.2 slot and two PCIe 4.0 M.2 slots, equipped with all M.2 heatsinks
- Ultrafast Connectivity: Wi-Fi 7, PCIe 5.0 x16 slot, Realtek 2.5Gb Ethernet, rear USB 20Gbps Type-C port, front USB 10Gbps Type-C connector, Thunderbolt (USB4) header support
- Security → Secure Boot
- Settings → Security → Secure Boot
MSI states that Security Boot Mode must be set to Custom before Image Security Policy is exposed. The policy options include Always Execute and Deny Execute. Always Execute is the compatibility-oriented behavior; Deny Execute applies the stricter policy. Do not change this setting unless you understand how it affects option ROMs and boot images.
Recommended Free Tools
Fix common MSI Secure Boot problems
| Problem | Likely cause | What to do |
|---|---|---|
| Secure Boot is missing from BIOS | CSM is still enabled | Go to Settings → Advanced → Windows OS Configuration and change BIOS CSM/UEFI Mode to UEFI. |
| Windows stops booting after the change | Windows was installed in Legacy mode or the disk is MBR | Return to BIOS and restore the previous boot mode temporarily. Check msinfo32 and Disk Management, then convert the system disk with MBR2GPT if it passes validation. |
| No boot device after MBR2GPT | Firmware was left in Legacy/CSM mode | Enter BIOS and select UEFI. MBR2GPT conversion does not automatically change firmware settings. |
| MBR2GPT validation fails | Partition layout, BCD, disk space, partition type, or BitLocker problem | Read the validation error and correct that specific issue. Do not use the conversion command repeatedly without resolving the failure. |
| Secure Boot Violation appears | Firmware rejected the boot image or a recovery process is required | On MSI laptops, enter BIOS with Delete, choose Security → Secure Boot → Disable, save with F10, and follow MSI’s model-specific recovery procedure. MSI’s procedure uses an empty FAT32 USB drive, the supplied recovery tool, and the F11 boot menu; re-enable Secure Boot after recovery. |
What not to assume
- Do not use a single universal MSI menu path. Motherboards and laptops expose Secure Boot in different places.
- Do not enable Secure Boot while Windows is still installed for Legacy/CSM boot.
- Do not treat TPM and Secure Boot as the same feature.
- Do not assume
mbr2gpt /convertis the whole procedure; you must switch the firmware to UEFI afterward. - Do not assume every Windows 11 upgrade requires Secure Boot to be switched on. The device must be Secure Boot-capable with UEFI enabled; enabling Secure Boot provides additional protection.
FAQ
Why is Secure Boot not showing in my MSI BIOS?
On many MSI motherboards, Secure Boot appears only after you change Settings → Advanced → Windows OS Configuration → BIOS CSM/UEFI Mode to UEFI. On laptops, check Security → Secure Boot.
Can I enable Secure Boot on an MBR disk?
Do not switch to UEFI and Secure Boot until the Windows system disk is GPT. Use Disk Management to check the partition style, then use Microsoft’s mbr2gpt tool if the disk passes validation.
Will enabling Secure Boot erase Windows?
Changing the BIOS setting does not normally erase Windows, but an incompatible Legacy/MBR boot configuration can prevent Windows from starting. Back up important files and confirm UEFI and GPT before enabling it.
Does Secure Boot require TPM 2.0?
No. Secure Boot and TPM are separate BIOS features. TPM 2.0 may be required for Windows 11 or other security functions, but it is not required merely to enable Secure Boot.
Free tools Windows power users keep installed
One-click scans. No signup required.
How do I check Secure Boot after enabling it?
Run msinfo32 from Win + R and confirm BIOS Mode: UEFI and Secure Boot State: On.
The Bottom Line
For an MSI motherboard, first confirm that Windows uses UEFI and that the system disk is GPT. Then enter BIOS with Delete, switch BIOS CSM/UEFI Mode to UEFI, enable Secure Boot from the model’s Secure Boot menu, and save with F10. MSI laptops usually expose the setting directly at Security → Secure Boot → Enable. Finally, run msinfo32 in Windows and confirm that Secure Boot State is On.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

