
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Use the narrowest capture method that matches your target. For an app you develop, start with Android Studio’s Network Inspector. For browser or emulator traffic, configure the Android System Proxy and install your interception tool’s certificate authority (CA) when you need HTTPS contents. For a physical phone, enable developer options and USB debugging, connect through adb, and then use the same proxy or logging workflow. If an app bypasses the operating-system proxy, switch to a TUN or lower-level capture mode. Seeing a connection is not the same as decrypting it: the client must trust the interception CA, and certificate pinning or app policy can still block plaintext.
Only capture devices, applications, and accounts you own or are explicitly authorized to test. HTTPS interception can expose passwords, tokens, messages, and personal data; use a test account, isolate the device, and remove temporary certificates when finished.
Choose the right Android traffic-capture method
| Method | Best for | What you can see | Main limitation |
|---|---|---|---|
| Android Studio Network Inspector | An app you develop and can run in a debuggable build | Supported app-level requests and transfers | Unsupported request types may not be identified; it is app-focused rather than a device-wide sniffer. |
| Android System Proxy plus a debugging CA | Browser traffic, an emulator, or apps that honor the system proxy | HTTP and HTTPS requests and responses after certificate trust is established | Certificate installation is required for HTTPS; pinning and app policy can prevent decryption. |
| mitmproxy regular proxy | Interactive interception, replay, and modification | HTTP(S) flows that use the proxy and trust mitmproxy’s CA | Some Android apps bypass operating-system proxy settings. |
| mitmproxy TUN or another lower-level capture | Apps that bypass an HTTP proxy or traffic that needs broader packet visibility | Lower-layer traffic and metadata, with visibility depending on the protocol | Packets, IP addresses, or TLS handshakes do not guarantee readable HTTPS bodies. |
adb-assisted physical-device workflow |
Repeatable debugging on a real phone | Device connection, logs, forwarding, and support for the proxy or capture tool you select | USB debugging must be authorized, and a charging-only cable cannot carry the data connection. |
1. Inspect your own app with Android Studio
Network Inspector is the least invasive choice when the question is “what is my app sending and receiving?” It is designed to examine data transfers from an app you develop, rather than to monitor every application on the device.
- Run a debuggable build of your app on a connected device or emulator.
- In Android Studio, open View > Tool Windows > App Inspection.
- Select the running process and open the Network Inspector.
- Reproduce the action you are debugging—open a screen, submit a form, refresh data, or upload a test file.
- Inspect the requests and transfers that the inspector identifies, including timing and payload details exposed by the supported client stack.
If the panel is empty or only shows part of the activity, do not assume the app made no network calls. The inspector may not identify unsupported request types. Move to a proxy or packet-level method when you need broader coverage, or instrument the specific networking code in your debug build.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitches#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
2. Capture browser or emulator traffic with the Android System Proxy
For a browser session or an emulator, Android’s System Proxy is the normal debugging path. It is distinct from the emulator’s lower-level proxy setting: the system proxy is intended for application debugging with tools such as Charles or mitmproxy.
Configure the interception tool
- Start your interception tool on the computer and note its listening address and port.
- Make the listener reachable from the emulator or device. A listener bound only to the computer’s loopback interface will not be reachable from a separate Android network namespace.
- In Android’s network settings, edit the active Wi-Fi network and set the proxy to the computer’s address and the tool’s port. On an emulator, use the emulator’s documented networking address for the host computer when required by that emulator image.
- Open a non-sensitive test URL and confirm that a plain HTTP request appears in the tool before troubleshooting TLS.
Keep the proxy enabled only for the test session. Leaving it configured can break ordinary browsing when the computer is offline or the listener is stopped.
Install the proxy CA for HTTPS
A proxy can show that an HTTPS connection was attempted while still being unable to read the URL path, headers, request body, or response. The reason is TLS: the client must trust the proxy’s CA before the proxy can generate a substitute certificate and decrypt the flow. Follow the interception tool’s Android certificate-installation procedure, then retry with a test site.
Android distinguishes user-installed certificates from certificates in the system store. Many applications trust the system store but do not trust user-added CAs. If an application you own requires system-store trust in an emulator or test device, use an appropriate test image and the tool’s documented system-certificate workflow. Do not modify a production phone to defeat another person’s security controls.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
3. Make an app you control trust a debugging CA
For your own application, prefer a debug-only network security configuration rather than weakening release behavior. Android’s Network Security Configuration supports <debug-overrides> trust anchors. A qualifying debug trust anchor can also disable certificate pinning for that debug connection, which is useful when an interceptor presents its own certificate.
Keep the override out of release builds
- Put the additional trust anchor in the debug configuration or debug manifest variant.
- Leave the release configuration unchanged, including its normal certificate policy and any pins.
- Use a separate test endpoint and credentials so captured material cannot be reused in production.
- Remove the debug CA and uninstall the test configuration after the session.
If the application uses certificate pinning outside the qualifying debug path, installing a user CA alone will not make the connection decryptable. A failed handshake, a connection reset, or a request that never reaches the proxy is consistent with pinning or another trust policy.
4. Capture traffic from a physical Android phone
You do not need a USB cable to capture an emulator’s traffic. A real phone is different: a cable is the practical way to establish the computer-to-device connection used by adb, unless you deliberately use another supported network debugging arrangement.
- On the phone, enable Developer options and then USB debugging.
- Connect a compatible, data-capable USB cable. A cable that supplies power only will not provide the debugging link.
- Accept the computer’s debugging authorization prompt on the phone.
- Run
adb deviceson the computer and verify that the device is listed as authorized rather than offline or unauthorized. - Configure the phone’s Wi-Fi proxy to the interception computer, install the tool’s CA when HTTPS decryption is needed, and reproduce the request.
- Use
adbfor the device connection, logs, or forwarding functions required by your capture tool. The bridge transports debugging data; it does not decrypt TLS by itself.
If the phone is not detected, try a different USB port and a known data cable, unlock the phone, re-check the authorization dialog, and verify that the Android platform tools are installed. Fix device detection before changing TLS settings.
Recommended Free Tools
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere — perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style — just close the grip, press down, twist 90°, and snap on a new top.
- Black PopSockets: Simple, refined, and endlessly versatile — a timeless essential for any phone.
- PopSockets Ecosystem: Mix and match your favorite PopSockets products — from grips and wallets to cases and mounts — all designed to work together seamlessly.
5. When an app ignores the proxy
Android applications can bypass operating-system HTTP proxy settings. Common symptoms are that the browser is visible in the interceptor but the target app produces no flow, or that only DNS and connection attempts appear.
Use a mode that sees traffic below the HTTP proxy
mitmproxy’s TUN mode and other lower-level capture paths route traffic at a broader network layer. They are appropriate when an app does not honor the system proxy. They do not automatically solve encryption: a TUN capture can show endpoints, ports, packet timing, or a TLS handshake while the application payload remains encrypted.
Check the app’s own networking policy
- Confirm that the app is using the device network rather than a separate VPN or private tunnel.
- Check whether the app uses certificate pinning or rejects user-installed CAs.
- For an app you own, test the debug-only trust override described above.
- For an app you do not own, stop rather than attempting to bypass its protections without written authorization.
How HTTPS visibility actually works
There are three separate checkpoints, and confusing them causes most failed captures:
- Routing: the device or app must send traffic through the capture path. A proxy setting that the app ignores fails here.
- Trust: the client must trust the interceptor’s CA. Without that trust, the proxy cannot present a certificate the client accepts.
- Policy: certificate pinning, a custom trust manager, or another application rule must permit the substituted certificate. A debug-only configuration can relax this for an app you control; it must not be carried into release.
When all three pass, the tool can display decrypted HTTP requests and responses. If only routing passes, you may see connection metadata but not contents. If trust or policy fails, expect TLS errors, resets, or an apparently missing request.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
Read captures without leaking sensitive data
- Use test accounts and synthetic identifiers; redact authorization headers, cookies, session IDs, and personal fields before sharing a capture.
- Record the device model, Android version, app build, proxy mode, and CA location alongside the capture so another developer can reproduce it.
- Compare timestamps at the device and proxy. Clock differences can make a correctly captured request look out of order.
- Expect compressed, binary, streaming, or encrypted application payloads to be hard to interpret even after TLS is decrypted.
- Turn off the proxy and remove the debugging CA when the test ends.
Troubleshooting: symptom, cause, and fix
No traffic appears anywhere
- Cause: the listener is stopped, the host or port is wrong, or the device cannot reach the computer.
- Fix: verify the listener first, confirm the proxy address and port, and test a simple HTTP request from the browser.
The browser is visible but the app is not
- Cause: the app bypasses the operating-system proxy or uses a private tunnel.
- Fix: use the app’s supported debug configuration, then try TUN or another lower-level capture mode for an authorized test.
HTTPS connections appear, but bodies are unreadable
- Cause: the CA is missing from the store the app actually trusts, or certificate pinning rejects the interceptor.
- Fix: install the CA in the correct test-device store; for your own debug build, add a debug-only trust anchor and verify that release policy was not changed.
Network Inspector is blank or incomplete
- Cause: the app is using a request type the inspector does not identify.
- Fix: use a proxy for HTTP(S) coverage or a lower-level capture when the request never enters a supported inspector path.
The physical phone shows as unauthorized or offline
- Cause: USB debugging authorization was not accepted, the phone is locked, or the cable is power-only.
- Fix: unlock and re-authorize the computer, reconnect with a data-capable cable, and check the
adbdevice state before investigating certificates.
Captures are slow or unreliable
- Cause: interception adds a network hop, TLS handshakes are repeated, or the emulator and proxy computer are resource-constrained.
- Fix: capture only the needed host or time window, avoid loading unrelated pages, keep the emulator and proxy on a stable network, and use a physical device when emulator behavior is the variable under test.
Performance, reliability, and cost considerations
Android Studio is usually the quickest option for one app because it avoids configuring a device-wide proxy. A proxy gives broader protocol visibility but adds setup and an extra hop. TUN or packet capture covers more applications, yet interpretation becomes protocol-dependent and encrypted payloads may remain opaque. Local tools such as Android Studio, adb, and mitmproxy do not charge per request; your practical costs are development time, test-device access, and any lab or network resources you choose.
For repeatable tests, keep a dedicated emulator or test phone, a documented debug CA, a known proxy port, and a reset procedure. Recreate the same app build and network policy before comparing two captures; changing the CA store, pinning policy, or proxy mode changes what “missing traffic” means.
Or skip the browser setup
If what you actually need is a clean image or PDF of a rendered webpage—not the app’s raw HTTP request stream—ScreenshotNeo can do that with one request. It accepts a URL and returns a PNG, JPEG, WebP, or PDF. It is not a replacement for Android traffic interception, but it avoids installing a browser proxy when the deliverable is a page image.
ScreenshotNeo removes cookie or consent banners, newsletter popups, and chat widgets before capture. Bot checks, blank pages, failed loads, timeouts, and cache hits are not billed, and each response reports the page verdict and billing status in headers. Its MCP server provides take_screenshot, get_page_info, and capture_pdf tools for Claude, Cursor, and other MCP clients. The Free plan includes 1,000 screenshots per month with no card; paid plans start at $5 for 3,000 shots. Every feature is available on every plan.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →See the ScreenshotNeo documentation for parameters and authentication. The following calls are runnable; replace the target URL and API key as needed.
Best Value
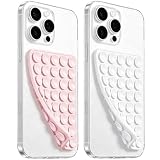
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
cURL
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpPython
import requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)
Node.js
const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);
Create a free ScreenshotNeo account to get 1,000 screenshots a month with no card.
FAQ
Can a USB cable decrypt HTTPS by itself?
No. It provides the adb data connection for a physical phone; HTTPS readability still depends on proxy routing, CA trust, and the app’s security policy.
Is an emulator required?
No. An emulator is convenient for repeatable tests, while a physical phone is useful when hardware-specific behavior matters. The capture method must match the device and app’s proxy behavior.
What should I do with a debugging CA after testing?
Remove it from the test device and disable the proxy. Keeping an interception CA installed increases the chance that later traffic is inspected unintentionally.
Frequently Asked Questions
Can a USB cable decrypt HTTPS by itself?
No. It provides the adb data connection for a physical phone; HTTPS readability still depends on proxy routing, CA trust, and the app’s security policy.
Is an emulator required?
No. An emulator is convenient for repeatable tests, while a physical phone is useful when hardware-specific behavior matters. The capture method must match the device and app’s proxy behavior.
What should I do with a debugging CA after testing?
Remove it from the test device and disable the proxy. Keeping an interception CA installed increases the chance that later traffic is inspected unintentionally.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

