
Android Keystore, key attestation, Play Integrity, and Android Management API securityPosture answer different security questions; they are not interchangeable root-check libraries. Keystore governs how an app uses keys on a device, attestation lets a server verify claims about a key, Play Integrity evaluates an app request’s environment, and security posture reports on a managed device. Choose based on what you need to protect and where you can make a trusted decision.
Which Android security mechanism answers your question?
| Mechanism | Primary question | Where the decision is made | Coverage variables | Main limitation |
|---|---|---|---|---|
| Android Keystore | Can the app use a key without exporting its material, and under what restrictions? | On the device, by Keystore and any supporting secure hardware | Android version and target API, device hardware, supported algorithm, mode and digest, and StrongBox availability | A Keystore key is not automatically hardware-backed; support depends on the exact key configuration. Android Keystore documentation. |
| Key attestation | Can a remote party verify claims about a generated key and its attestation chain? | A trusted remote server | Device attestation capability, certificate chain and root, provisioning, and revocation status | Certificate and extension validation must be correct; an on-device verifier can be compromised. Key attestation guidance. |
| Play Integrity | Does a request appear to come from the expected app, account, and device environment? | App backend, after receiving a Google-provided verdict | Google Play ecosystem, request mode, Android generation, verdict tier, and available signals | It is one anti-abuse signal, not a universal guarantee; verdict tiers and signals vary. Play Integrity overview. |
Android Management API securityPosture |
What security posture does a managed device report? | Management backend or API consumer | Management enrollment and context, hardware-backed evaluation availability, and returned posture details | Software evaluation can be less trustworthy; interpret details instead of reducing results to a binary label. Android Management API reference. |
The practical distinction is scope: a key, an app request, or a managed device. Keystore is principally about local key custody and use. Attestation supplies evidence about a key for a remote verifier. Play Integrity provides verdicts relevant to a particular app interaction. Management posture evaluates a device in a management context.
How do I check if Android Keystore is hardware backed?
Android Keystore was introduced in Android 4.3 (API level 18), according to the Android Developers documentation. Its key material is not exposed to the app process during cryptographic operations, but that fact alone does not establish that a key resides in secure hardware. Hardware binding depends on the device and whether its secure hardware supports the key’s specific algorithm and configuration.
- For an app targeting Android 10 (API level 29) or later, inspect
KeyInfo.getSecurityLevel(). A trusted environment or StrongBox security level indicates secure-hardware residency. - For older-target compatibility, Android’s guidance uses
KeyInfo.isInsideSecurityHardware(). - Check the result for the actual generated key and configuration; do not infer hardware backing merely from using the Keystore provider.
When creating or importing a key, Keystore lets the app constrain allowed algorithms, operations, validity periods, and user-authentication requirements. Those restrictions govern key use; they do not guarantee that every requested configuration is available in secure hardware.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
Does Android support StrongBox on every device?
No. StrongBox is optional. Android’s documentation says StrongBox KeyMint can be included on devices running Android 9 (API level 28) or higher; that is a platform possibility, not a promise that every device has it. StrongBox implementations use embedded secure elements or integrated Secure Enclaves and provide stronger isolation and tamper resistance than a trusted execution environment (TEE). See Android’s Keystore and StrongBox guidance.
StrongBox supports a narrower set of algorithms and configurations, is slower, and supports fewer concurrent operations than TEE-backed Keystore. Check for FEATURE_STRONGBOX_KEYSTORE before relying on it, and handle StrongBoxUnavailableException when requesting StrongBox for a key.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
If StrongBox is unavailable, generating or importing a key without a StrongBox requirement is a fallback only if it fits the threat model. Treat the resulting key according to its actual security level; never label a fallback key StrongBox-backed.
What does key attestation prove, and where should it be verified?
Key attestation gives a remote party evidence about an asymmetric key generated on a device and associated security properties. Android introduced key attestation in Android 7.0; its documentation notes that attestation was not required until Android 8.0, so the API’s introduction does not mean uniform availability across devices. Android Open Source Project attestation documentation.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
Verification belongs on a trusted server, not on the potentially compromised device. Android’s verification guidance says, “Don’t complete the following validation process on the same device.” A server-side validation flow should:
- Receive the generated key’s certificate chain from the app.
- Validate the chain against an appropriate trusted root and verify every signature.
- Check revocation status using current operational data.
- Locate and parse the trustworthy attestation extension, then compare its challenge and other values with the server’s expected challenge and policy.
Attestation root certificates and revocation information need operational maintenance. A locally successful check is not a substitute for server verification when the device itself is within the threat model.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
Can Play Integrity detect root?
Play Integrity evaluates multiple signals about an app, account, and device. Its device verdicts can reflect device integrity, but a verdict should not be treated as a universal root detector or as proof that a device is safe or malicious. The result depends on Android version, verdict tier, and available signals.
Google documents conditional hardware-backed behavior: on Android 13 and later, MEETS_STRONG_INTEGRITY requires recent security updates. On devices before Android 13, MEETS_DEVICE_INTEGRITY and MEETS_STRONG_INTEGRITY rely on hardware-backed signals; the pre-Android-13 MEETS_DEVICE_INTEGRITY verdict can fall back to software-backed attestation. Consult the current Play Integrity documentation before setting policy around a verdict.
Best Value
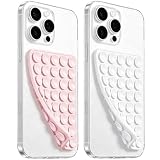
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Play Integrity also offers verdicts covering recognized app identity and integrity, account or app acquisition details, and optional areas such as app access risk and Play Protect. These signals help a backend evaluate a protected request; they do not replace other anti-abuse controls. Google recommends using the API alongside other signals, gathering telemetry before enforcement, and estimating how a policy would affect the existing install base. Standard requests are described as lower-latency and reliable for on-demand checks, so select a request strategy that fits the action being protected.
What does Android Management API security posture tell you?
The Android Management API’s securityPosture evaluates the current status of a managed device. Factors can include root access or a custom ROM. The response includes devicePosture and postureDetails; a securityRisk detail can explain why a device is not considered fully secure.
Where hardware-backed key attestation cannot be used, the API may rely on software checks and can report HARDWARE_BACKED_EVALUATION_FAILED. That is a meaningful distinction: a failed hardware-backed evaluation may leave a software-based evaluation, which is less trustworthy. The API documents mappings to Play Integrity verdicts, but a management posture result and an app backend’s decision about a request remain different product decisions. Review the security posture response reference.
Is SafetyNet still supported?
The available official Android search result indicates that the SafetyNet API is being deprecated, but the referenced blog page could not be verified here. That does not establish a precise retirement date or transition schedule. For new integrity checks, consult Google’s Play Integrity API documentation and verify the current status of any existing SafetyNet integration against official Android guidance before changing production behavior.
How should you choose?
- Choose Keystore when the requirement is to keep key material out of the app process and constrain its use on-device.
- Use key attestation when a server needs verifiable evidence about a generated key, and implement chain, extension, challenge, and revocation checks on that server.
- Use Play Integrity when an app backend needs signals to evaluate a request or risky interaction; set policy in light of the Android version and verdict tier.
- Use Android Management API posture when evaluating devices in a managed-device context, and preserve the distinction between hardware-backed and software-based evaluation.
These mechanisms can complement one another when a system has multiple security needs, but they are not interchangeable. The right combination depends on the asset at risk, where a trustworthy decision can be made, device compatibility, and the cost of rejecting legitimate users.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

