
The safest way to update an IoT device is to authenticate the update, verify it on the device before installation, deploy it to a small test group first, monitor device health, and have a tested recovery route. The right mechanism depends on the device’s memory, power, connectivity, bootloader, and the team’s ability to operate the update service—not on one universal OTA method.
Choose an update method that fits the device and the fleet
Over-the-air (OTA) updating is a way to deliver software remotely, usually over a network. It is also a security-sensitive code-execution path: an update system that accepts an untrusted image can give an attacker control of a device. Choose the approach only after checking hardware and operational constraints.
- Device constraints: hardware revisions, available flash and RAM, battery or power limits, radio type, and the bootloader’s ability to validate, select, or recover firmware.
- Connectivity: whether devices are regularly online, can maintain a connection during transfer, and can report progress and health after reboot.
- Fleet operations: whether you need remote targeting, staged deployment, per-device status, audit records, and centralized controls.
- Support obligations: device lifetime, security-update expectations, regulatory or recertification implications, and the recovery options available when a device stops communicating.
RFC 9019, published by the IETF in April 2021, describes an architecture for firmware updates over the air. It is an informational RFC, not an Internet Standards Track requirement. Treat it as a design reference rather than a certification or compliance checklist.
Compare the main patterns
| Pattern | Best fit | Trade-offs |
|---|---|---|
| Managed cloud orchestrator with a device agent | A fleet needs remote targeting, job tracking, and centralized rollout controls. | Depends on service availability, compatible device agents, connectivity, and a viable operating cost and lifecycle. Confirm that the service supports the target devices and required recovery workflow. |
| Device-hosted update client with a signed manifest and image | A team needs direct control over transport, update policy, or behavior on constrained devices. | The team must build and operate signing, trust-anchor provisioning, retry logic, status reporting, boot verification, and recovery. |
| Local or removable-media update and wired recovery | Devices are intermittently connected or need a fallback after a failed network update. | Usually requires physical access and hardware and bootloader support; it is not a hands-off OTA process. |
Documented examples of managed services include AWS IoT Jobs and FreeRTOS OTA, and Microsoft Device Update for IoT Hub. Vendor documentation describes particular product behaviors; it does not establish feature parity between services or compatibility with every device. Compare supported agents, signing and manifest workflows, rollout controls, monitoring, recovery, lifecycle, geographic availability, and current cost before selecting a service.
#1 Best Overall

- 𝐄𝐚𝐬𝐲 𝐒𝐞𝐭𝐮𝐩 𝐈𝐧𝐝𝐨𝐨𝐫/𝐎𝐮𝐭𝐝𝐨𝐨𝐫 𝐂𝐚𝐦𝐞𝐫𝐚 — 2.5K HD video, vibrant color night vision and IP66, ensuring you never miss a moment, day or night,rainy or sunny. With dual-band 2.4G/5G WiFi & Plug and play setup of the cameras for home security - just download app and scan QR code! No tools needed for tabletop use, mounting screws included for walls
- 𝟐.𝟓𝐊 𝐐𝐇𝐃 & 𝐂𝐨𝐥𝐨𝐫 𝐍𝐢𝐠𝐡𝐭 𝐕𝐢𝐬𝐢𝐨𝐧 — Experience crystal-clear visibility day and night with full-color night vision enhanced by a built-in white light. Perfect as a baby monitor, pet camera, or security camera to monitor your home inside and out
- 𝐒𝐦𝐚𝐫𝐭 𝐀𝐈 𝐃𝐞𝐭𝐞𝐜𝐭𝐢𝐨𝐧 & 𝐀𝐥𝐞𝐫𝐭𝐬 — Stay informed about what matters most with human/motion/sound detection up to 33 feet away. The camera deters intruders with flashing lights and a siren while sending instant alerts to your phone — keeping you one step ahead of any suspicious activity. Call +1 (978) 437-5767 for expert support with setting up and optimizing Vimtag cameras, available Monday to Friday, 9:00 AM - 6:00 PM (ET)
- 𝐄𝐧𝐡𝐚𝐧𝐜𝐞𝐝 𝐓𝐰𝐨-𝐖𝐚𝐲 𝐀𝐮𝐝𝐢𝐨 - Communicate effortlessly with guests or check in on pets using the upgraded two-way audio feature of this indoor camera, allowing you to see, hear, and speak from anywhere
- 𝐓𝐰𝐨 𝐑𝐞𝐜𝐨𝐫𝐝𝐢𝐧𝐠 𝐎𝐩𝐭𝐢𝐨𝐧𝐬 & 𝐑𝐞𝐚𝐥-𝐓𝐢𝐦𝐞 𝐒𝐡𝐚𝐫𝐢𝐧𝐠 - With the mobile app, you can access the baby camera's video anytime, anywhere, view real-time footage, and even share monitoring content with family, keeping you informed about your home dynamics while you're away.Enjoy secure cloud recording with Vimtag Cloud (subscription required) for detecting people, sounds, motion. Alternatively, you can insert a microSD card (sold separately) for local video storage
Build verification and recovery into the update design
Do not treat an encrypted connection as proof that the firmware itself is trustworthy. Protect the connection and authenticate the people and systems that authorize deployments, but also have the device verify the update artifact before installation. NIST’s IoT Device Cybersecurity Requirement Catalog lists signatures, checksums, and certificate validation as examples of ways to verify update source and integrity. Where the design supports secure boot, verify the image again during boot.
Use protected metadata and authorized signers
A manifest or equivalent metadata can identify the image, its version, when and how it should be applied, and where it is obtained or stored. Protect both the metadata and firmware: an attacker who can alter instructions may be able to redirect or misuse an otherwise valid image. Keep manifest parsing and trusted boot components as small and carefully reviewed as practical, especially on constrained devices.
Define which signing keys are trusted, which signers may authorize updates for each device or component, and how keys are rotated or revoked. Restrict deployment permissions as well as artifact access. For example, AWS’s FreeRTOS OTA documentation describes TLS mutual authentication and message authorization alongside firmware signing and device-side integrity checks; transport security and artifact verification serve different purposes.
Prevent unsafe downgrades
A correctly signed older image may still contain a known vulnerability. Enforce a version or security policy that prevents an attacker or mistaken deployment from reinstalling firmware that the device should no longer accept. The policy must account for legitimate recovery: decide which older versions, if any, can be installed through an authorized recovery process.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #2
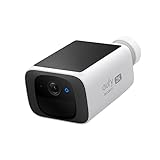
- Continuously Powered by Solar: Just 3 hours of sunlight is enough to keep the camera running. The tiny size and wire-free design allow it to be installed anywhere.
- Day and Night Clarity: Enjoy clear black-and-white night vision thanks to infrared LEDs and an f/1.6 aperture. Please note that spotlight color night vision is not supported.
- Easy Installation: Use anywhere thanks to its tiny size and wire-free design. Drill one hole, once.
- Human Detection: Al alerts you to anyone in your yard, whether family, a courier, or a stranger. Connect to HomeBase 3 for individual facial recognition.
- No Monthly Fee: One-time purchase. No monthly fees or hidden costs. On-device storage and AI for complete security and transparency.
Choose a recovery mechanism before deployment
Recovery depends on the hardware. Options include retaining a known-good image, using multiple firmware slots or partitions, or providing a separate recovery image or path. A/B or multi-partition updates require enough flash and a bootloader able to select a valid image; do not assume either capability exists. RFC 9019 discusses serial, USB, and wireless recovery routes, but the device must support the relevant interface and procedure.
For an intermittently connected device, plan how an operator can reach it if a failed update prevents normal network communication. A wired or removable-media route may help, but it requires compatible hardware and often physical access. If serial recovery is explicitly supported, a USB-to-UART adapter may be useful; confirm the device’s voltage levels, pinout, and model-specific instructions before connecting one.
Prepare and release updates in controlled stages
Use this release workflow for either a managed service or a device-hosted updater. Exact menu names and device-agent steps differ by platform, so validate them against the chosen vendor documentation and the device’s implementation.
- Inventory the fleet. Record device models and hardware revisions, current firmware, update agent, available flash, connectivity and power constraints, and support lifetime. Identify which devices can install and recover the proposed image.
- Build and authorize the release. Produce the firmware image and protected metadata. Provision trust anchors securely, define which signer is authorized for each device or component, and set version and anti-rollback rules where supported.
- Test on representative hardware. Exercise realistic low-power operation, interrupted network transfers, and storage-failure conditions. Test the installation, successful boot, failure detection, and recovery route—not just whether a transfer completes.
- Communicate the change. Tell customers or operators what the update changes, its criticality, recommended installation timing, prerequisites and dependencies, and possible effects. NIST Federal Profile 8259A calls for update information of this kind and for testing effectiveness and side effects.
- Deploy to a canary group. Select a small, representative set of devices rather than starting with the whole fleet. Track per-device job status, whether each device boots successfully, relevant health signals, error rates, and deployment telemetry.
- Pause or recover if the canary fails. Set decision thresholds before rollout. If devices fail to install, boot, or meet health expectations, pause expansion and use the recovery or rollback controls appropriate to that hardware and service.
- Expand by cohorts and retain records. Increase deployment groups only after the previous group behaves as expected. Preserve the artifact and version, target group, start and end states, and failures so the rollout can be audited and diagnosed.
- Publish remediation expectations. Explain how vulnerabilities can be reported, how updates will be communicated, and what timing, prerequisites, and impacts customers should expect.
AWS IoT Lens recommends incremental device groups and monitored deployments, and advises that updates be controlled and reversible. Rollback is not a generic button: it depends on device boot behavior, retained images or recovery options, and the deployment mechanism.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Rank #3

- High-definition pan and tilt camera: Capture every detail in pristine 1080p HD quality, from any angle, with the Energizer Connect security camera's 355-degree horizontal and 48-degree vertical pan and tilt capabilities.
- Night Vision Equipped: Camera has 4 led lights and 4 IR lights that switch automatically depending on the lighting conditions, allowing you to see color at night or black and white in total darkness.
- Two-Way Audio: Allowing you to listen and talk to the person in the video, using the built-in microphone and speaker, or siren alarm to deter intruders.
- Flexible Storage Options: Choose cloud storage with a complimentary 30-day trial or utilize a micro SD card (up to 128GB, not included) for local recording.
- 2.4GHz Wi-Fi Compatible: Connects to your 2.4ghz wifi network, which is the most common wifi frequency. It does not support 5ghz wifi networks.
Account for power, storage, and connectivity limits
Firmware transfer and flash writes consume energy and storage. Choose chunk sizes, retry behavior, and update windows based on the device’s actual radio, flash, power source, and connection reliability. A strategy that works on a powered device with stable broadband may be unsuitable for a battery-powered sensor on a lossy link.
Plan for interrupted transfers and devices that cannot report status continuously. The device should be able to resume or safely restart according to its design, and the operator needs a way to distinguish a slow or disconnected device from a failed installation. Test these behaviors on representative hardware rather than assuming the cloud service’s job status proves the image booted correctly.
Separate firmware releases from routine operations that do not require new code. AWS IoT Lens, for example, advises using configuration or device-management operations for tasks such as certificate rotation where appropriate, instead of rebuilding and distributing firmware unnecessarily.
What managed services document—and what they do not guarantee
Vendor documentation can help establish whether a service offers the controls your fleet needs, but it is not a guarantee that every hardware target, agent, region, or recovery path is supported. Product details can change; confirm current compatibility and lifecycle terms with the vendor before deployment.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →- AWS IoT Jobs: AWS IoT Lens describes targeting devices, tracking job execution, versioning artifacts and manifests, deploying to incremental groups, and using known-safe fallback versions and rollback practices.
- FreeRTOS OTA: AWS documentation describes signing, device-side verification, delivery over HTTP or MQTT depending on configuration, deployment to one or more devices, progress monitoring, and failure debugging. These are documented FreeRTOS/AWS behaviors, not universal OTA guarantees.
- Microsoft Azure: Microsoft’s IoT security guidance names Device Update for IoT Hub and recommends secure update paths and cryptographic assurance of firmware versions. Check Microsoft’s current documentation for supported-device and service details.
Microsoft also recommends using device protections such as secure boot and hardware-backed secret storage where feasible. Whether those are available depends on the device design.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

