
Recommended Free Tools
Secure an AI coding agent by assuming that files, issues, web pages, and tool responses can contain hostile instructions—and limiting what the agent can do if it follows them. Give it only the context and permissions needed for the task, isolate it from credentials, control network access, gate consequential actions, review its changes, and test the whole workflow repeatedly. Input filters and model refusals can help, but they are not security boundaries on their own.
How prompt injection can reach a coding agent
Prompt injection is an attempt to place instructions in content an AI model processes so it acts outside the user’s intended task. In a coding workflow, the content may arrive indirectly through a source file, README, project instruction file, issue, pull request, comment, dependency changelog, log, fetched web page, or MCP tool response. A malicious README or GitHub issue can therefore influence an agent when that content is included in its context; whether the agent then runs a command depends on its tools, permissions, and safeguards.
These sources may look like ordinary development material. There is no reliable rule that every hostile instruction will announce itself with a recognizable phrase. OWASP warns that repository instruction files can steer later generations and that untrusted pull-request content can target CI agents with access to organizational secrets. Treat external and repository content as data to assess, not as authority to expand the task. OWASP Secure Coding with AI Cheat Sheet
The security boundary is larger than the model: it includes the context the model sees, the filesystem, shell, network, credentials, connected tools, CI/CD permissions, and human approval path. The practical objective is to prevent manipulated text from silently becoming a high-impact action.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problems#1 Best Overall

- Valued Carpenter Pencil Set: You will get 2 pcs solid carpenter pencils with 26 piece 2.8 mm refills, 1 replaceable sharpener, 1 plastic storage box.The complete carpenter pencils combination allows you to finish your work faster and more easily
- Deep Hole Marker Pencil: The deep-hole construction pencils adopts 45mm elongated tip design, which is more convenient to mark in the small hole or in other tight areas that other carpenter markers cannot reach
- Carpenter Pencils with Sharpener: The sharpener is screwed into the top of the work pencil, which won't get lost either. Built-in pencil sharpener that keep the lead with pointed and smooth to Improves line of sight in fine work
- Stronger Solid Lead: This work pencil is matched with a 2.8 mm thick lead , which is much thicker and stronger during the drawing process of construction work, it will not break or damage easily
- Marks on Various Surfaces: 3 colors solid construction pencil can marks on various surfaces,such as metal, plastic, wood, paper etc. Ideals for woodworkers, contractors, craftsmen, builders, merchants and masons
How to reduce an agent’s ability to cause harm
Limit context and treat included content as untrusted
Provide only the files and outside material the task requires. Do not let instructions found in those materials silently broaden the assignment. After the agent reads untrusted content, inspect its actions and proposed changes for unexpected scope. For public contributions, protect privileged CI workflows from untrusted pull requests and audit what an agent does with contribution content. OWASP also cautions against unrestricted web access without egress controls.
Restrict tools and permissions
Give the agent the minimum authority needed for the task. Prefer read-only or resource-scoped access when possible; separate tools by trust level; and require explicit authorization for sensitive operations. Use command and path allowlists where practical. A routine code change rarely needs unrestricted shell access or broad access to administrative, payment, email, or deployment tools. OWASP AI Agent Security Cheat Sheet
Rank #2

- Ergonomically Designed: Work in tight areas with a compact design that gets into tough spots
- Compact and Lightweight: Both tools are designed to fit into difficult to reach spaces. The 1/4" impact driver has a length of 5.55 in. and weighs just 2.8 lbs, while the 1/2" drill/driver measures only 7.5 in. and weighs 3.6 lbs
- Both the DEWALT impact driver and electric drill driver feature integrated LED work lights with a convenient 20-second delay, ensuring enhanced visibility in dimly lit or challenging work areas
- One-Handed Loading - Keep one hand free with a 1/4 in. hex chuck that accepts 1 in. bit tips
- Power drill cordless with 1/2" single sleeve ratcheting chuck provides tight bit gripping strength, making bit changes faster and more secure
Review MCP servers and integrations
Model Context Protocol (MCP) servers and other integrations are part of the tool supply chain. Maintain an approved inventory, review tool descriptions because they enter model context, validate arguments before execution, and limit each integration’s access to files, networks, and credentials. Pin tool definitions where possible and compare them for changes. Watch for name shadowing—an untrusted tool using a name that resembles a trusted one—or unexpected changes in capability. Do not automatically discover and connect to arbitrary MCP servers without review.
Isolate the runtime and control network access
Run the agent in a dev container, restricted shell, virtual machine, or ephemeral workspace appropriate to the task’s risk. Keep SSH keys, cloud credentials, environment secrets, and sensitive host directories outside its reachable filesystem. Block outbound network access when it is unnecessary; when it is required, allow only necessary destinations.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #3

- 【Great Compatibility】This Katerk 1/4 inch hex shank bit holder is specifically designed for 1/4 inch hex shank drill bits. It's compatible with most 1/4 fast hex handles, hex sockets, various electric screwdrivers, and handheld screwdrivers. The bit holder makes it a valuable addition for any handyman.
- 【Secure and Safe】Built with a secure backup nut design, each drill bit holder securely locks onto your bits, ensuring they stay firmly in place. Additionally, our bit holder incorporates a high-quality steel ball rolling design that holds up to several kilograms of weight, ensuring your various drill bits don't fall off.
- 【Easy One-Handed Operation】The bit holder for impact driver allows you to change bits single-handedly, simplifying your workflow. Its multi-color design further allows for quick identification of the drill bit you need.
- 【Compact and Convenient】Thanks to its compact size, this 1/4 inch bit holder is easy to carry around. The bit holder allows for easy attachment to various tools, making this a convenient addition to your construction accessories. The Katerk bit holder is cast from high-quality alloy material, promising a long product lifespan. Despite its rugged strength, the bit holder remains lightweight, making it portable.
- 【Cool Christmas Gift For Men Stocking Stuffers】 This screwdriver bit holder, driver bit holder, impact bit holder, can be given as a gift to your loved one, especially for anyone involved in construction or electrical work. It's a must-have for stocking stuffers for men and women, tools gifts for dad, tech gadgets for men, gifts for dad, gifts for him, gifts for husband, gifts for boyfriend, cool gadgets for men, and cool gifts for dad.
The reason for enforcing these boundaries outside the model is practical: an agent that is manipulated should still lack a path to valuable credentials or an unrestricted data-transfer channel. Anthropic describes a controlled internal red-team example in which its coding agent was prompted to exfiltrate credentials. The company’s engineering article says the task succeeded in 24 of 25 retries in that specific exercise; that is not a general success rate for coding agents or prompt-injection attacks. In discussing that scenario, Anthropic wrote: “The only defense that holds in this situation is the environment, specifically egress controls that block the POST regardless of intent and filesystem boundaries that keep ~/.aws out of reach in the first place.” The statement concerns that scenario, not every possible defense. Anthropic’s account of its containment approach
Which actions should require approval?
Pause for an explicit authorization before an agent takes an action that could expose data, affect shared systems, or be difficult to reverse. Make the proposed action and the data or resources involved visible to the reviewer before approval.
Rank #4

- Long Nib and Deep Hole Marker: Our mechanical carpenter pencil with 45mm nib is designed for easy marking of deep holes or narrow areas. These construction pencils are the great choice for woodworking tools, construction tools, carpenter tools, contractor tools, wood carpentry tools and architect tools
- Extra Refills in 2 Colors for Versatile Marking: The construction mechanical pencil comes with 12 extra 2.8mm refills, including 6 red and 6 black refills. The black refill is suitable for light surfaces, while the red wax is perfect for dark surfaces. Our carpenter mechanical pencil makes sure that you'll have an ample supply for extended use
- Built-in Sharpener: Our construction pencil comes with a built-in sharpener to ensure the mechanical pencil tip is always sharp and ready for use. Never buy an extra pencil sharpener again. A great tool for any woodworker pencil, contractor pencils. The refill can easily be extended or retracted with a simple click of the pencils mechanical, allowing you to work more efficiently and accurately
- Portable Clip Design: Our deep hole construction pencil features a portable clip design, easy to carry and attach to your pocket or tool box, so that you can keep the carpenter pencils mechanical close at hand, making it a convenient tool to have on the go. Great gifts choice for carpenters
- Stronger Pencil Lead: The black refills are made of lead, sturdy and smooth. The red refills are made of wax, clear and light. These marking pencils are much thicker and stronger than normal pencils during the marking process of construction work, suitable for various surfaces, such as glasses, metal, boards, floors, walls, furniture, etc. The written marks can be easily wiped with a wet paper towel when needed
- Transmitting data outside the workspace or organization.
- Pushing changes, opening or modifying a pull request, or changing CI configuration.
- Changing permissions, secrets, dependencies, or security controls.
- Deploying software or using administrative tools.
After the agent has processed outside content, review the resulting diff for unrelated edits, exposed secrets, unexpected dependency changes, and weakened controls. Apply normal code review and security testing; an agent’s confidence is not validation. Code scanning, secret scanning, and dependency checks can help find issues in generated changes, but a clean scan does not establish that the workflow resists prompt injection. GitHub describes these kinds of checks for third-party coding agents in documentation that currently labels the feature public preview; product capabilities and status can change. GitHub Docs: About third-party coding agents
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How to choose safeguards for your workflow
There is no universally best sandbox or single prompt-injection blocker. Match safeguards to the agent’s capabilities, the sensitivity of the code and data, and the impact of a mistaken action. When comparing setups, assess the actual boundary rather than relying on a product label.
Best Value
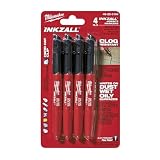
- Milwaukee Ink all Fine Point Marker, Black, 4 Per Pack
- 4 per pack Features Clog Resistant Marker Tip Writes through Dusty, Wet and Oily Surfaces Durable Marker Tip for Writing on Concrete, OSB and Rough Surfaces
- Clog resistant tip writes on dusty, wet and oily surfaces and is optimized for rough surfaces such as OSB, cinderblock and concrete
- Hard hat clip- attaches for easy access
- Quick dry time with reduced smearing and marking
| Decision area | What to check | Trade-off to manage |
|---|---|---|
| Isolation | Is the agent limited to a workspace, restricted shell, container, or VM? Which host files and credentials can it reach? | Stronger separation can limit access to local resources the workflow needs. |
| Tool authority | Can it only read, or can it write, run commands, push, or deploy? Are commands, paths, and resources scoped? | Reducing authority may require a person or a separate process to perform privileged steps. |
| Network boundary | Is egress blocked, destination-allowlisted, or unrestricted? Are transfers inspected or approved? | Blocking network access may prevent required downloads or integrations; allow exceptions narrowly. |
| Action approval | Which operations are gated? Can a reviewer see the action’s effect and the data involved? | More approval points add review work, so focus them on consequential actions. |
| Auditability | Are tool calls, permission changes, external inputs, and resulting diffs recorded and reviewable? | Logs need to be useful to reviewers and handled appropriately if they contain sensitive data. |
How to test whether the safeguards work
Evaluate the real workflow, not just the model’s behavior in an isolated prompt. Test indirect-injection routes that match how the team works: repository content, issue or pull-request text, tool outputs, fetched pages, and untrusted contributions. Check both whether the agent follows malicious instructions and whether the environment prevents a resulting action from reaching data or systems outside its permitted scope.
NIST’s CAISI recommends adaptive evaluation, task-specific measurements, and multiple attempts. A single successful or unsuccessful demonstration is not a complete risk assessment. Its January 2025 technical blog discusses agent-hijacking evaluations using Claude 3.5 Sonnet and AgentDojo; it should not be read as a current ranking of models. NIST CAISI: Strengthening AI Agent Hijacking Evaluations
Monitor unexpected tool calls and instructions that appear to propagate between agents. Re-test when the model, tools, permissions, configuration files, or integrations change. Measure task-specific outcomes, including whether sensitive actions were blocked and whether reviewers could detect unexpected changes.
Why a detection filter is not enough
Detection and refusal are useful layers, but neither guarantees that hostile content will always be identified or ignored. OpenAI’s March 11, 2026 article describes a reported 2025 example that worked 50% of the time with a specific user prompt. That figure applies only to the cited test, not to all prompt injections or coding agents. OpenAI summarizes the broader design goal as: “The goal is not limited to perfectly identifying malicious inputs, but to design agents and systems so that the impact of manipulation is constrained, even if it succeeds.” OpenAI: Designing AI agents to resist prompt injection
In practice, combine model-level defenses with external limits: narrow context, least-privilege tools, credential isolation, controlled egress, approval gates, and review. If one layer fails, the others should still restrict the consequences.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

