
Recommended Free Tools
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
A TPM 2.0 bypass skips an installer’s hardware-eligibility check; it does not add a TPM, enable one that is disabled, or make an unsupported Windows 11 installation supported. Before considering a bypass, check whether your PC already has TPM 2.0 that can be enabled in UEFI firmware.
What does “TPM 2.0 bypass” mean?
TPM stands for Trusted Platform Module. Windows 11’s requirement is for TPM version 2.0. A bypass is a way of getting past Setup’s TPM check on a PC that does not meet that requirement. It changes the installation check, not the computer’s hardware.
That distinction matters: bypassing the check does not install a TPM, enable a disabled firmware TPM, or provide the hardware security functions associated with TPM 2.0. Microsoft describes TPM 2.0 as part of Windows 11’s hardware root of trust and identifies security capabilities that rely on TPM features. Which features are affected in practice depends on the PC’s configuration and how those features are used; a bypass does not mean every Windows security feature stops working.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Check whether TPM 2.0 is present but disabled
A PC reported as lacking TPM 2.0 may have a TPM that is disabled or not detected because of its platform configuration. Check the computer’s UEFI firmware settings and consult the documentation for the exact computer or motherboard. The setting name and location vary by manufacturer, so there is no universal menu path. Microsoft also advises consulting the device manual or manufacturer before clearing a TPM; clearing it is not the same as enabling it.
#1 Best Overall
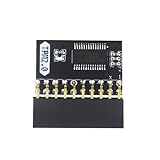
- APPLICATION: TPM 2.0 module suitable for Gigabyte, Asus and other brands of TPM 2.0 modules. 2.54mm pitch,20pin security modules.
- COMPATIBILITY: TPM chip is better compatible with DDR4 memory module of motherboard, built in support memory type higher than DDR3! Supported states may vary by motherboard specification.
- POWERFUL SECRECY: The TPM is a standalone crypto processor connected to a daughter board connected to the motherboard.It securely stores encryption keys, which can be created by encryption software.
- PREVENT ACCESS: Without the correct key, the content on the user's PC will remain encrypted,preventing unauthorised access.
- PERFECT REPLACEMENT: Our TPM 2.0 module can help repair the device and make it work properly. It functions the same as the original, ensuring the smooth operation of your device.
How a setup bypass differs from enabling TPM
| Option | What it changes | Windows 11 eligibility and support |
|---|---|---|
| Enable an existing TPM 2.0 in UEFI | Changes firmware configuration so Windows can detect the TPM, if the PC has one. | If the PC meets all minimum system requirements, this addresses the TPM check without bypassing it. Check the device documentation for its specific instructions. |
| Bypass the TPM check during installation | Skips or relaxes an installer eligibility check; it does not add or enable TPM hardware. | The installation remains on hardware that does not meet the TPM requirement. Microsoft does not support Windows 11 on devices that fail minimum requirements. |
What Rufus documents about its media bypass
The Rufus FAQ says Rufus 3.17 and later can create Windows 11 installation media that adds the BypassTPMCheck and BypassSecureBootCheck registry keys under the setup boot image’s LabConfig area. According to the project, these media-applied bypasses affect checks performed when booting from that media. They do not apply to checks made by running setup.exe from within an already-running Windows installation. See the Rufus FAQ for the project’s description.
This is Rufus’s documented behavior, not a guarantee for every later Rufus or Windows build or every installation path. The existence of a media bypass also does not make the resulting Windows installation eligible for Microsoft support.
Rank #2

- 【Wide Compatibility – Gigabyte & ASUS】 Specifically designed for Gigabyte and ASUS desktop motherboards with a 20-1 pin (2x10 / GA 20-1) 2.54mm pitch LPC TPM header. Ideal for upgrading to TPM 2.0 on DDR4 systems. (Note: NOT compatible with 12-pin, 2x6, or 14-pin headers).
- 【Windows 11 Readiness】 An essential hardware upgrade to meet Windows 11 security requirements. Ensure your system stays secure and up-to-date with a dedicated hardware TPM 2.0 module without replacing your entire motherboard or CPU.
- 【Advanced Security & Encryption】 Powered by the standalone Infineon SLB9665 encryption processor. This module securely stores cryptographic keys for software like Windows BitLocker, providing a robust layer of hardware-based security for your data.
- 【Platform Limits – No Laptops】 Optimized for Desktop motherboards from the DDR4 era (X99 series and newer). Not compatible with laptops or legacy DDR3 systems. Please verify your motherboard's header layout (2x10 pins) before ordering.
- 【Easy Setup & BIOS Note】 Simple plug-and-play installation takes only minutes with no tools required. IMPORTANT: After installation, you MUST enable "Security Device Support" or "Intel PTT / AMD fTPM" in your BIOS settings for Windows to recognize the module.
What bypassing means for support, updates, and security
Microsoft says: “If Windows 11 is installed on a device that doesn’t meet the minimum system requirements, Microsoft won’t provide support for any issues.” Microsoft also warns that such devices may have compatibility problems and are not guaranteed updates, including security updates. Read Microsoft’s guidance on Windows 11 devices that do not meet minimum system requirements before deciding.
TPM 2.0 has a security role beyond passing Setup. Microsoft explains its role in the Trusted Platform Module overview and its relationship to device security in System Guard documentation. Bypassing the installer check does not recreate those hardware-backed functions.
Rank #3

- ENCRYPTION KEY: The TPM 2.0 module can use an encryption key created by encryption software (e.g. for for BitLocker). Without this key, the contents of the user's PC will remain encrypted and protected from unauthorized access.
- STANDALONE ENCRYPTION PROCESSOR: The TPM 2.0 encryption security module is a standalone encryption processor connected to a daughter board attached to the motherboard.
- SUPPORTED MOTHERBOARDS: The TPM module supports for for 400, 500,600 and 700 Series Motherboards, for A520,B550,WRX80,X570S,B650 and Motherboards.
- SPI INTERFACE: 12‑1 Pin TPM security module supports memory types higher than DDR3, SPI interface, support for 10 11.
- RESERVED MEMORY: Simple to install and use, some motherboards require the TPM module to be plugged in or updated to the latest BIOS to enable the TPM option. Standard PC architectures reserve a certain amount of memory for system use.
Which option makes sense?
- If the PC may already have TPM 2.0: check UEFI settings and the manufacturer’s documentation first. Enabling an existing TPM is different from bypassing the check.
- If the PC lacks TPM 2.0: a bypass may get past an installation check, but it does not satisfy the requirement or remove Microsoft’s support and update caveats.
- If you are planning an in-place upgrade: do not assume a bypass documented for booting from Rufus media will apply when launching
setup.exeinside Windows; Rufus says it does not.
Microsoft’s advice for unsupported hardware is intended for people who accept compatibility risk. If you need a supported Windows 11 installation, use a device that meets the minimum requirements rather than relying on a bypass.
Quick Recap
Rank #4

- 【Quality materials and easy installation】TPM 2.0 Security Module is made of high quality material and is well made for long life.It is easy to install, lightweight and compact, and its easy integration makes it a breeze to install and operate quickly.
- 【Working environment】The TPM2.0 Security Module is compatible with GC-TPM2.0_S. Interface: LPC, TPM IC: SLB9665, Pin Connector: 12Pin.Please check compatibility before purchasing.
- 【Reliable Work】The TPM 2.0 Module is a highly reliable cryptographic processor that brings an extra layer of security to your Windows computer. With its advanced encryption technology, you can perform secure operations such as generating, storing, and restricting the use of cryptographic keys, ensuring that your system is protected from unauthorized access.
- 【High-quality replacement】high-quality professional use, the function is the same as the original model, stable performance, a good replacement of the original damaged old safety module.
- 【Model Support】Each security module is tested before it leaves the factory and is 100% perfectly works well.Therefore, Please confirm that your motherboard supports TPM2.0 technology.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

