
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Managing governance, risk, and compliance (GRC) for remote work means defining who can access which systems and data, reducing the risks created by remote devices and connections, and mapping those controls to your organization’s actual legal, contractual, and sector obligations. It is an operating model—not simply a VPN choice or a policy document.
What remote-work GRC needs to cover
Remote work shifts access beyond the traditional office network. Employees, contractors, vendors, and business partners may connect from different devices and locations to company networks, cloud services, and sensitive information. A workable GRC model connects three activities:
- Governance: Set responsibilities, eligibility, approved services, and acceptable work practices.
- Risk management: Identify and address exposure across people, endpoints, identity, remote-access services, cloud systems, and third parties.
- Compliance: Map controls to the requirements that actually apply to the organization, then retain evidence that those controls operate.
NIST’s SP 800-46 Rev. 2, published July 29, 2016, provides guidance on telework, remote access, and BYOD security. NIST’s publication index also references a Rev. 3 draft, so check NIST’s current publication status before treating Rev. 2 as the latest final edition.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Turn remote-work rules into operational governance
A policy is useful only when people know what it permits and who is accountable for making it work. CISA’s federal-focused Federal Mobile Workplace Security (August 14, 2024) describes practices that organizations can consider, including written agreements, approved-workspace self-certification, and training. These are practical reference points, not universal legal requirements for every private employer.
#1 Best Overall

- Remote Control Holder & Desktop Organizer: Keep your remotes and desk essentials organized with this rotating wooden holder that keeps your coffee table, desk, or end table tidy. Holds 3–6 remote controls plus small daily essentials like pens, glasses, and notepads.
- 360° Smooth Rotation with Anti-Slip Base: The 360-degree rotating base lets you easily access items from any angle. The anti-slip rubber bottom prevents sliding and protects your tabletop from scratches.
- 4 Compartment Smart Storage (2 Wide + 2 Narrow): Features 4 compartments (2 wide, 2 narrow) to neatly separate remotes, office supplies, and personal items, keeping everything organized and within reach.
- Natural Wood Construction with Smooth Finish: Crafted from natural wood with a smooth finished surface for everyday durability. Sturdy wooden construction provides reliable support while adding a warm, clean look to your space.
- Compact Size & Space-Saving Design: Measures 5.9" x 5.63" x 5.12", fitting neatly on coffee tables, desks, and bedside tables without taking up much space. Designed for small items only.
Write down eligibility, services, and data restrictions
Specify which roles may work remotely, what systems and services they may use, and what information may be accessed, stored, or transmitted from remote locations. Make restrictions understandable: for example, define which data may be downloaded to an endpoint and which must remain in an approved service.
Assign responsibility for access and devices
Name the roles responsible for approving remote access, maintaining devices, reviewing exceptions, reporting incidents, and addressing policy violations. Make clear how those responsibilities apply to employees as well as contractor-, vendor-, and partner-managed devices. NIST SP 800-46 Rev. 2 addresses organization-issued and personally owned devices, along with devices controlled by contractors, partners, and vendors.
Set expectations for the workspace and training
Where appropriate to the work and risk, establish an approved-workspace process and explain what a self-certification covers. Train workers on operational security, phishing, social engineering, and how to report a suspected incident. CISA’s federal guide discusses these practices as part of a remote-work security program.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchPC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Rank #2

- 【Office Humor + 2-in-1 Function 】Sarcastic office-themed phone stand with a built-in small mirror—stable horizontal/vertical phone hold at ergonomic angle, mirror for quick touch-ups! 5.5x3.2inch compact size saves desk space, adds fun to cubicle/home office.
- 【Durable for Daily Office Use 】High-grade scratch-resistant plastic construction, vivid fade-proof sarcastic patterns—stands up to knocks/spills, long-lasting for busy workspaces, no easy damage with daily use.
- 【Relatable Sarcastic Office Design 】Clever workplace satire patterns, eye-catching and unique—speaks to every desk warrior, shows your personality, makes coworkers chuckle at first glance, liven up boring 9-to-5.
- 【Universal Fit for All Workspaces】 Perfect for corporate offices, home workspaces, co-working hubs—A-frame slim design fits any small desk/cubicle corner, ideal for remote/onsite workers, versatile desk decor essential.
- 【Practical Hilarious Office Gift 】Ultimate gag gift for coworkers, teammates, bosses—great for birthdays, work anniversaries, holidays, promotions, stress relief, useful and fun, better than generic desk trinkets.
Manage risk across identity, endpoints, and remote connections
Remote access creates a connection that needs to be secured at both ends: the service accepting the connection and the device using it. NIST SP 800-46 Rev. 2 recommends securing remote-access servers and client devices, protecting sensitive information stored on endpoints and sent over external networks, and basing policies and controls on expected threats.
Know which devices and users can connect
Keep an inventory of approved devices and their ownership status, including BYOD and third-party equipment. Decide what device condition or configuration is required before access is allowed, and maintain software and security settings. Pair that inventory with access approvals so the organization can identify who is using a device and what it can reach.
Apply identity controls and limit privilege
Use identity controls proportionate to the sensitivity of the systems and information involved. Evaluate multifactor authentication (MFA) as part of the identity design, and restrict privileged remote actions to the people and tasks that require them. A security key can be one MFA option, but selection depends on identity-provider compatibility, deployment policy, and account recovery; a key by itself does not establish compliance.
Rank #3
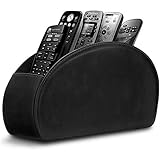
- A perfect solution to storage various remote controllers ,Overall size: 8.46 inches (length) x 2.95 inches (width) x 4.72 inches (height), five divisions, the distance between each division is 1.57 inches
- Excellent environmental protection material: The surface is made of high-quality pu leather, waterproof and non-slip, the inner lining is environmentally friendly flannel, soft and moisture-proof, the structural support is wooden, strong and durable
- The design is beautiful and practical: the arc-shaped plus line design, with sponge filling under the leather, looks very high-end, 5 divisions are very suitable for putting all your remote controls on hand and easy to identify, saving time and energy Space, to provide protection for the remote control from scratches, grease and abrasions.
- The application scenarios are very wide: used in tables, toilets, dining rooms, living rooms, study rooms, bedrooms and offices, and can be used as storage for stationery, glasses or makeup brushes. It can also be used to store various remote controls for cable boxes, Roku, Apple TV, Amazon Fire TV, sound bars, etc. Make your desktop neat and beautiful
- Available in 3 different colors: Caddy organizer is available in 3 classic colors black, brown & white Choose the color that best compliments your home décor.
Secure and monitor remote-access software
Remote-access software can be misused by threat actors, and misconfiguration can create business risk. CISA’s Guide to Securing Remote Access Software (June 6, 2023) addresses malicious use, detection, and mitigations. Maintain configurations, monitor access and connections, and include remote-access activity in incident response. No single access product removes the need for those controls.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsChoose an access approach that fits the environment
VPNs remain one way to provide remote connectivity, but CISA and partner agencies’ June 18, 2024 guidance, Modern Approaches to Network Access Security, discusses risks associated with traditional remote access and VPN deployments and points organizations toward approaches including Zero Trust, Secure Service Edge (SSE), and Secure Access Service Edge (SASE). The guidance does not establish a universal winner or provide a product comparison.
| Approach | What to assess |
|---|---|
| VPN-centered access | Review configuration, who and what can connect, the scope of access granted, and how connection activity is monitored. A VPN is not inherently unsafe, but its deployment and controls matter. |
| Zero Trust | Assess how identity and device context inform access decisions, how narrowly access can be scoped, and what changes are needed to integrate with existing systems. |
| SSE or SASE | Assess identity and device context, visibility into network activity, integration needs, operational complexity, and fit with the organization’s services and risk profile. |
Compare options against actual systems, users, data, and operational capacity rather than choosing a label as a substitute for risk analysis.
Rank #4
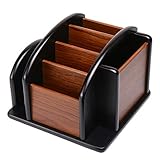
- HIGH QUALITY MATERIALS. The desktop organizer is made of premium high density fiberboard. The brown-and-black color of wood organizer makes your room be more elegant and makes your office be more professional. It is also easy to clean.
- PROPER SIZE. The approximate size of this desktop organizer is 7.25inch W x 7inch D x 6inch H. It may have little error due to manual measurement. It is big enough to hold many items.
- MULTIFUNCTIONAL STRUCTURE. The desk organizer has 6 compartments, 1 side slot for note pads, calculators or mail, and 1 side cup for files, books or writing utensils, 4 middle compartments are suitable to hold items in different size like remote controls, pens, scissor and so on.
- PERFECT FOR HOME AND OFFICE. The desk organizer can be set on any desktop, end table, or coffee table to organize your office, living room or kitchen. It is ideal to hold post-it note, binder clips, paper clips, scissors, markers, highlighters, pens, pencils, tape, erasers, white-out and other home or office essentials.
- NEW ITEM & QUALITY ASSURANCE: If the corner damage, it is unavoidable that caused by the transportation process. And if you are not satisfied with the item, please contact us at any time, we will provide you with return service or refund all your money.
Make BYOD and third-party access explicit
Organization-managed devices generally give an employer more direct control over configuration, updates, support, and separation of work data. BYOD may reduce the need to issue a separate device, but requires clear rules for protecting company information, managing access, and respecting user privacy. The right balance depends on data sensitivity and the organization’s ability to support and manage the device; NIST SP 800-46 Rev. 2 treats both organization-issued and personally owned devices as relevant to telework security.
For contractors, vendors, and partners, document who owns the device and account, what access is approved, who maintains the device, and how incidents are reported and coordinated. Third-party access should have an owner inside the organization and a defined scope, rather than being treated as an informal extension of an employee’s account.
Include cloud services in the control model
Remote teams often work in cloud services outside the traditional office network. Define which cloud services are approved, who administers them, how access is granted and reviewed, and what information may be stored there. CISA’s Executive Order cybersecurity overview describes federal cloud governance, a Cloud Security Technical Reference Architecture, Zero Trust, MFA, and encryption. That federal policy context is an example, not a blanket mandate for all organizations.
Best Value
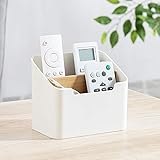
- Approximate Dimensions (in inches): 5 1/2 x 3 1/2 x 4 3/4 in
- Organize your desk and cut clutter in your office with this modern stylish and useful desk supply caddy
- Features 2 tiered slots for keeping remote controls, office supplies, and other items organized.
- Desktop remote control storage box made of plastic and wood
- Benifits for You - It help you to organize your desk and save space and time for you.
Clarify the division of responsibilities between the organization and cloud providers, including access management, security configuration, monitoring, and incident coordination. Using a provider does not mean the customer’s security responsibilities disappear.
Map controls to the organization’s actual obligations
Do not assume that one federal publication defines every organization’s compliance duties. Requirements may depend on the data handled, contracts, jurisdiction, privacy law, sector rules, and customer commitments. The cited security publications can inform control design, but they do not determine an individual organization’s legal obligations.
Build a requirements map that connects each applicable obligation to a control, an accountable owner, evidence, and a review cadence. Revisit it when the organization changes its systems, data types, jurisdictions, or work patterns. For organizations handling controlled unclassified information (CUI), NIST SP 800-171 Rev. 3 is relevant; it says remote-access monitoring and control help detect attacks and ensure compliance with remote-access policies. It is not a generic checklist for every remote workforce.
Quick Recap
Put the operating model into practice
- Define scope: List remote-work roles, approved services, data restrictions, and user responsibilities.
- Assign owners: Identify who approves access, maintains endpoints, reviews exceptions, and coordinates incident response.
- Inventory access: Record users, device ownership and approval status, remote-access services, cloud systems, and third parties.
- Set controls: Secure remote-access services and endpoints, maintain configurations, apply identity controls proportionate to risk, and limit privileged actions.
- Train and prepare: Cover phishing, social engineering, operational security, and incident reporting; define how remote incidents are escalated.
- Map and retain evidence: Connect applicable obligations to controls, owners, implementation records, reviews, and remediation.
- Reassess: Review the model when the organization’s systems, jurisdictions, data, or working patterns change.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

