
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
“Muddled Libra” describes an early campaign pattern in which attackers used the Oktapus phishing kit, text-message lures and fake sign-in pages to reach employees at large outsourcing and business-process firms. Unit 42’s later assessments show that the activity broadened beyond outsourcing and increasingly relied on live social engineering—especially calls to helpdesks and employees—rather than SMS alone. The name also is not universally defined: government advisories list Muddled Libra among Scattered Spider’s names, while Unit 42 describes it more cautiously as a subset within a loosely affiliated collective.
What the original campaign did
The 2023 account summarized by Dark Reading describes a repeatable intrusion sequence. Attackers researched a target, prepared lookalike domains and configured the Oktapus kit, then sent employees text messages that appeared to be corporate account or application alerts. The links led to counterfeit login portals designed to capture usernames, passwords and multifactor-authentication (MFA) codes.
1. Reconnaissance and preparation
Campaign operators first identified organizations, employees and authentication workflows. They registered realistic domains and built pages that imitated the target’s normal identity provider or internal application.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →2. Smishing lure
Employees received SMS messages framed as account warnings, access notices or other urgent corporate requests. The message’s objective was to move the recipient to the fraudulent portal rather than to install a conventional malware payload.
#1 Best Overall

- PHISHING-RESISTANT 2FA: Cryptographically binds to real domains, making phishing attacks impossible unlike SMS codes or authenticator apps.
- 3-SIDE CAPACITIVE TOUCH: Tap the end, left, or right side to authenticate, so it works in any orientation or crowded USB port.
- MULTI-COLOR LED INDICATOR: Blue means ready, blinking blue means tap now, green means success, and red means error for instant status feedback.
- IP68 WATERPROOF & BATTERY-FREE: Crush-resistant one-piece construction survives daily carry on a keychain or in a bag for years without any batteries.
- UNIVERSAL COMPATIBILITY: Works with Google, Microsoft, Apple, GitHub, AWS, and any FIDO2 / U2F / WebAuthn service, storing up to 100 passkeys.
3. Credential and MFA capture
After a victim entered credentials, the operators sought MFA codes or attempted to induce repeated approval prompts. This is why an account having MFA enabled did not, by itself, prevent the early intrusions.
4. Post-login activity
Unit 42’s 2023 reporting described credential theft, use of legitimate remote-management software, persistence, data theft and possible pivots into the breached organization’s customers. Unit 42 researchers told Dark Reading’s Elizabeth Montalbano, “Once established, this threat group is difficult to eradicate.” That statement refers to the 2023 activity described in the June 21, 2023 article, not to every later incident using a related label.
Why outsourcing and BPO firms mattered
Early reporting emphasized large outsourcing and business-process outsourcing (BPO) companies that served high-value cryptocurrency organizations and individuals. These firms can hold privileged access, support many customers and operate centralized identity or helpdesk functions. A compromise therefore offered a route not only into the service provider but potentially toward downstream customer environments.
Recommended Free Tools
Rank #2

- SECURITY KEY FOR ENTERPRISE ACCESS: Supports FIDO2 passkeys and U2F for secure authentication across enterprise IT systems.
- PHISHING-RESISTANT AUTHENTICATION: Enables passwordless login with secure on-device credential storage and PIN-based user verification.
- COMPATIBLE WITH ENTERPRISE SYSTEMS: Works with FIDO2, WebAuthn, and U2F across enterprise, cloud, and modern IT environments.
- DRIVERLESS FIDO2 AUTHENTICATION: FIDO2 works natively with modern browsers and platforms. No drivers required.
- USB AND NFC CONNECTIVITY: Supports authentication via USB-C and NFC. No batteries required.
The early exposed sectors included software automation, BPO, telecommunications and technology. That should be read as the focus of the reported campaign, not as a permanent target restriction.
How the activity evolved
Unit 42’s later assessments describe a broader sector footprint and a change in initial-access technique. Direct interaction with people increasingly replaced mass text-message delivery: operators called helpdesks while posing as employees who had lost access, or called employees while pretending to be corporate support. They reportedly pursued password or MFA resets and sometimes persuaded victims to launch remote-management software.
| Dimension | Early Oktapus-related pattern | Later pattern described by Unit 42 and government advisories |
|---|---|---|
| Initial access | SMS smishing, lookalike domains and counterfeit login portals | Direct calls to helpdesks or employees, including impersonation of staff or corporate support |
| Credential and MFA handling | Credentials and MFA codes entered into the fake portal; repeated approval requests could also be used | Password and MFA resets, one-time-password theft, MFA fatigue and, in some cases, SIM swaps |
| Remote access | Legitimate remote-management tools used after access was obtained | Victims reportedly manipulated into launching remote-management software; legitimate tools remain ambiguous without behavioral context |
| Target footprint | Large outsourcing and BPO providers serving cryptocurrency-related customers | Technology, hospitality and finance, with 2025 reporting also covering government, retail, insurance and aviation; contracted IT helpdesks remain exposed |
| Objective after entry | Credential theft, persistence, data theft and possible customer pivots | Administrative or lateral activity, monitoring and incident-response interference, data exfiltration and extortion |
| Containment timing | Not stated for the early campaign | Unit 42 observed an average of 1 day, 8 hours and 43 minutes from initial access to containment in the 2025 cases it discussed |
The containment figure is an observed statistic from those cases, not a universal response-time expectation.
Rank #3
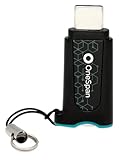
- Phishing-Resistant Security: Guard against cyber threats like phishing and credential theft with bank-grade security from OneSpan, trusted by over 60% of the world’s largest financial institutions.
- Effortless, Password-Free Authentication: Experience easy, one-touch security with this FIDO2-certified device. Say goodbye to passwords and hello to secure, passwordless access in seconds.
- Portable and User-Friendly: Compact and easy to use, DIGIPASS FX7 ensures secure access anytime. Simply plug into a USB-C port on a laptop, desktop, tablet, or phone, and tap to authenticate. For added security, a PIN entry option is also available.
- Broad Compatibility: This single security key grants access to over 1,000 FIDO2-enabled services, compatible with Microsoft 365, Google Workspace, AWS, Salesforce, Okta, OneLogin, Ping Identity, and more.
- Plug-and-Play Activation: With a zero-footprint design, DIGIPASS FX7 requires no software installation or complex configuration. Just plug it in, and it’s ready to go.
Scale indicators from the reporting
- Unit 42’s 2025 updated assessment said the earlier Oktapus framework activity involved more than 200 realistic fake authentication portals.
- The same assessment said credentials and MFA codes were gathered across more than 100 organizations.
- In one 2025 case, Unit 42 reported more than 100 GB of data exfiltrated during a two-day period. That is a single-case observation, not a typical volume.
What happens after a helpdesk or employee is deceived
A successful reset or approval can provide a foothold that outlives the original conversation. Unit 42 describes access to downstream customer information, lateral movement or administrative actions, interference with monitoring and incident response, exfiltration and extortion. The FBI and partner agencies likewise warn that attackers may combine helpdesk or IT impersonation with OTP theft, repeated MFA prompts, SIM swaps and legitimate remote-access utilities.
Free tools Windows power users keep installed
One-click scans. No signup required.
Remote-management software deserves careful interpretation. The FBI advisory says such utilities can be abused, but their presence alone does not prove compromise. Investigators should correlate the tool with the user, time, ticket, device, command history, authentication events and network activity.
How the names relate
Naming is unsettled. Unit 42 characterizes Muddled Libra as a distinct subset in a loosely affiliated collective discussed under names including Scattered Spider, Octo Tempest and Oktapus. A joint government advisory updated July 29, 2025 lists Muddled Libra among Scattered Spider’s other names. Those are different analytical taxonomies, so they should not be presented as universally interchangeable labels.
Rank #4

- HARDWARE 2FA AND MFA: FIDO Alliance Certified FIDO2 v2.1 with CTAP2 plus legacy U2F and CTAP1 for strong two-factor login and passwordless sign-in on services that support security keys
- BUILDING ACCESS ON ONE CARD: MIFARE DESFire EV2 4K applet with AES encryption adds office door and physical access control alongside digital authentication
- CERTIFIED SECURE ELEMENT: An NXP Common Criteria EAL6+ certified secure controller and Java Card platform protects your keys on a tamper-resistant chip
- DUAL INTERFACE SMART CARD: Contactless NFC ISO 14443 plus ISO 7816 contact reader support in an ISO 7810 ID-1 format that is passive and needs no battery
- SWISS ENGINEERED DESIGN: Built by Cryptnox as a single card for authentication and access control and backed by a 2 year warranty
Unit 42 also reported that affiliations and tooling changed over time, including an affiliation with DragonForce ransomware-as-a-service in its 2025 assessment. That is an assessment about the observed period, not a permanent attribute of every cluster or incident using one of these names.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Defensive controls for organizations and service providers
The practical lesson is to secure the human and identity processes that an attacker is trying to manipulate, especially where a provider can reach many customers.
Harden helpdesk resets
- Require a documented, phishing-resistant identity-verification procedure before password, MFA or SIM-related changes.
- Use independent verification channels and approval from a second authorized employee for high-impact resets.
- Record the caller, ticket, device, reset reason and resulting authentication events for review.
Reduce MFA takeover paths
- Prefer phishing-resistant methods such as hardware-backed security keys where supported.
- Monitor for repeated approval prompts, unusual one-time-password requests, number-porting or SIM-change signals and sudden changes to authentication factors.
- Train users to reject unexpected prompts and to report a suspected MFA-fatigue attempt immediately.
Control remote-management software
- Maintain an approved-tool inventory and restrict execution to managed devices and authorized support workflows.
- Alert on new remote tools, unusual parent processes, after-hours sessions, or connections from accounts that do not normally provide support.
- Do not treat a tool’s brand as proof of safety or compromise; investigate its surrounding behavior.
Apply identity and conditional-access policy
Unit 42 recommends tight security controls, awareness training and vigilant monitoring. It reports that correctly implemented Conditional Access Policies can disrupt activity and limit impact in Microsoft Entra ID environments. Conditional access is a layer, not a guarantee: policy coverage, exceptions, recovery methods and privileged accounts still need testing.
Best Value

- ENTERPRISE ROLLOUT: 25 White PVC cards in one SKU sized for bulk procurement, one card per employee for both web authentication and building access
- HARDWARE 2FA AND MFA: FIDO Alliance Certified FIDO2 v2.1 with CTAP Level 1 for phishing-resistant login and passwordless sign-in where the service supports it
- BUILDING ACCESS: MIFARE DESFire EV2 applet with 4K AES storage adds door and facility access to the same card employees use for account security
- CERTIFIED SECURE ELEMENT: NXP JCOP 4 chip rated Common Criteria EAL 6+ augmented
- DUAL INTERFACE: Tap over NFC (ISO 14443) or use a contact reader (ISO 7816), backed by a 2-year warranty from Swiss company Cryptnox
Protect the provider-customer boundary
Outsourcers should limit standing access, separate customer environments, review privileged support roles and alert on unusual cross-customer activity. Customers should treat a contracted helpdesk as part of their identity threat model and verify that its reset procedures meet their own security requirements.
Incident-response priorities after a suspected social-engineering breach
- Contain identity access: suspend affected accounts, revoke active sessions and tokens, review newly registered MFA methods and investigate password or factor resets.
- Check telephone and helpdesk changes: examine SIM-swap or number-porting events, caller records, tickets and reset approvals.
- Review endpoint and remote-access evidence: identify tools launched, sessions established, files accessed and commands executed.
- Scope customer exposure: determine whether the account could reach downstream tenants, shared administration systems or customer data.
- Preserve evidence and monitor: retain authentication, helpdesk, endpoint, cloud and network logs while watching for persistence, exfiltration and extortion activity.
What this title does—and does not—establish
“Oktapus-related smishing” accurately describes the early campaign mechanism reported in 2023, and outsourcing firms were prominent early targets. It does not describe the full current method set. By 2024 and 2025, Unit 42 and government reporting described broader sectors, helpdesk and IT impersonation, MFA fatigue, SIM swaps and direct manipulation of employees. Techniques, targets and affiliations are volatile, so the latest Unit 42 and government advisories should be checked when making an operational decision.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

