
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Yes. Dragos tracked 119 ransomware groups targeting industrial organizations worldwide in 2025, up from 80 in 2024, while U.S. and Canadian advisories warn that pro-Russia hacktivists are targeting exposed industrial control systems and other operational technology (OT). The numbers are not a North America-only count, but the warnings and reported incidents make the risk concrete for utilities, manufacturers and other critical-infrastructure operators.
What the reported increase means
OT is the hardware and software used to monitor or control physical processes, including industrial control systems (ICS), programmable logic controllers (PLCs), human-machine interfaces (HMIs) and engineering workstations. An attacker who reaches these systems may affect operations, not just steal files.

Dragos tracks groups and incidents affecting industrial organizations. Its figures show a sharp rise in the number of ransomware groups targeting the sector, but they are not a census of every group or attack worldwide, and they do not isolate North American activity.
Recommended Free Tools
| Measure | Reported figure | What it covers |
|---|---|---|
| Ransomware groups targeting industrial organizations in 2023 | 50 | Dragos-tracked groups, as reported in its 2025 review. |
| Ransomware groups targeting industrial organizations in 2024 | 80, up 60% from 50 in 2023 | Dragos-tracked groups, as reported in its 2025 review. Dragos also documented 1,693 ransomware attacks against industrial organizations in 2024, an 87% increase from the previous year. |
| Ransomware groups targeting industrial organizations in 2025 | 119, up from 80 in 2024 | Dragos-tracked groups, as reported in its 2026 review. Dragos said they collectively impacted 3,300 organizations and ransomware attacks increased 64% year over year. |
| OT threat groups in 2024 | 23 worldwide, with nine active in OT operations | Dragos’s 2025 reporting. This is a separate measure from the count of ransomware groups. |
These measures should not be added together: ransomware groups are one category of financially motivated actor, while the broader OT threat-group count includes other kinds of adversaries. Nor does the increase in tracked groups mean every group directly operated an industrial process; criminal groups may reach OT by compromising IT, VPNs or remote services first.
#1 Best Overall

- BUSINESS CYBERSECURITY SOLUTION: SafeBiz is an advanced cybersecurity solution that protects your work network and safeguards your Business data and all internet connected devices in your business from cyber threats and hackers. SafeHome blocks phishing, malware, ransomware, online scams and dark web threats.
- ADVANCED THREAT PREVENTION: SafeBiz includes a Next-Gen Firewall, DNS Security, Web Filtering, Dark Web Protection, Geo-fencing and other AI Powered cybersecurity features protecting your Business and Sensitive Data from internet threats and hackers.
- BUSINESS DATA & IDENTITY SECURITY: Safeguards your Official and financial data, protecting them from online theft and unauthorized access.
- EASY SETUP: Connects effortlessly to any existing wireless router or internet connection, setting up in minutes without the need for any changes to your Business internet connection.
- HIGH SPEED CONNECTIVITY: Supports an aggregate throughput of up-to 4.3 Gbps, maintaining high-speed browsing and streaming performance for up to 128 devices.
Why North American operators are specifically at risk
CISA and its partners warned that pro-Russia hacktivists were targeting vulnerable ICS and small-scale OT in North American and European critical-infrastructure sectors. The sectors named include water and wastewater, dams, energy, and food and agriculture. The Canadian Centre for Cyber Security has separately described a growing number of non-state actors targeting internet-connected Canadian OT for disruptive or destructive effects.
In a May 1, 2024 statement, NSA Director of Cybersecurity Dave Luber said: “This year we have observed pro-Russia hacktivists expand their targeting to include vulnerable North American and European industrial control systems.” CISA and NSA documented cases in the United States in which pro-Russia hacktivists remotely manipulated HMIs at water and wastewater facilities. The reported cases generally caused limited physical disruption, but unauthorized changes to an operator interface can still obscure conditions or interfere with control.
The group names below illustrate different kinds of activity identified in the cited reporting; they are not a complete list of actors targeting North America. Dragos’s tracking is global, while government advisories describe particular regions or incidents, and attribution is not equally clear in every case.
Which kinds of groups are targeting industrial environments?
Pro-Russia hacktivists
These actors have targeted vulnerable ICS and small-scale OT, including remote manipulation of exposed HMIs in U.S. water and wastewater cases. Hacktivist activity may be intended to disrupt, intimidate or attract attention; the documented incidents generally had limited physical effects, but the access itself can undermine operators’ ability to trust what an interface displays.
Voltzite (Volt Typhoon)
Dragos tracks Voltzite, also known as Volt Typhoon, as an OT-relevant actor associated with China and critical-infrastructure targeting. This is a state-linked threat category, distinct from opportunistic criminal ransomware, and should not be conflated with the specific hacktivist cases described above.
Electrum (Sandworm)
Dragos tracks Electrum, also known as Sandworm, as a Russia-linked group with destructive OT capabilities, including wiper activity. A wiper is malware designed to erase or damage data; in an industrial context, destructive actions can hinder recovery as well as disrupt operations.
Bauxite
Dragos identifies Bauxite as a group aligned with Iranian interests and warns of campaigns against critical infrastructure. Its inclusion reflects the wider range of state-aligned threats relevant to industrial defenders, not proof that every named group has attacked every North American sector.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Ransomware ecosystems
Ransomware groups are financially motivated and numerous. Their route into an industrial environment may begin with an IT account, a compromised VPN, an exposed remote service or credentials reused across systems. A criminal operator does not need to be an OT specialist to create operational risk if a compromised business network is connected to control systems or if remote access is poorly restricted.
Rank #3
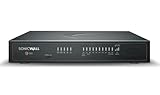
- HIGH AVAILABILITY UNIT: Secondary appliance for active/standby stateful failover; requires a matching primary firewall. Hardware only — security services and support are not included.
- PERFORMANCE: Up to 5 Gbps firewall inspection, 2.5 Gbps threat prevention and 2.5 Gbps IPSec VPN throughput driven by SonicWall's patented Reassembly-Free Deep Packet Inspection (RFDPI) engine.
- CONNECTIVITY: 8x1GbE + 2x5G SFP+ + 2x10G SFP in a desktop form factor; zero-touch deploy and manage on-box or via cloud Network Security Manager (NSM).
- THREAT PROTECTION: SonicOS 8 delivers intrusion prevention, gateway anti-malware, application control, TLS/SSL decryption, Capture ATP multi-engine sandboxing (RTDMI) and reputation-based content & DNS filtering with an active service subscription.
- BUILT FOR DISTRIBUTED & HIGH-END SMB: Secure SD-WAN, IPSec and SSL VPN plus Zero-Trust Network Access through Cloud Secure Edge keep distributed sites and remote workers protected.
How attackers reach OT
Remote access is often necessary for maintenance and support, but an exposed or weakly protected path can give an attacker a route to an HMI or a bridge from enterprise IT into an industrial network. CISA’s fact sheet urges operators to harden HMI remote access and implement multifactor authentication (MFA).
- Internet-exposed HMI or VNC: A control interface or remote desktop service reachable from the public internet can invite unauthorized access, especially if credentials are weak or unchanged from their defaults.
- Poorly secured remote access: Remote connections without MFA, tightly scoped permissions or adequate monitoring can be abused after credentials are stolen or guessed.
- VPN or external-service compromise: Attackers may compromise an account or service used by staff or vendors, then use that foothold to reach internal systems.
- Movement from IT into OT: If enterprise and industrial networks are not adequately separated, an intrusion that starts with ordinary business systems may progress toward operational assets.
These paths can overlap. The practical concern is not only who is attacking, but whether an attacker can reach a control interface, change what an operator sees, interfere with a process or prevent safe recovery.
What an OT attack can do to operations
Industrial consequences extend beyond data theft. A compromised or unavailable HMI can cause loss of view: operators may be unable to see reliable process status. An attacker or outage that prevents commands from reaching equipment can cause loss of control. Either condition may require staff to halt or restrict operations until they can verify the process and restore safe control.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsIn incidents to which Dragos responders were called, 75% led to a partial OT shutdown and 25% to a full shutdown, according to Dragos’s 2025 reporting. Those percentages describe that responder-involved set of incidents, not all industrial ransomware attacks. They nevertheless show why an intrusion that begins as a cyber incident can become an uptime and safety problem.
Rank #4

- Powerful 16-Core Performance & Low Power: Powered by the Intel Atom C3958 Processor (16 Cores/16 Threads, 2.00 GHz), this mini PC delivers exceptional multi-tasking capabilities for virtualization and routing. With a TDP of only 31W and a peak power consumption of 30W, it offers enterprise-grade performance with high energy efficiency.
- Massive 10-Port Network Connectivity: Designed for heavy network loads. Features 6x Intel i226-V 2.5G LAN ports and 4x Intel X553 10G SFP ports on the front panel. Ideal for use as a high-performance firewall, soft router (pfSense/OPNsense), or network gateway handling massive data throughput.
- Flexible Storage & Memory Expansion: Supports up to 2x SO-DIMM DDR4 2400MHz memory slots for smooth multitasking. Storage is versatile with options for 2x M.2 2280 SATA SSDs, 1x SFF SATA HDD/SSD, and an onboard eMMC interface, ensuring fast boot times and ample space for logs and databases.
- Versatile I/O & Wireless Support: Equipped with a rear VGA port for local debugging/management and a Console port for direct system access. Includes an M.2 slot for a 4G LTE module (with SIM slot) and WiFi antenna ports, providing reliable wireless backup connectivity for remote management.
- Compact Industrial Design & Wide OS Support: Measuring just 9.25" x 4.72" x 2.76", this fanless-style compact unit fits easily into server racks or network cabinets. It supports Windows Server and Linux distributions, operating reliably in temperatures from 0°C to 45°C, making it perfect for 24/7 industrial applications.
How utilities and manufacturers can reduce exposure
Prioritize protections according to whether a weakness could cause loss of view, loss of control or an unsafe interruption. The following measures address the remote-access and network paths emphasized in the government guidance and incident reporting.
- Remove unnecessary public access. Identify HMIs, VNC services and other control interfaces reachable from the internet. Remove that exposure unless there is a clear operational need; where remote access is necessary, put it behind a controlled, monitored access path rather than leaving the interface directly exposed.
- Require MFA on remote access. Apply MFA to every supported remote-access route, including vendor and maintenance access. Use individual accounts with permissions limited to the systems and tasks each person needs.
- Replace default and shared credentials. Change default passwords and eliminate shared administrator accounts where feasible. Individual accounts improve accountability and make it easier to remove access when a person or vendor no longer needs it.
- Separate OT from IT and the public internet. Segment industrial networks so that access from enterprise systems is controlled rather than automatic. Monitor traffic crossing between zones and pay particular attention to engineering workstations and remote connections that can reach control assets.
- Inventory operational assets and remote services. Record PLCs, HMIs, engineering workstations, remote-access services and their connections. Use that inventory to prioritize vulnerabilities that could affect an operator’s view or control of a process.
- Prepare for safe operation and recovery. Maintain tested offline recovery capabilities and manual operating procedures for safety-critical processes. Recovery plans should account for the possibility that control systems or the systems needed to administer them are unavailable.
- Monitor and report. Watch for unusual remote logins, unexpected access to HMIs or engineering systems, and suspicious movement across IT/OT boundaries. Report incidents through the relevant national or sector channel and apply current CISA, NSA or Canadian guidance relevant to the organization.
Choosing monitoring and security support for OT
Tools and services should be assessed against the plant’s operating conditions and legacy equipment, not just a general IT feature list. Before selecting an OT monitoring platform or external support, ask:
- Visibility: Does it passively observe the OT protocols and assets actually present in the environment?
- Remote-access detection: Can it help identify abuse of HMI, VNC, VPN, vendor or engineering access?
- Identity and segmentation: Can it work with the organization’s identity controls and reveal traffic crossing OT/IT boundaries?
- Incident response: Is OT-specific response support available when an event could affect operations?
- Safety and uptime: Can the deployment and monitoring approach avoid unacceptable effects on safety-critical or fragile systems?
- Legacy deployment: Can it provide useful visibility where equipment is old, sensitive to change or unable to run modern endpoint software?
For smaller water, manufacturing or public-sector operators, start with an accurate asset and remote-access inventory, removing unnecessary exposure, securing accounts and defining an incident-reporting route. Those steps address common paths without assuming that every facility can replace legacy controls or deploy the same monitoring architecture.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

