
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
There is no authoritative global ranking of the biggest IoT attacks in 2026. The clearest risks are vulnerable connected devices being recruited into botnets, exposed systems being compromised directly, and attackers using poorly protected IT or IoT networks as a possible route toward operational technology (OT). Reported consequences include service disruption and operators switching to manual processes. Businesses can reduce risk by knowing what is connected, limiting internet exposure, maintaining devices, and controlling network paths—while taking care not to disrupt sensitive operations.
What IoT threats have mattered most in 2026?
These are prominent threat patterns in the available reporting, not a ranked list of the world’s largest incidents. The risk to a business depends on what a device does, how it is exposed, and what other systems it can reach.
Botnet recruitment and denial-of-service
Attackers can compromise connected devices and remotely control them as part of a botnet. A botnet can be used to send traffic that overwhelms a target service, causing a distributed denial-of-service (DDoS) outage. The U.S. Government Accountability Office (GAO) identifies botnets and denial-of-service among threats to networked devices in its report on cybersecurity risks to networked devices.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minuteExploitation of outdated or vulnerable devices
Devices that miss security updates, use weak credentials, or expose unnecessary services can give attackers an entry point. GAO describes a state-sponsored group using out-of-date routers and IoT devices that were no longer receiving manufacturer updates or patches. Separately, the EU Agency for Cybersecurity (ENISA) identifies exploitation of known and zero-day vulnerabilities as a prevalent intrusion vector in its broader 2026 threat-landscape release.
Movement from IT or IoT networks toward OT
Some connected devices share networks or routes with business systems and industrial or facilities equipment. GAO describes an assessment that attackers appeared to pre-position on IT networks to enable movement toward connected OT and possible disruption of critical infrastructure. That is a reported threat assessment, not proof that every compromise follows this path. The practical concern is that a device with access beyond its own function can become a bridge.
#1 Best Overall

- 𝐄𝐚𝐬𝐲 𝐒𝐞𝐭𝐮𝐩 𝐈𝐧𝐝𝐨𝐨𝐫/𝐎𝐮𝐭𝐝𝐨𝐨𝐫 𝐂𝐚𝐦𝐞𝐫𝐚 — 2.5K HD video, vibrant color night vision and IP66, ensuring you never miss a moment, day or night,rainy or sunny. With dual-band 2.4G/5G WiFi & Plug and play setup of the cameras for home security - just download app and scan QR code! No tools needed for tabletop use, mounting screws included for walls
- 𝟐.𝟓𝐊 𝐐𝐇𝐃 & 𝐂𝐨𝐥𝐨𝐫 𝐍𝐢𝐠𝐡𝐭 𝐕𝐢𝐬𝐢𝐨𝐧 — Experience crystal-clear visibility day and night with full-color night vision enhanced by a built-in white light. Perfect as a baby monitor, pet camera, or security camera to monitor your home inside and out
- 𝐒𝐦𝐚𝐫𝐭 𝐀𝐈 𝐃𝐞𝐭𝐞𝐜𝐭𝐢𝐨𝐧 & 𝐀𝐥𝐞𝐫𝐭𝐬 — Stay informed about what matters most with human/motion/sound detection up to 33 feet away. The camera deters intruders with flashing lights and a siren while sending instant alerts to your phone — keeping you one step ahead of any suspicious activity. Call +1 (978) 437-5767 for expert support with setting up and optimizing Vimtag cameras, available Monday to Friday, 9:00 AM - 6:00 PM (ET)
- 𝐄𝐧𝐡𝐚𝐧𝐜𝐞𝐝 𝐓𝐰𝐨-𝐖𝐚𝐲 𝐀𝐮𝐝𝐢𝐨 - Communicate effortlessly with guests or check in on pets using the upgraded two-way audio feature of this indoor camera, allowing you to see, hear, and speak from anywhere
- 𝐓𝐰𝐨 𝐑𝐞𝐜𝐨𝐫𝐝𝐢𝐧𝐠 𝐎𝐩𝐭𝐢𝐨𝐧𝐬 & 𝐑𝐞𝐚𝐥-𝐓𝐢𝐦𝐞 𝐒𝐡𝐚𝐫𝐢𝐧𝐠 - With the mobile app, you can access the baby camera's video anytime, anywhere, view real-time footage, and even share monitoring content with family, keeping you informed about your home dynamics while you're away.Enjoy secure cloud recording with Vimtag Cloud (subscription required) for detecting people, sounds, motion. Alternatively, you can insert a microSD card (sold separately) for local video storage
Direct manipulation of exposed operational systems
GAO reports that CISA described July 2026 targeting of internet-exposed water-sector assets. Attackers changed passwords and disconnected assets; reported consequences included boil-water notices and manual operation. These are sector-specific examples showing that compromise can affect operations, not evidence that every IoT incident causes physical harm.
What 2026 attack examples have been reported?
A May 7, 2026 IT Pro report describes several botnet-related cases. The figures below are claims reported by that article, rather than a comprehensive or independently established count of IoT attacks.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →| Case | What IT Pro reported | How to read the figure |
|---|---|---|
| RondoDox | More than 40,000 automated attacks in January, exploiting an HPE OneView remote-code-execution flaw. | The article’s reported attack count; it is not a count of infected IoT devices. |
| Kimwolf | More than two million infected hosts. | The article’s reported host estimate; it does not measure all IoT compromises. |
| KadNap | More than 14,000 edge devices compromised in March. | The article’s reported device figure, not a global incident total. |
The same article reports a coordinated law-enforcement action against several botnets. These cases illustrate why exposed routers, edge devices, and other connected equipment deserve attention, but they do not establish which attacks were globally the “biggest.”
What broader cyber statistics can—and cannot—tell you
ENISA’s 2026 release analyzes 2025 events across the EU cyber landscape; its figures are not IoT-specific attack rates. They provide context about the environment businesses operate in, not a measure of how often IoT devices were attacked.
- Vulnerabilities: ENISA reports more than 48,000 newly assigned CVE identifiers during 2025, a 22% year-over-year increase. That does not show how many affected IoT devices.
- Unauthorized access: Among the small subset of such incidents for which ENISA could identify an intrusion vector—5% of those incidents—60% were seen leveraging a vulnerability. This is not 60% of all attacks or IoT incidents.
- DDoS impact: ENISA describes 51% of recorded DDoS cases in its EU reporting as low-impact. This is not a measure of IoT botnets or of the consequences for any particular business.
ENISA also highlights ransomware, vulnerability exploitation, supply-chain and third-party dependencies, and politically motivated activity. These wider risks matter because connected devices depend on networks and services beyond the device itself.
Rank #2
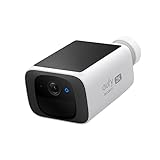
- Continuously Powered by Solar: Just 3 hours of sunlight is enough to keep the camera running. The tiny size and wire-free design allow it to be installed anywhere.
- Day and Night Clarity: Enjoy clear black-and-white night vision thanks to infrared LEDs and an f/1.6 aperture. Please note that spotlight color night vision is not supported.
- Easy Installation: Use anywhere thanks to its tiny size and wire-free design. Drill one hole, once.
- Human Detection: Al alerts you to anyone in your yard, whether family, a courier, or a stranger. Connect to HomeBase 3 for individual facial recognition.
- No Monthly Fee: One-time purchase. No monthly fees or hidden costs. On-device storage and AI for complete security and transparency.
How should a business reduce IoT risk?
1. Build an inventory that supports action
Record each device’s owner, location, purpose, model, firmware, network connections, support status, and business criticality. Include equipment that can be overlooked, such as cameras, printers, building controls, routers, sensors, and facilities or industrial devices. GAO notes that incomplete or stale inventories make it harder to know what is connected and spot unauthorized or abnormal activity.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware match2. Find and justify internet exposure
Identify devices and services reachable from the internet, then remove exposure that does not have a clear operational need. CISA’s exposure-reduction guidance recommends scanning for exposed systems and assessing why that exposure is required. Treat remote access as a deliberate business decision rather than a default setting.
3. Patch, replace, or isolate devices that cannot be patched
Apply vendor firmware updates and prioritize known exploited vulnerabilities. If a device no longer receives security updates, plan replacement or compensating network controls; do not assume it can be maintained safely indefinitely. Confirm update procedures with the vendor and operations owners where a change could affect availability.
4. Reduce unnecessary functions and access
- Change default credentials and use unique, strong credentials for devices and services.
- Use device authentication where supported.
- Disable unused services and remote-management features.
- Review vendor security and operational guidance before changing a setting on equipment that supports a physical process.
These measures align with the practical advice in IT Pro’s report, but implementation should fit the device and the organization’s security requirements.
5. Restrict network paths between IoT, IT, and OT
Separate IoT devices from user and business systems, and allow device-to-device communication only when it is needed. Review routes into OT especially carefully. This is a practical response to the interconnected networks and potential attacker movement described by GAO; involve OT owners because network changes can affect availability or safe operation.
Recommended Free Tools
Rank #3

- High-definition pan and tilt camera: Capture every detail in pristine 1080p HD quality, from any angle, with the Energizer Connect security camera's 355-degree horizontal and 48-degree vertical pan and tilt capabilities.
- Night Vision Equipped: Camera has 4 led lights and 4 IR lights that switch automatically depending on the lighting conditions, allowing you to see color at night or black and white in total darkness.
- Two-Way Audio: Allowing you to listen and talk to the person in the video, using the built-in microphone and speaker, or siren alarm to deter intruders.
- Flexible Storage Options: Choose cloud storage with a complimentary 30-day trial or utilize a micro SD card (up to 128GB, not included) for local recording.
- 2.4GHz Wi-Fi Compatible: Connects to your 2.4ghz wifi network, which is the most common wifi frequency. It does not support 5ghz wifi networks.
6. Discover devices without endangering operations
Asset discovery is not automatically harmless. GAO reports that active queries can disrupt or disable some sensitive systems. Coordinate scans with device and operations owners, schedule testing appropriately, and consider passive discovery where it is suitable.
7. Prepare for an outage, not just a breach
For systems that support essential services or physical processes, define an incident escalation path and test a manual fallback. The water-sector cases reported by GAO show why teams should know who can safely take over operations and how to communicate when a connected system is unavailable.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How should a business prioritize its next steps?
Start with the devices whose compromise or outage would matter most, rather than treating every connected device as equally urgent. Use these questions to order remediation:
- Is it exposed? Prioritize internet-reachable devices and services without a clear operational need for public access.
- Can it be maintained? Identify devices with known vulnerabilities, overdue updates, or no vendor support.
- What can it reach? Give closer review to devices with paths to business-critical systems or OT.
- What happens if it stops? Prioritize equipment whose interruption could affect essential operations, safety, or service delivery, and confirm an appropriate fallback.
These factors help set remediation order; they are not a substitute for evaluating the specific device, vendor guidance, and operational environment.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

