
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Roll out Microsoft Purview Data Loss Prevention (DLP) in stages: define the risk and owners, simulate the policy, test policy tips with a bounded pilot group, review matched events and user feedback, tune the policy, and expand only when its results and response process are ready. Simulation shows what a policy would match without enforcing its configured actions; it is a way to assess likely impact, not proof that every relevant workload or activity is covered.
Start with the control objective and its owners
Before creating or materially changing a policy, agree on what sensitive information and user activity you need to protect. Microsoft’s DLP planning guidance advises identifying stakeholders, describing sensitive information categories, and setting goals and strategy. Make the business approval and operational ownership explicit rather than leaving them to be resolved during enforcement.
- Define the intended risk: Identify the information, action, and business context the policy should address.
- Set the boundary: Specify the workloads, locations, users, devices, apps, and sites that are meant to be in scope.
- Name the decision-makers: Assign an owner for policy design and business approvals, and identify who will review events and decide exception requests.
- Agree how to respond: Decide what the team should do when it sees a likely policy match or a report of disrupted work.
Licensing, permissions, and workload availability depend on the tenant, subscription, role assignments, and configuration. Verify what applies in your environment before promising that a policy or report will be available.
Simulate before enforcement
Microsoft recommends using simulation to assess a policy’s impact before turning on enforcement. In simulation, configured actions are not enforced, so administrators can examine which items would match and review alerts for accuracy. Do not assume that a policy behaves as intended just because its conditions look correct: inspect the resulting matches and investigate representative cases.
#1 Best Overall

- Solid&Durable: Security box is constructed from heavy duty cold rolled steel; Electrostatic powder coat prevents rust and corrosion; Dimension: 18”D×18”W×5”H
- Temperature Control: Built-in fan and vents in both sides exhaust hot air, control temperature balance appropriately to prevent overheating
- Removable Top Cover: Top cover fixed by screws can be disassembled or installed according to daily use
- Cable Passage: Three punch-out holes in the back of lock box enables cable to pass through conveniently
- Device Security: Lockable metal box comes with a key to prevent theft, loss and damage; A reliable storage solution of NVR, DVR, POE Switch, document and any valuables
- Run the policy in simulation. Include the locations and scope you expect to protect, while checking that the relevant workload is supported and actually included.
- Review simulation results and alerts. Determine whether matches reflect the sensitive information and activity in your stated objective; distinguish valid detections from irrelevant or ambiguous matches.
- Record gaps and potential disruption. Note missed cases, unexpected matches, affected workflows, and questions that need a business decision before any restrictive action is enabled.
Simulation is only as representative as the policy’s scope and the data and activities visible to it. For endpoint scenarios, devices must be onboarded and reporting to Activity explorer before relying on that view for operational visibility. Check prerequisites for the specific workload and tenant.
Microsoft’s simulation-mode getting-started material says simulation scan results are saved for 30 days. It also describes an optional setting that can turn a policy on if it is not edited within fifteen days of simulation. These are product behaviors, not recommended pilot durations or universal rollout deadlines; check the current settings and documentation before relying on them.
Choose how to expose the policy during the pilot
After reviewing simulation behavior, choose whether a pilot should include policy tips and how broad the simulated audience should be. Microsoft’s deployment guidance recommends a narrow target group for the policy-tip stage, so users can give feedback and help others as the policy expands. A broader simulation can reveal more varied activity, but it also creates more results for administrators to review.
| Choice | What it helps you learn | Main trade-off |
|---|---|---|
| Simulation without policy tips | How the configured conditions match without exposing users to tips. | Less direct user feedback about how the policy explanation lands in real work. |
| Simulation with policy tips for a narrow pilot | Policy behavior plus user questions and feedback about the tips. | Requires communication and a clear channel for reporting confusing or disruptive workflows. |
| Broad simulation scope | Potentially more varied activity and matches to assess. | More event volume and review effort; breadth is useful only if the team can examine the results. |
| Narrow pilot scope | More manageable feedback and closer review of a defined group’s workflows. | May not expose activity patterns found in other teams, locations, or workloads. |
Explain why users are seeing tips and where they should report a blocked or confusing workflow if enforcement follows. A tip is a communication and feedback opportunity; it does not, by itself, establish that the policy is accurate or that a workflow is safe to restrict.
Review events and tune the policy with evidence
Bring simulation results, alerts, Activity explorer events, and pilot feedback together. A raw match count alone cannot tell you whether a policy is successful: each match needs to be understood in light of the intended risk and the business activity involved.
Rank #2
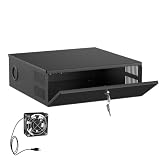
- LOCKABLE DVR SECURITY ENCLOSURE: Made from durable 16-gauge cold rolled steel with a powder-coated finish, this NVR security enclosure provides reliable protection against impact, dust and daily use. The front key lock helps prevent unauthorized access, tampering, and accidental shutdown of your recording system.
- BUILT-IN COOLING FAN & VENTILATED DESIGN: Built-in low-noise AC-powered cooling fan and dual-side ventilation grilles help maintain airflow and reduce heat buildup during continuous 24/7 DVR and NVR operation. The removable top cover design allows easy access for equipment setup, maintenance, and upgrades.
- VERSATILE SECURITY EQUIPMENT PROTECTION: Measures 15.45" × 5.3" × 15.35" and fits most DVR, NVR, CCTV systems, PoE switches, routers, network equipment, and surveillance accessories. Ideal for home security systems, business surveillance, retail stores, schools, and commercial environments.
- CABLE MANAGEMENT KNOCKOUTS: Avoid cluttered wires and messy setups in your server room or office. Designed with four 1.8-inch diameter cable knockout ports featuring pre-installed protective rubber grommets, this NVR lock box routes power cords, coaxial cables, and Ethernet cables while helping protect wires from scratches.
- FLEXIBLE INSTALLATION & READY TO USE: No assembly required. Includes mounting hardware for quick installation on walls, racks, or desktops, helping maximize space in compact environments. This CCTV security enclosure is a practical security enclosure for homes, businesses, retail stores, schools, and commercial locations.
Microsoft’s DLP guidance identifies several areas teams may refine as they learn from outcomes:
- Scope: Locations, people, and the instances of a location covered by the policy.
- Detection: Conditions and sensitive information definitions.
- Response: Actions, including whether a less impactful audit or allow behavior is suitable while validating the policy, or whether stronger restrictions are necessary to meet the objective.
- Context: Restricted apps and sites where those apply to the scenario.
Keep a record of why a change was made and what evidence prompted it. If you change a material condition, scope, or action, simulate the changed policy and review its results before using it to justify broader enforcement. Tuning is an ongoing control-design loop, not a one-time cleanup after launch.
Free tools Windows power users keep installed
One-click scans. No signup required.
Make legitimate exceptions bounded and reviewable
Microsoft’s guidance supports refining scope and conditions, including using includes and excludes. The organization still needs to decide how legitimate exceptions are requested and governed; the sources do not prescribe a universal exception workflow.
As a practical local process, require each exception to have:
- a named business owner and a clear reason tied to a workflow;
- a narrowly defined user, data, location, or activity scope;
- an accountable approver and a record of the decision;
- a review date and a way to expire, remove, or renew the exception;
- a check that the exception does not silently defeat the policy’s control objective.
Repeated requests for the same workflow may point to a policy condition that needs adjustment, a process that needs redesign, or a recurring business risk that requires an explicit decision. Treat the request as evidence to assess, not automatic proof that the policy should be weakened.
Rank #3
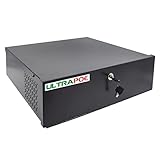
- Heavy Duty 18x18x5in DVR Lock Box: Secure storage solution for DVR/NVR, POE Switch, video baluns, and other surveillance equipment
- Spacious & Versatile Design: Accommodates all types of DVRs, NVRs, POE switches, and video baluns with included AC110/220V fan, keys, power cord, and fixing screws
- Durable Construction: 16-gauge heavy-duty steel design ensures maximum security with 18x18x5in exterior dimensions for long-lasting protection
- Optimized Interior Dimensions: 17.7 inch width, 15.7 inch depth, and 4.7 inch height provide ample space with superior cooling through included fan and power cord
- Convenient Setup Features: Pre-drilled knock-outs for easy cable management with included mounting bolts, rubber feet, and power connector for hassle-free installation
Expand only when the review process is ready
Microsoft describes widening the policy to its intended location instances when moving to enforcement, then continuing to monitor and tune it. Before that change, confirm that the pilot supports the control objective, feedback has been addressed, event triage is staffed, and exceptions have owners and review dates.
- Policy results have been reviewed against the intended risk, not just counted.
- The team can review alerts and events and route meaningful issues to the right owner.
- Users know what a policy tip means and where to report a legitimate workflow problem.
- Exceptions are documented, bounded, and scheduled for review.
- The response action is no more disruptive than necessary to meet the stated objective.
Microsoft’s DLP overview says policies generally take effect about one hour after being turned on. Treat that as product guidance rather than a guaranteed propagation time, and verify the current documentation and tenant behavior before scheduling a change window.
Measure adoption locally, not against invented benchmarks
The reviewed Microsoft deployment and planning guidance describes observing matches, alerts, locations, types, and severity, but does not set universal adoption targets or success thresholds. The following are suggested local measures, not Microsoft-mandated metrics. Choose a baseline, a review cadence, and an owner for each measure; set thresholds according to your risk tolerance, data, and business process.
- Policy accuracy: Share of reviewed matches judged to represent the intended sensitive data and activity; track validated false positives separately from unresolved events.
- Exception handling: Request volume, time to decision, share of exceptions with a business owner and review date, and repeat requests for the same workflow.
- Workflow impact: User-reported disruption, support tickets associated with the policy, and affected business processes.
- Adoption and understanding: Pilot participation, completion of relevant communication or training, recurring questions, and policy-tip feedback.
- Operational readiness: Share of alerts reviewed within the team’s own service target and share of policy changes that completed simulation review before enforcement.
- Control outcomes: Intended matches and high-risk events handled through the organization’s response process.
Use the scorecard to trigger investigation and decisions, not to reward a low event count in isolation. A lower count could reflect a better-tuned policy or a scope gap; interpretation depends on what the control is meant to detect and whether the relevant activity is visible.
Plan for changed work, not just configured settings
Microsoft cautions that DLP can change business processes and user culture and advises planning, testing, and tuning to minimize inadvertent disruption. Its deployment guidance warns that a haphazard, rushed rollout can negatively affect business processes and frustrate users. Communication, feedback handling, event review, and exception decisions are therefore part of the technical rollout—not follow-up tasks to improvise after users encounter a restriction.
Recommended Free Tools
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

