
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
To prevent a polling retry from sending the same alert or repeating a side effect, derive a stable idempotency key for the logical work item, claim that key atomically in durable storage, and reuse it on every retry. A practical lifecycle is unseen, in progress, completed, and failed/retryable. This four-state model is a design aid, not an industry-standard protocol: the right states and recovery rules depend on what your worker does.
What an idempotency key protects—and what it does not
An idempotency key identifies one logical operation across repeated attempts. If a polling worker reads the same item again after a timeout, restart, or redelivery, it should send the same key rather than create a new one for that attempt. The receiving system can then recognize the repeat and avoid repeating the operation or return its stored result.


This does not make a distributed workflow literally execute once. A request may be delivered or processed more than once, and failures can occur between a side effect and recording its result. The useful goal is an idempotent outcome: repeating the protected operation has the same effect as doing it once. AWS explains the distinction between at-most-once, at-least-once, and exactly-once behavior in its Well-Architected guidance. Scope the guarantee to a boundary, such as creating an alert record or calling a notification API, rather than claiming the entire workflow is exactly once.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsFor alerts, define what counts as the same work before choosing a key. It might mean the same source observation, the same incident, or the same notification to a recipient within a defined window. Those identities are not interchangeable: an incident that changes state or resolves and later recurs may legitimately warrant another alert. The key should reflect the alert policy you intend, not merely the polling schedule.
#1 Best Overall
Use a key that remains stable across retries
Prefer a trustworthy immutable event or work-item ID from the source. For CloudEvents, Google Cloud treats the combination of source and id as the unique identity; duplicate events share that identity. If the polling API has no event ID, derive a deterministic key from immutable source identity and the intended operation. A useful conceptual shape is source + entity/event identity + operation/version. Add a time bucket only when the product semantics define separate work for each bucket.
Do not include the time of each attempt: a fresh timestamp can turn every retry into a new key. AWS also cautions that timestamps are risky because of clock skew and collisions, and that inconsistent key generation defeats deduplication. Conversely, a key that is too broad can collapse distinct work into one operation. Keep key construction consistent across workers, deployments, and replay paths.
If the same key can arrive with different business parameters, compare immutable fields or a canonical request hash. A repeated key with matching content is a duplicate; a repeated key with changed content is an integrity conflict, not a harmless repeat. Stripe’s API illustrates this distinction: while a key is retained, it returns the first saved result for matching parameters and errors if parameters differ. That is Stripe-specific behavior, not a universal protocol; see Stripe’s idempotent request documentation.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Model the work with four explicit states
This lifecycle is a practical synthesis for a polling worker, not a published standard. AWS describes tracking states such as pending, completed, and failed; the unseen state below means no durable record exists yet. An implementation may need fewer states or additional ones, such as terminal failure.
| State | Meaning | Worker behavior |
|---|---|---|
| Unseen | No durable record exists for the logical key. | Attempt an atomic claim before doing side effects. |
| In progress | A worker has durably claimed or recorded the operation. | Competing attempts must not repeat the side effect. Wait, skip, or consult the record according to the lease and recovery policy. |
| Completed | The outcome and, where useful, result are durably recorded. | For a matching duplicate, reuse the saved result or acknowledge it as a no-op. |
| Failed/retryable | An attempt failed, but another attempt is allowed. | Retain enough error and work information for safe retry; define whether to reclaim the record or transition it back to unseen. |
Separate transient failures from permanent conflicts. A temporary network error may be retryable; a key reused with changed business content should be rejected or quarantined rather than silently retried as though it were the same operation. If a failure is terminal, model that explicitly and route it to the appropriate dead-letter or operator workflow.
Implement the polling flow without a check-then-act race
- Read and identify: read the source item and derive its stable logical key from the event identity or deterministic business identity.
- Claim atomically: create or claim the in-progress record using a uniqueness constraint, atomic create, transaction, lock, or equivalent concurrency control. A separate “check whether key exists” followed by “insert if absent” is unsafe: two pollers can both pass the check.
- Handle an existing record: if another worker owns an in-progress key, follow the lease policy; if it is completed, return the stored result or acknowledge without repeating the effect. Compare request data before treating a repeated key as a duplicate.
- Perform the side effect: do this only after the claim is durable. Where a downstream API supports idempotency keys, pass the same logical key through rather than generating a downstream attempt key.
- Record the outcome: persist completion and the result. When related business writes and the dedupe marker share a store, make them atomic together where possible so a crash cannot leave one committed without the other.
- Recover or retry: record transient failures and retain enough information to retry safely. Route changed-payload conflicts to an error or dead-letter path and alert an operator instead of suppressing them.
Microsoft’s Idempotent Consumer pattern describes uniqueness checks, payload comparison, dead-lettering mismatches, and transactional batches that write a dedupe marker and business documents together in one partition. The transactional approach is useful when those writes must stay synchronized; the specific mechanism depends on your datastore.
Rank #3

- 2 Years of Cellular Service Included – Necto offers the most affordable cellular-enabled sensor with 2 full years of 4G LTE service included—no hidden fees, contracts, or WiFi required. With a built-in multi-network SIM card, you can remotely monitor conditions 24/7 and receive real-time alerts. After 2 years, you can renew the subscription from the app for only $6.99 a month.
- Instant Alert & 24/7 Monitoring - Keep tabs on your Home, RV, Car, or Pets from anywhere with the 3-in-1 temperature, humidity & power outage monitor. Customize the high and low temp/humidity thresholds and add up to 5 contacts for unlimited text and email alerts. Receive real-time alerts if critical changes in temp/humidity or a power loss occurs.
- Rechargeable Internal Battery - The Necto smart RV and pet monitor has a 3 day long-lasting rechargeable battery. Unlike WiFi sensors, Necto provides continuous monitoring in the event of a power outage, via its built-in battery and cellular technology. Receive instant alerts on your phone when battery power is low or if the device disconnects from the network.
- Intuitive Mobile App & Easy Setup - Our user-friendly mobile app gives you remote access to your sensor from anywhere. Use your smartphone or PC to customize alert thresholds, view past readings, and manage device settings with ease. The sensor takes minutes to install and requires no technical expertise. Simply activate the device through the app and plug it into any standard wall outlet.
- Fast Refresh & Free Data Storage - The industrial built-in temperature and humidity sensor takes readings every 10 seconds to make sure the temp/humidity are within the safe range. Every 10 minutes the most recent reading is updated on the online portal. Readings are stored on our servers for 1 year and can be downloaded anytime on a CSV file.
Plan for crashes, concurrency, and replay
A worker crashes after claiming
An in-progress record can strand work unless it has recovery semantics. Use an expiring lease, heartbeat, or another safe reclaim rule. A replacement worker should verify that the previous claim is no longer valid before taking over; otherwise, a slow original worker and its replacement may both perform the side effect.
The side effect succeeds, but completion is not recorded
This is the critical gap between the external action and your local state. A retry must use the same downstream idempotency key if available, or reconcile the downstream outcome before repeating the operation. A local completed flag alone cannot prove that an external notification was not already sent.
Two pollers claim the same key
Enforce uniqueness or serialization in the shared store. An in-memory set or per-process lock cannot coordinate separate worker instances. Every worker that can process the same logical item must see the same durable dedupe record.
Rank #4
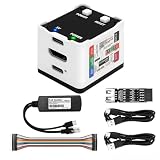
- 【Remote Control Operations Server】Sipeed NanoKVM is an IP-KVM solution based on the LicheeRV Nano RISC-V Linux single-board computer, inheriting the Nano's compact form factor and powerful capabilities. Breaking free from traditional host requirements for network connectivity and system software, NanoKVM functions as an external hardware device directly providing remote control capabilities.
- 【Powerful Interfaces】Sipeed NanoKVM features one HDMI input port that can be recognized by a computer as a display to capture screen content. One USB 2.0 port connects to the computer host, functioning as a HID device (e.g., keyboard, mouse, touchpad). It also utilizes spare TF card storage space, mounting it as a USB flash drive device.
- 【100Mbps Ethernet Support】Sipeed NanoKVM features a 100Mbps Ethernet port for network transmission of video and control signals. The Full version additionally includes an ATX power control interface (USB-C) for remote host power status monitoring and control. The Full version housing also incorporates an OLED display showing the device's IP address and KVM-related status.
- 【Server Management】Sipeed NanoKVM enables real-time monitoring and control of server operations. Supports remote desktop access and host power cycling: NanoKVM overcomes limitations requiring the host to be networked or specific system software, functioning as external hardware to provide direct remote control capabilities.
- 【Supports Remote Installation】Sipeed NanoKVM emulates a USB flash drive device, enabling mounting of installation images for system deployment or access to computer BIOS settings. The NanoKVM Lite features two serial ports for use with IPMI or connection to other development boards via web-based serial terminal interaction. Users may also expand functionality with additional accessories.
A delayed replay arrives after the record expires
Once the marker is deleted or no longer visible, the same logical work may run again. Choose retention to cover the actual retry and replay horizon, including manual backfills when relevant. Provider-specific retention is not a general recommendation: for example, Stripe says its API may remove keys once they are at least 24 hours old, after which reuse can initiate a new request. That behavior applies to Stripe’s implementation only, not to your worker’s retention policy.
A provider returns a cached failure
Some idempotency implementations save execution results as well as successes. Stripe documents that once endpoint execution begins, its first result—including a 500 response—is saved and subsequent requests with the same key return it. It also says validation failures and certain concurrent execution conflicts are not saved as idempotent results. Inspect the downstream provider’s semantics: retrying with the same key may repeat a cached failure rather than start a fresh attempt.
Free tools Windows power users keep installed
One-click scans. No signup required.
Choose the duplicate response and retention policy deliberately
Deduplication is only as effective as the lifetime and visibility of its record. Store the minimum durable information needed to recognize the key, enforce uniqueness, compare relevant request data, and return or reconcile an outcome. AWS cautions against using the entire payload as the idempotency record; a hash plus the necessary identity and state may be more appropriate, depending on the operation.
- Identity: upstream immutable event ID when trustworthy, otherwise a deterministic identity for the entity and operation.
- Atomicity: unique constraint or atomic create for claiming; transaction or equivalent when the marker and business writes must commit together.
- Duplicate response: cached prior result, no-op acknowledgement, or wait while a valid in-progress claim completes.
- Recovery: lease and reclaim for abandoned work, with explicit handling for retryable and terminal failures.
- Retention: duration based on real retries, provider redelivery, and replay/backfill practices—not an unrelated provider TTL.
- Mismatch handling: reject, quarantine, and alert when the same key carries changed business content.
What the cloud guidance supports
Google Cloud recommends pairing retries with idempotent event handlers and recording processed event IDs; for CloudEvents, the duplicate identity is the (source, id) pair. See Google Cloud’s Eventarc retry guidance. AWS recommends unique tokens, durable state tracking, concurrency controls, consistent key generation, and passing tokens downstream in its Well-Architected idempotency guidance.
AWS Durable Execution further distinguishes at-least-once and at-most-once behavior per retry and cautions that neither retries alone nor at-most-once handling at one boundary guarantees a single end-to-end workflow execution. Its guidance demonstrates retaining the same token across replay: AWS retry and idempotency best practices. These principles support the stable-key and durable-state design; they do not prescribe the four state names or an alert-specific suppression policy.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

