
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Yes, a hacker can affect a car’s physical functions in some circumstances, but there is no universal method that lets someone remotely take over every modern vehicle. A connected car has wireless and wired entry points; the danger depends on whether an attacker can exploit a weakness and reach systems that control vehicle functions. A well-known 2015 demonstration affected a particular 2014 Jeep Cherokee configuration—it was not evidence that all cars are vulnerable in the same way.
How could an attacker get into a connected car?
A modern vehicle is a networked computer system. Cellular connections, Wi-Fi, Bluetooth, USB ports, infotainment systems, telematics services, diagnostic connections, companion apps, cloud accounts, and aftermarket devices can all be part of its attack surface. An exposed interface is not automatically a way to control the car: an attacker needs a weakness, a route to exploit it, and a path from the compromised component to the function they want to affect.
From an entry point to a vehicle function
- Reach an exposed component. Depending on the vehicle and its configuration, that might mean a remotely accessible cellular or Wi-Fi service, a compromised app or account, a nearby Bluetooth connection, a USB device, or a diagnostic or aftermarket device.
- Exploit a weakness. The attacker may try to run unauthorized software or misuse the component’s access. The precise opportunity depends on the vehicle’s software and security controls.
- Look for a route into other systems. Infotainment and telematics components may communicate with other vehicle electronics. If the networks are not adequately separated, or messages are not sufficiently authenticated and validated, a compromise could have a path farther into the vehicle.
- Attempt an effect. What the attacker can actually do depends on the vehicle’s architecture, gateways, ECU permissions, and the access they obtained. A compromised app account, for example, is not the same thing as access to a braking controller.
CISA identifies cellular, LTE/5G, Wi-Fi, USB, and Bluetooth as possible routes for malicious access to vehicle software. The risk is not simply that a car has these connections; it is whether a weakness in a connected component can be used to cross into systems with more consequential functions.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
What does “take control” mean?
There is no single capability called “car control.” A compromise might expose information or affect infotainment without reaching driving functions. Other attacks may target locks, starting or stopping, or driver-assistance functions. Reaching a controller involved in steering assistance, braking, or propulsion is a more serious possibility, but it depends on the particular vehicle and the attacker’s access. A connection to the car does not by itself prove access to these safety-critical systems.
#1 Best Overall

- 2 Stage Shock Sensor
- Door, Bonnet & Boot Protection
- Engine Immobilization
- Parking Light Flash (Arm, Disarm & Trigger)
- Keyless Entry
Electronic control units (ECUs) manage different vehicle functions. They communicate over internal networks that may include a Controller Area Network (CAN) bus. Gateways, network segmentation, authentication, and message validation can limit which components can communicate and what commands they can accept. The design differs by make, model, year, software version, and configuration, so a finding about one vehicle cannot safely be generalized to another.
What did the Jeep Cherokee demonstration prove?
In 2015, security researchers Charlie Miller and Chris Valasek demonstrated remote exploitation of an unaltered 2014 Jeep Cherokee through its cellular-connected infotainment system. Their research showed that, in that particular configuration, a path from the connected infotainment system could reach vehicle functions and produce physical effects. It was a controlled research demonstration, not evidence of a routine attack against every Jeep or every connected car.
Rank #2

- -Way Security + Remote Start System with 5-Button LCD Transmitter
- 5-button sidekick remote control transmitter
- 1 mile range
- 4-Channel vehicle security system
- Door and trunk triggers
The U.S. Government Publishing Office’s 2019 hearing record says the researchers found 2,695 vehicles with a similar vulnerability during a short scan. A 2025 USENIX retrospective says the research led to a recall of about 1.5 million vehicles. Those figures describe that case and its aftermath; they do not measure how many vehicles today are vulnerable to the same attack.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsThe lasting lesson is about the route between systems: a remotely reachable weakness in a non-driving component can become safety-relevant if the vehicle does not sufficiently contain it. The Jeep case does not establish that a single exploit works across makes or that a remote attacker can routinely steer any modern car.
Rank #3
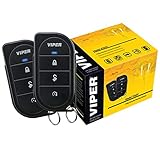
- 3-Channel 1-way Security System with Keyless Entry 4-Button remotes. Additional options include remote starter & GPS Tracking.
- FailSafe starter kill.
- Anti-carjacking & Panic Alarm Feature
- Revenger six-tone soft-chirp siren and parking light alarm response.
- Bright blue status LED warns thieves and gives you info about the system
How do car cyberattacks differ?
- Remote vehicle-system compromise: An attacker reaches a connected vehicle component over a network and attempts to move from that component to other vehicle systems. Whether safety-critical functions are reachable depends on the vehicle’s design.
- App or cloud-account compromise: Someone gains access to a connected-car account, potentially exposing account-linked data or using the remote features that the service provides. This is not automatically access to the car’s internal networks.
- Keyless-entry theft: An attacker targets the keyless-entry system or the key fob’s signal. This is distinct from compromising the vehicle through its cellular connection or taking control of its driving systems.
- Local or physical access: An attacker uses access to the vehicle, its diagnostic connection, or an installed device. This is different from exploiting a weakness remotely, and physical access may change what systems can be reached.
What can owners do to reduce exposure?
Owner precautions can reduce avoidable risks, but they cannot guarantee that a vehicle is immune to vulnerabilities in its design or software. Follow the manufacturer’s instructions for the specific vehicle and check its recall status with the manufacturer or relevant regulator.
- Install manufacturer updates. Keep vehicle software and firmware current, and update companion mobile apps. Use the maker’s official instructions and update channels.
- Secure connected-car accounts. Use a unique password and enable multifactor authentication if the service offers it. Protect the email account used to recover or manage the vehicle account as well.
- Review installed devices. Remove unknown aftermarket telematics trackers, remote starters, or diagnostic dongles. For a device you rely on, ask its installer or manufacturer about security updates and support.
- Protect keyless-entry credentials. Follow the vehicle maker’s guidance for safeguarding key fobs and keyless-entry features. This addresses keyless-entry risks, which are separate from remote compromise of vehicle software.
- Report suspected vulnerabilities responsibly. Contact the manufacturer’s security team or vulnerability-disclosure channel; NHTSA or CISA may also be appropriate contacts. Do not probe vehicles or systems without authorization, and do not attempt to reproduce a suspected exploit on public roads.
What should manufacturers and fleets prioritize?
NHTSA’s 2022 cybersecurity best-practices guidance recommends a voluntary, risk-based program across a vehicle’s lifecycle. Its recommendations are not a guarantee that a vehicle is unhackable; they are principles that manufacturers and fleets need to adapt to their own systems and risks.
Rank #4

- 【2-Pack Double Protection】: Each set includes 2 car alarm units + 1 wireless remote, so you can secure two vehicles at once, or place one on the front and one on the rear of a single car. The remote can pair with multiple hosts - great for couples, families, or a car + motorcycle combo
- 【Smart 3D Motion Sensor, Fewer False Alarms】: Built-in 3D acceleration sensor with AI algorithm detects vibration, prying and forced entry, while intelligently filtering out noise from passing cars, rain or thunder - high sensitivity without the constant false alarms that cheap alarms cause
- 【108dB Siren + Red Warning Light】: First vibration triggers a short beep with red flashing as a warning; a second sets off a 30-second loud 108dB siren with strobe-like flashing that scares off thieves. 3 volume levels (108/102/96dB) suit neighborhoods, lots or busy streets
- 【Magnetic Mount, No Drilling】: A strong magnet holds the alarm in place - no tools, no wiring, no sticky residue, and you can move it between cars anytime. The anti-UV PC housing resists high heat and cold, so it stays stable even in a car parked under the summer sun
- 【66ft Wireless Remote & Long Battery】: Arm, disarm or locate your vehicle from up to 66ft (20m) away. Powered by 2 AAA batteries, the unit runs 6+ months and the remote lasts up to 2 years. Also works for home doors, bikes, ebikes, luggage - multi-scene security
- Threat modeling and secure architecture: Identify likely attack paths early, including paths from connected or non-safety systems toward safety-relevant networks.
- Interface protection and segmentation: Limit unnecessary access from cellular, Wi-Fi, Bluetooth, diagnostic, and other external interfaces. Use gateways and separation to constrain what a compromised component can reach.
- Secure communications and updates: Authenticate and validate messages where appropriate, and build update mechanisms that can deliver fixes securely and reliably over the vehicle’s service life.
- Monitoring and response: Watch for relevant security events, define incident-response procedures, and coordinate with suppliers and other affected organizations.
- Vulnerability disclosure and information sharing: Provide a way for researchers to report flaws responsibly and share relevant information through industry channels such as Auto-ISAC.
NHTSA has also described how wireless paths and non-safety systems such as telematics can become proxies into safety-relevant networks, and says its Vehicle Research and Test Center has verified reported vulnerabilities through lab testing. In an Auto-ISAC keynote, the agency said it had assessed more than 75 vehicle-cybersecurity cases over roughly the preceding decade. That figure reflects the cases its teams assessed, not a count of successful attacks on cars.
How should you judge a claim that a particular car is “hackable”?
Ask what the evidence actually demonstrates. A credible, vehicle-specific claim should identify the model and relevant software or configuration, explain whether access was remote, local, or physical, and distinguish an infotainment or account compromise from access to safety-critical systems. A vulnerability report or controlled demonstration is not proof that an exploit is widespread, currently usable, or applicable to other vehicles.
Best Value

- Real-time alerts — Receive notifications for impacts, door openings, and other disturbance alerts so you can act fast.
- Track your vehicle’s location — Use the Ring app to view your vehicle on a map with period updates.
- No ongoing fees — Track and protect your car with no monthly subscription or hidden fees.
- Easy car installation — Start tracking your car right away with no tools, wiring, or complicated setup. Compatible with most vehicles.
- Connects to your OBD-II Port — Powered by your car while driving, with a built-in backup battery that lasts up to 7 days when parked.
For comparisons between vehicles, useful questions include how exposed their wireless interfaces are, how well infotainment and telematics are separated from safety-critical ECUs, how they authenticate and validate internal messages, how long software updates are supported, how the manufacturer handles vulnerability reports and incidents, and whether aftermarket devices introduce additional access. Without current, model-specific evidence, those factors do not justify labeling a particular model safe or unsafe.
Where can readers learn more?
Craig Smith’s The Car Hacker’s Handbook: A Guide for the Penetration Tester (No Starch Press, March 2016) is a technical book covering topics including CAN bus, diagnostics, ECUs, infotainment, wireless systems, and test benches. Its technical detail is intended for security learning and authorized testing; it is not a reason to experiment on a public vehicle.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →
