
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Review AI-generated changes as you would work from an unfamiliar contributor: understand what changed, verify its behavior and security in context, run the right automated checks, and require an accountable human to approve the pull request before merge. AI authorship alone does not show that code is unsafe, and passing tests or clean scans do not prove it is safe.
What the review gate should require
Every AI-generated change needs a responsible owner who can explain what it does and approve it explicitly. OWASP advises requiring developer approval before merging and treating that approval as confirmation that the developer reviewed and understood the change. AI-generated review comments do not replace that accountability.


Use the same baseline engineering gates for code written by a person or generated with AI. Give heightened attention to authorization, input handling, dependencies, and changes to build, CI, or deployment files, because these can affect security beyond the lines that appear to implement a feature.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsHow to review an AI-generated pull request
-
Understand the purpose and scope
Read the pull request description and focused diff. Identify the intended behavior, changed files, affected components, and existing security controls. For a routine pull request, begin with a diff-based review rather than treating the change as an unexplained block of code.
#1 Best Overall
Sale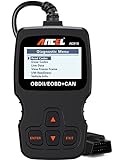 ANCEL AD310 Classic Enhanced Universal OBD II Scanner Car Engine Fault Code Reader CAN Diagnostic Scan Tool, Read and Clear Error Codes for 1996 or Newer OBD2 Protocol Vehicle (Black)
- CEL Doctor: The ANCEL AD310 is one of the best-selling OBD II scanners on the market and is recommended by Scotty Kilmer, a YouTuber and auto mechanic. It can easily determine the cause of the check engine light coming on. After repairing the vehicle's problems, it can quickly read and clear diagnostic trouble codes of emission system, read live data & hard memory data, view freeze frame, I/M monitor readiness and collect vehicle information
- Sturdy and Compact: Equipped with a 2.5 foot cable made of very thick, flexible insulation. It is important to have a sturdy scanner as it can easily fall to the ground when working in a car. The AD310 OBD2 scanner is a well-constructed mechanic tool with a sleek design. It weighs 12 ounces and measures 8.9 x 6.9 x 1.4 inches. Thanks to its compact design and light weight, transporting the device is not a problem. The buttons are clearly labelled and the screen is large and displays results clearly
- Accurate Fast and Easy to Use: The AD310 scanner can help you or your mechanic understand if your car is in good condition, provides exceptionally accurate and fast results, reads and clears engine trouble emission codes in seconds after you fixed the problem. This device will let you know immediately and fix the problem right away without any car knowledge. No need for batteries or a charger, get power directly from the OBDII Data Link Connector in your vehicle
- OBDII Protocols and Car Compatibility: Many cheap scan tools do not really support all OBD2 protocols. AD310 scanner as it can support all OBDII protocols such as KWP2000, J1850 VPW, ISO9141, J1850 PWM and CAN. This device also has extensive vehicle compatibility with 1996 US-based, 2000 EU-based and Asian cars, light trucks, SUVs, as well as newer OBD2 and CAN vehicles both domestic and foreign. Pls confirm with our customer service whether it is compatible with your vehicle before purchasing
- Home Necessity and Worthy to Own: This is an excellent code reader to travel or home with as it weighs less and it is compact in design. You can easily slide it in your backpack as you head to the garage, or put it on the dashboard, this will be a great fit for you. The AD310 is not only portable, but also accurate and fast in performance. Moreover, it covers various car brands and is suitable for people who just need a code reader to check their car
-
Check behavior against requirements
Ask what the change is supposed to do, which inputs it accepts, what data it reads or changes, and what should happen on errors or unexpected input. Check both the intended path and failure paths. If the responsible developer cannot explain the change, OWASP guidance says it is not ready to merge.
-
Inspect security-sensitive logic
Trace data from input to use and verify that authentication and authorization checks apply to the right users and resources. Examine validation, business rules, error handling, cryptographic operations, and query construction. In particular, look for omitted access checks, inadequate validation, weak or deprecated cryptography, and queries assembled by concatenating strings.
-
Verify new dependencies before installation
Check that each package name exists, is the intended project, and is appropriate for the application. Do not install an unfamiliar dependency just because generated code imports it: OWASP warns that a hallucinated package name could be registered by an attacker. Assess the dependency through your normal dependency-review process before accepting it.
Recommended: Update Every Outdated Driver on Your PC in One Scan - Free →Recommended: Fix Windows Errors and Clear Junk Files in Minutes - Free Scan →Special offer. See more information about Outbyte and uninstall instructions. Please review EULA and Privacy policy. -
Review build, CI, and deployment changes closely
Inspect package scripts, CI workflows, Dockerfiles, build configuration, deployment files, agent instruction files, and hooks. Look for new network access or shell execution, privileged triggers, broader permissions, and unpinned third-party actions. These files may execute automatically or shape later generated work, so a small diff can have effects beyond the feature being reviewed.
-
Run the established automated checks
Run pull-request tests and the available static analysis (SAST), dependency analysis (SCA), and secret scanning. Apply the same required gates regardless of whether a person or an AI produced the code. Treat results as evidence about the checks performed, not as a substitute for understanding the change.
-
Assess proposed fixes before accepting them
An AI review or remediation tool can surface candidate findings, but inspect its proposed diff and confirm that the fix preserves intended behavior. GitHub’s documentation for its AI security and quality features says developers should review suggestions, verify that they meet expectations, and run CI testing after applying fixes.
Rank #4
Sale UJS Rocco OBD2 Scanner Bluetooth for iOS & Android, No Subscription(Black)
- AI-Powered Car Health Reports in Minutes: Get beyond confusing codes. Our Rocco OBD2 scanner connects to your phone and uses AI intelligence to analyze live data and freeze frame information, generating easy-to-understand health reports and actionable repair advice—no mechanic knowledge needed
- Truly Wireless & Ultra-Compact Design: Weighing only 0.98 ounces, this mini scanner plugs seamlessly into your OBD2 port and stays there. No cables, no batteries, no clutter. Leave it in your car for 24/7 monitoring and connect via Bluetooth 5.4 whenever you need a diagnosis
- Visualize Your Car's Performance in Real-Time: See your engine's heartbeat with stunning real-time data graphs and charts on your phone screen. Monitor RPM, coolant temperature, and oxygen sensor voltage visually to pinpoint intermittent issues that simple code readers miss
- One-Tap Full Vehicle Scan & Code Clearance: Stop the guesswork. The app's "Full Vehicle Scan" feature quickly checks all systems and gives a simple Pass/Fail result. Read and clear check engine lights instantly after repairs, turning off the warning lamp and getting you back on the road
- Universal Compatibility with Free Lifetime App Updates: Works with all OBD2 protocol vehicles from 1996 and newer (cars, trucks, SUVs). The free app supports iOS & Android and receives lifetime updates with new features and expanded fault code libraries (65,000+ codes), ensuring it never becomes obsolete
-
Record accountable approval
Assign an owner and require explicit human approval before merge. Use your ownership rules to route sensitive modules and high-risk paths to reviewers with the appropriate context; do not let a large volume of generated changes bypass established review capacity.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Special offer. See more information about Outbyte and uninstall instructions. Please review EULA and Privacy policy.
Which review scope fits: the diff or the whole codebase?
Diff-based and baseline reviews answer different questions. OWASP describes both as useful approaches rather than alternatives that must be chosen once for an entire engineering program.
Best Value
| Review approach | Scope | Best suited to | Main emphasis |
|---|---|---|---|
| Diff-based | Changed files and their effect on existing controls | Routine pull requests and commits | Understand the change, assess its impact, and prioritize risky modifications |
| Baseline | The application and its dependencies across the codebase | New applications, major releases, legacy-system onboarding, compliance work, or post-incident analysis | Architecture, boundaries, dependencies, security history, and broad codebase coverage |
A focused pull-request review can sit within a wider baseline review program. A diff review checks what a change may have broken; a baseline review looks for issues and gaps that may exist outside any one pull request.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What automated checks can—and cannot—tell you
Each check covers a different slice of risk. Static analysis flags code patterns; software composition analysis checks dependencies; secret scanning looks for exposed credentials; tests exercise specified behavior; and human review evaluates business logic and context. None makes the others unnecessary.
- Tests: Check the behavior they actually assert. A passing suite can still encode the wrong expectation or omit an important security case. OWASP cautions against treating AI-generated tests or pass rates alone as evidence of security.
- Scanners: Use findings to direct attention and investigate relevant paths. OWASP recommends SAST, SCA, and secret scanning on every pull request, while warning that clean scans are only the beginning: scanners may miss broken access control and business-logic flaws.
- AI-assisted review: Treat generated summaries, alerts, and fixes as suggestions to verify. GitHub documents AI suggestions for CodeQL alerts, generic secret detection, custom secret-pattern generation, and code-quality analysis; these are product capabilities, not independent evidence that a change is secure.
- Manual review: Use it to reason about application-specific rules, complex security implementations, and how a change interacts with existing controls. OWASP positions secure manual review as complementary to automated testing.
Protect sensitive context used by AI tools
Review what the coding assistant can access or send to its provider. Credentials, personal data, and proprietary code may require special handling. Check the tool’s settings and file exclusions against your organization’s data-handling requirements before using it on sensitive material.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Use a whole-codebase review when the question is broader
A pull-request gate cannot by itself establish the security posture of an entire application. For a new application, major release, legacy-system onboarding, compliance need, or post-incident analysis, a baseline review can examine architecture, trust boundaries, dependencies, security history, and coverage across the codebase. Continue diff-based review for subsequent changes; the two scopes serve different purposes.
Standards context for AI-assisted development
NIST Special Publication 800-218A, published July 26, 2024, augments the Secure Software Development Framework (SSDF) version 1.1 with practices and recommendations specific to generative AI and dual-use foundation models. NIST says it is intended to be used with SP 800-218A and SP 800-218. It provides development-practice context; it does not turn an automated check or approval into proof that a particular change is safe.
Quick Recap
Guidance to consult
- OWASP Secure Coding with AI Cheat Sheet
- OWASP Secure Code Review Cheat Sheet
- OWASP DevSecOps Guideline: IDE and AI-Assisted Development Security
- OWASP DevSecOps Guideline: Secure Code Review
- GitHub Docs: Application card—GitHub security and quality AI features
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

