
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Obfuscation can make a mobile app harder to reverse engineer, but it cannot make the app trustworthy. Treat it as one resilience layer—not a substitute for server-side authorization, secure data handling, protected communications, or sound architecture. A modified client can still be inspected, and checks implemented only in that client can be bypassed.
Does obfuscation make a mobile app secure?
No. Code obfuscation changes how understandable an app binary is, raising the effort required to inspect or modify it. Anti-debugging and anti-tampering measures can add friction, but a capable attacker who controls the device or analysis environment may bypass them. OWASP puts the boundary plainly: “Anti-tampering or obfuscation techniques must not be used as a substitute for proper security architecture.” See OWASP MASVS-RESILIENCE.
That distinction matters most for trust decisions. Do not make client-side checks or hidden code the sole barrier to privileged actions, and do not treat obfuscation as a way to secure long-lived credentials embedded in the app. Design the system so that sensitive authorization decisions are enforced by trusted components, rather than relying on an attacker being unable to understand or alter the client.
What are mobile app security best practices?
Start with the app’s data, users, deployment, and likely attackers, then cover the whole attack surface—not just the binary. OWASP’s Mobile Application Security Verification Standard (MASVS) organizes controls across storage, cryptography, authentication and authorization, network communication, platform interaction, code quality, resilience, and privacy. Its scope is intended for mobile app architects, developers, and testers across platforms and deployment scenarios.
Free tools Windows power users keep installed
One-click scans. No signup required.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
Use the control areas as a coverage checklist, not as a claim that one configuration fits every app. For each relevant threat, decide what could happen if an attacker obtains a device, repackages the app, compromises an account, or intercepts traffic. Then identify the control, its residual risk if bypassed, its effect on users and operations, and how the team will verify it.
Protect data and cryptographic material
Identify what the app stores and what would be exposed if a device or app data were accessed. Protect stored data and cryptographic material according to the app’s threat model; do not assume a renamed symbol or hidden code provides that protection. MASVS includes storage and cryptography as distinct control areas because binary resilience alone does not address data exposure.
Make authentication and authorization resilient to a modified client
Assess account misuse and unauthorized actions separately from reverse engineering. A hidden endpoint or obfuscated authorization branch is not an authoritative security boundary: a modified client can attempt to skip local checks. Keep sensitive authorization decisions out of places where a modified client can simply bypass them, and test the relevant server and client behavior.
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
Secure network communication
Consider what an attacker could learn or alter through intercepted traffic. Network communication is its own MASVS area; obfuscation does not protect data in transit. Choose and verify communication controls for the app’s actual deployment and threat model.
Review platform interaction, code quality, resilience, and privacy
Account for how the app interacts with the operating system and other components, examine code for weaknesses, and decide whether resilience measures are warranted. Include privacy in scope as well: protecting code does not by itself establish that app data and behavior meet privacy expectations.
How to apply obfuscation without relying on it
Use obfuscation where making analysis or tampering more costly contributes to a defined resilience goal. Before adopting a control, state which threat it addresses—such as reverse engineering or tampering—and what remains possible if the control is bypassed. Avoid treating a more opaque binary as evidence that secrets, authorization, or user data are safe.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
For Android, code shrinking and obfuscation can be part of release hardening. Preserve symbols required by reflection, serialization, or frameworks, and validate the release artifact. Also make sure the team can interpret crash reports using the matching deobfuscation information; otherwise, hardening can make production failures harder to diagnose. These are practical release checks, not a claim that Android guidance mandates a particular obfuscator configuration.
Anti-debugging and anti-tampering may supplement that layer, but should be assessed against the same bypass question. If defeating a measure would grant an attacker authority or expose a secret, the underlying design needs another control.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteAndroid: secure the build, permissions, and signing keys
The Android Open Source Project’s app security best practices recommend manual and automated source review, running an Android linter and addressing its findings, and using appropriate automated analysis for native code. Review the official documentation for implementation details and current tool behavior.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
- Permissions: request only permissions that are relevant and necessary for the app’s functionality.
- Signing keys: handle signing keys as sensitive assets, with industry-standard protections and limited, auditable access. The guidance includes an HSM-backed process as an example of controlled access.
- Release validation: inspect and test the release artifact, including obfuscation-dependent behavior and crash-reporting workflows.
Signing establishes an important release and identity control, but it does not prove that application logic cannot be analyzed or changed in an attacker-controlled environment.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.iOS: understand what code signing does—and does not do
Apple’s code-signing documentation says executable code on iOS and the other operating systems listed there must be signed using an Apple-issued certificate. Treat this mandatory platform integrity control as part of the app’s security model, not as a guarantee that its logic is impossible to inspect.
The cited Apple documentation establishes the signing model; it does not establish a general requirement or guarantee for third-party source-code obfuscation. Do not assume Android build-hardening advice directly specifies an iOS obfuscation approach.
Best Value
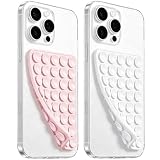
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Define and verify controls with OWASP guidance
MASVS helps teams define which mobile security controls are in scope. OWASP pairs it with the Mobile Application Security Testing Guide (MASTG) for testing guidance and the Mobile Application Security Weakness Enumeration (MASWE), a catalog of mobile weaknesses. Together they provide a way to connect requirements, testing, and weakness analysis rather than treating a build setting as proof of security.
Adapt test cases to the app’s threat model, platforms, and deployment. Include code review and automated analysis, and verify that controls work in the release context—not only in a development build. OWASP’s Mobile Application Security Cheat Sheet also highlights least privilege, trusted third-party components, integrity measures, and post-deployment updates as practices to consider.
Security work continues after release: review new findings and component changes, maintain an update process, and reassess controls when the app’s data, features, or deployment change. For teams that need independent verification, a mobile application security assessment or penetration test scoped to a defined standard can help evaluate whether implemented controls withstand testing; the assessment should be tied to the app’s actual requirements and risks.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problems
