
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Banks and ATM operators defend against malware with several layers: protecting ATM compartments, controlling what software can run and how the machine boots, securing device and network communications, monitoring suspicious activity, and rehearsing incident response. No single control covers every route into an ATM or the bank systems connected to it.
What counts as an ATM malware attack?
ATM malware can be used to steal card and PIN data, make a compromised ATM dispense cash, or interfere with communications between an ATM and its acquirer. Europol’s IOCTA 2015 describes four approaches:

- Software skimming: Malware on the ATM’s PC intercepts card and PIN data.
- Jackpotting: Malware takes control of the ATM PC and directs the cash dispenser to dispense money.
- Black boxing: A jackpotting variant in which an attacker uses a separate computer to communicate with the cash dispenser.
- Man-in-the-middle attacks: An attacker manipulates communications between the ATM PC and the merchant acquirer’s host. Europol says the malware must be present in a high software layer of the ATM PC or within the acquirer’s network.
These methods involve different components and require different safeguards. In particular, a machine dispensing cash does not by itself prove that its ATM software was infected.
How do banks tell if an ATM has been tampered with or infected?
Detection combines signals from the physical machine, its software and devices, network traffic, and bank-side transaction systems. The European Association for Secure Transactions (EAST) recommends monitoring ATM compartment openings and loss of communication with security-relevant devices. Its guidance also calls for file-integrity monitoring and controls on software and connected devices. See EAST’s countermeasures against ATM malware and black-box attacks.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall
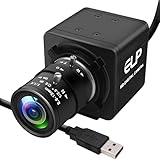
- 1080P HD USB Camera with CMOS IMX323 Sensor: This USB industrial camera features a 1920×1080 resolution CMOS IMX323 sensor, delivering sharp images and accurate color reproduction for industrial inspection and PCB repair. With 30fps high frame rate, it supports MJPEG/YUY2/H.264 compression formats. The H.264 compression of this USB camera reduces bandwidth usage by 50% for smooth live streaming (Windows software for H.264 capture is provided).
- Manual Zoom Lenses for USB Industrial Camera: Equipped with a 2.8-12mm CS mount varifocal lens, this industrial USB camera offers flexible manual zoom control—easily adjust focal length to switch between wide-angle views (for large-area inspections) and close-up precision (for tiny PCB components).
- 0.01Lux Low Light USB Camera Performance: As a professional industrial inspection camera, it adopts a 2MP 1/2.9 IMX323 Color CMOS sensor, enabling it to capture clear images even in 0.01Lux low light conditions. This low light USB camera is ideal for various dim environments in industrial applications.
- Plug-and-Play USB Camera with Wide Compatibility: This mini USB camera is plug-and-play, requiring no driver installation. With a 4pin to USB connector, it easily connects to PCs and is compatible with Linux, Windows, Android, and Mac OS. Suitable for various devices like kiosks, vending machines, and computers for video conference.
- Versatile Applications of 1080P USB Camera: The 1080P USB camera is widely used in industrial settings such as video surveillance system, industrial inspection, PCB repair, ATM monitoring, and robotic vision. It also works well for live streaming, video conference, dashcam, and applications needing gesture tracking, iris recognition, depth and motion detection, thanks to its 0.01Lux low-light sensitivity and low distortion lens.
At the bank or processor level, PCI Security Standards Council (PCI SSC) guidance identifies unusual transaction volume or velocity, unexpected traffic sources such as IP addresses, and unauthorized use of network tools as signs to monitor. The PCI SSC’s 2020 ATM cash-out guidance recommends continuous monitoring, immediate alerts for suspicious activity, and a practiced incident-response process.
These are warning signals, not proof of a particular attack. Operators need a defined process to assess alerts, investigate the relevant ATM or bank systems, and coordinate a response.
How ATM operators prevent compromise at the machine
Protect the enclosure and watch for access
EAST recommends securing the ATM head compartment, controlling physical access, and performing frequent visual inspections. Operators can also monitor compartment openings and loss of communication with security-relevant devices. Europol’s 2015 overview additionally names surveillance, alarms, limiting physical access, and more frequent cash-refilling cycles as possible mitigations. These controls complement one another; none guarantees that an ATM cannot be attacked.
Rank #2

- H.265/H.264 5MP POE IP Security mini ip Camera, POE(Power Over Ethernet),Resolution: 5MP@25fps;4MP@25Fps,3MP@30Fps
- POE Function,Power Over Ethernet,One Cable Transfer Data&Power
- Plug&Play,O-N-V-I-F,Motion Detect&Email Alert,FTP
- Remotely View By Free Mobile Phone App: XMEYE, Support smart mobile phone app,Tablet PC
Control software, files, and boot paths
Keeping the ATM’s software stack updated—including through a fast-track process for security updates—reduces exposure to known weaknesses. EAST also recommends file-integrity management and secure software delivery, so operators can identify unexpected changes and control how software reaches machines.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →To reduce the chance that an attacker can introduce or run unauthorized code, EAST recommends blocking unwanted USB or similar devices, using application control, and locking down the operating system by removing unnecessary services, applications, and privileges. Its guidance also includes encrypting the hard disk so files cannot be accessed while ATM software is not running; securing BIOS settings with passwords and preventing boot from external drives; and authenticating the boot process to guard against rootkits or alternate boot environments. Europol likewise identifies BIOS security, disabling external-drive boot, and operating-system hardening as mitigations.
Secure links between the ATM, its devices, and the host
ATM components and their connections need protection as well as the computer running the ATM software. EAST recommends protected communications with the card reader, cash device, and encrypting PIN pad; TLS for network traffic; message authentication for transactions; network segmentation; and a firewall limited to necessary connections. It also recommends end-to-end authentication between the host and cash modules to help mitigate attacks at the ATM PC.
Rank #3

- Samsung by Hanwha XNB-H6241A
Why ATM cash-outs are not always ATM malware
A coordinated ATM cash-out may start with a compromise of a bank or payment processor’s card-management or authorization system. An attacker may change account balances or withdrawal controls, then coordinate withdrawals at ATMs. PCI SSC and the ATM Industry Association (ATMIA) explain that these attacks usually do not exploit vulnerabilities in the ATM itself. The bank-side authorization system, rather than ATM malware, may be the key point of compromise.
That distinction affects where investigators should look. A compromised ATM PC that commands its dispenser is a machine-level attack; unusual withdrawals enabled by manipulated authorization systems point to a different attack path. A response plan should be able to investigate both without treating every cash-out as evidence of ATM infection.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallHow banks monitor systems and prepare to respond
For ATM cash-out risks and related financial systems, PCI SSC recommends monitoring the volume and velocity of transactions on underlying accounts, continuous monitoring that includes file integrity, immediate alerts on suspicious activity, and a practiced incident-response management system. It also recommends looking for unexpected traffic sources and unauthorized execution of network tools.
The same PCI SSC guidance covers broader controls for bank and processor systems. It recommends strong access controls, identifying third-party risk, employee monitoring, ongoing phishing training, multi-factor authentication, strong password management, timely patches, regular penetration testing, and regular reviews of access and privileges. Remote changes to balances or withdrawal limits should have layered authentication or approvals, and sensitive privileged roles should be strictly separated. These are financial-system security recommendations, not all ATM-firmware controls. PCI SSC also recommends following PCI DSS.
Operational readiness matters because a technical alert is useful only if responders receive it and know what to do. Banks and operators need assigned ownership, controlled access, timely updates, and response procedures that are practiced rather than merely documented.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How to assess whether ATM defenses cover the risks
Review controls against the attack paths they are meant to address. The guidance from Europol, EAST, and PCI SSC supports a layered approach; it does not provide comparative effectiveness scores for vendors or specific configurations.
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value

- 2MP FHD Auto IR Night Vision with Wide Viewing Angle: 2MP Super HD USB camera with 24pcs IR led lights,up to 90 degree wide viewing angle,capture more clearer and sharper images and video,great fit for driveway,hallways,indoor outdoor dog pet baby security monitoring etc.
- High Speed 480P@100fps Dome Camera:Usb camera with 480P 100fps high frame rate,recording more smoothly and stable,easy setup with plug and play,free driver,waterproof camera with Aluminum box housing fit for indoor and outdoor,residential areas retail store, business. Dome camera mini webcam with wide application for use in ATM machine,kiosk,vending machine,simple security system,teaching system,interactive.
- Experience Magnificent Full-HD 1080P with CMOS OV2710 Image Sensor. This USB Webcam comes with enhanced capability utilizing the 1/2.7” CMOS OV2710 image sensor. Wide 90 degree viewing angle,Android,PC Windows,Linux,Raspeberry Pi and Mac.Waterproof and durable,it could be widely applicable to indoor/outdoors.store,home,office,school,bus,taxi in snowy/rainy/sunny days.
- Dome Camera Full HD 1080P USB Webcam:Desktop Laptop Computer Web Camera,High Speed 100fps Indoor Outdoor Security Camera,Audio IR Night Vision Web Cam,Plug&Play,Dome Webcam for Windows/Android/Mac.High speed 2 megapixel dome usb camera 640X480@100fps,Max resolution:1920X1080.
- USB 2.0/Plug&Play/Free Driver usb dome camera.This usb dome camera is plug and play,free driver,Platform Compatibility:Skype,Youtube,Yahoo!@Messenger,MSN,Zoom,instant messaging applications.We want to ensure the safety of our customers,their loved ones,homes,and businesses and you’ll receive a full 1-year US Warranty and Lifetime Support provided directly from Webcamer_usb.
| Security layer | Example controls | Question to ask |
|---|---|---|
| Physical enclosure and access | Compartment access controls, inspections, opening alerts, surveillance | Would unauthorized access be prevented or promptly noticed? |
| ATM operating system, boot, and applications | Updates, file-integrity management, application control, OS lockdown, boot protection | Can unapproved code run or alter files, and how would a change be detected? |
| ATM components and communications | Protected device links, TLS, transaction message authentication, segmentation, firewall rules | Are device and host communications authenticated and limited to necessary connections? |
| Issuer and processor authorization systems | Transaction monitoring, layered approval for remote balance or limit changes, role separation | Could a compromise enable coordinated withdrawals without infecting an ATM? |
| Monitoring, alerting, and response | Continuous monitoring, immediate alerts, incident-response procedures and exercises | Who receives an alert, how quickly, and has the response been tested? |
For each control, identify whether it prevents compromise, detects it, or supports recovery. Then verify who owns the response and whether the procedure has been exercised.
Can these sources establish how common ATM malware is?
No current global or comparable ATM-malware incident count is established by the sources cited here. Europol’s IOCTA 2015 noted that there were no central records of such attacks in the background cited by its ATM logical-attack guidance. That is a historical observation, not a current prevalence figure. Card-fraud totals or old regional incident reports should not be presented as a current count of ATM malware attacks.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

