
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →An API gateway is usually a reverse proxy with API-specific routing and policy capabilities—not a mutually exclusive alternative to an API proxy. Choose a simpler reverse proxy when forwarding, load balancing, and layer-7 routing meet your needs; choose an API gateway when you need a managed place to enforce and govern API policies. The right choice depends on the features and operational model of the specific product, not its label.
What is the difference between an API proxy and an API gateway?
A reverse proxy accepts requests from clients and forwards them to upstream services. An API gateway commonly occupies that same position at an API boundary, routing client requests to the appropriate services while adding capabilities for managing APIs. Microsoft describes an API gateway as a reverse proxy in its Azure Architecture Center guidance; Kong also describes Kong Gateway as a reverse proxy used to manage, configure, and route API requests in its gateway documentation.

The terms therefore overlap. A proxy is not necessarily limited to basic forwarding, and a gateway is not guaranteed to include every API-management feature out of the box. For example, Microsoft notes that reverse proxies such as NGINX and HAProxy can provide load balancing, SSL termination, and layer-7 routing. Gateway capabilities vary too: some require configuration, extensions, or companion services.
What can an API gateway add?
Depending on the product and how it is configured, an API gateway can centralize functions that otherwise might be implemented across services or in other infrastructure:
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall

- The latest SonicWall TZ470W series, are the first desktop form factor nextgeneration firewalls (NGFW) with 10 or 5 Gigabit Ethernet interfaces. The series consist of a wide range of products to suit a variety of use cases.
- Reduce complexity and get the business running without relying on IT personnel with easy onboarding using SonicExpress App and Zero-Touch Deployment, and easy management through a single pane of glass.
- Drive business growth by investing in next-gen appliances with multi-gigabit and advanced security features, to future-proof against the changing network and security landscape.
- SonicWall 24x7 support provides chat, email, web, and telephone support for technical assistance | Dynamic Support is designed for customers who need continued protection through ongoing firmware updates and advanced technical support
- Hardware: Operating system: SonicOS 7.0 | Interfaces: 8x1GbE, 2x10GbE, 2 USB 3.0, 1 Console | Management: Network Security Manager, CLI, SSH, Web UI, GMS, REST APIs | VLAN interfaces: 128 | Access points supported (maximum): 32
- API-aware routing: Route requests through a client-facing endpoint to the appropriate backend.
- Authentication and authorization: Apply identity checks or connect to identity systems. AWS, for example, lists IAM policies, Lambda authorizers, and Cognito user pools among Amazon API Gateway authentication mechanisms in its service documentation.
- Quotas and rate limiting: Apply policies that control request volume. Apigee documents quota checks and rate-limiting policies, while Kong documents rate-limiting plugins.
- Request and response mediation: Transform or otherwise mediate messages between clients and services; Apigee documents transformation and mediation policies.
- API operations: Depending on the service, manage monitoring, traffic, or API versions. AWS lists these among Amazon API Gateway responsibilities.
- TLS controls: Terminate TLS or support mutual TLS when the selected product and configuration provide it.
These are possibilities, not a universal gateway checklist. A reverse proxy may already meet some requirements, and a gateway may need additional configuration or surrounding services to meet others. Check the product documentation for the precise controls and protocols you intend to use.
When should you use a reverse proxy?
Use a reverse proxy when your main requirement is to accept and forward traffic, direct requests at layer 7, or provide load balancing and TLS handling—and the proxy you select covers your security and operational requirements. This can avoid adopting API-management features and governance processes your team does not need.
Confirm the proxy supports the actual workload and deployment model. If you later need centralized identity policies, client-specific quotas, transformations, or API lifecycle controls, you can evaluate whether to extend the proxy, add another component, or move those responsibilities to a gateway.
When do you need an API gateway?
Consider a gateway when several APIs or teams need a shared place to apply API-focused policies or provide a managed client-facing layer. It may be a good fit when requirements include authentication and authorization, throttling by client, request or response transformation, monitoring, or API version management.
Do not assume a gateway replaces every networking component. Microsoft notes that Azure API Management does not perform load balancing, so a load balancer or reverse proxy may be needed alongside it. Its gateway guidance also recommends checking required capabilities, considering built-in platform offerings where they meet security and control needs, and accounting for the governance work of custom solutions.
How to choose between an API proxy and an API gateway
Write down the requirements before comparing product names. Assess these areas against the implementation you would actually deploy:
Rank #3
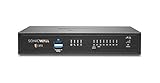
- The latest SonicWall TZ370 series, are the first desktop form factor nextgeneration firewalls (NGFW) with 10 or 5 Gigabit Ethernet interfaces. The series consist of a wide range of products to suit a variety of use cases.
- Reduce complexity and get the business running without relying on IT personnel with easy onboarding using SonicExpress App and Zero-Touch Deployment, and easy management through a single pane of glass
- Drive business growth by investing in next-gen appliances with multi-gigabit and advanced security features, to future-proof against the changing network and security landscape
- SonicWall Advanced Gateway Security Suite keeps your network safe from zero-day attacks, viruses, intrusions, botnets, spyware, Trojans, worms and other malicious attacks. Examine suspicious files at the gateway in a cloud-based multi-layered sandbox for inspection to keep your network safe from unknown threats. As soon as new threats are identified and often before software vendors can patch their software, SonicWall firewalls and Cloud AV database are automatically updated with signatures.
- Hardware: Operating system: SonicOS 7.0 | Interfaces: 8x1GbE, 2 USB 3.0, 1 Console | Management: Network Security Manager, CLI, SSH, Web UI, GMS, REST APIs | VLAN Interfaces: 128 | Access points supported (maximum): 16
- Policies: Identify required identity integration, authorization, quotas, transformations, logging, and monitoring. Confirm which are built in, which need configuration or extensions, and which require another service.
- Protocols and routing: Check support for the protocols and traffic patterns your services use, such as HTTP, REST, WebSocket, or gRPC. Product support varies; do not infer it from the terms “proxy” or “gateway.”
- Deployment model: Decide whether a managed cloud service, self-managed proxy or gateway, or service-mesh ingress best fits your environment.
- Operational ownership: Establish who handles configuration, upgrades, policy governance, availability, and incident response. Centralized controls can simplify policy enforcement but also create a shared operational dependency.
- Platform fit: Check integration with your cloud platform, Kubernetes setup, or service-mesh controls. Avoid duplicating controls without a clear reason.
- Cost and performance: Compare the specific offerings under your workload and operating model. The category names alone do not establish which option will cost less or add less latency.
If the required controls fit a simpler proxy, start there. If API-specific policies or management are requirements, assess gateways that meet them and include any companion components needed. For either option, verify current capabilities and limits with the vendor before committing.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How do the product examples differ?
These examples illustrate how vendors describe particular products; they do not define every proxy or gateway.
| Product | What the cited documentation says | How to interpret it |
|---|---|---|
| Amazon API Gateway | AWS describes the service as a way to create, publish, maintain, monitor, and secure REST, HTTP, and WebSocket APIs. AWS says HTTP APIs suit API proxy functionality, while REST APIs are for cases needing API management features in a single solution. See AWS service documentation and the Amazon API Gateway product page. | This is AWS-specific product guidance, not a universal distinction between HTTP APIs and REST APIs at other providers. |
| Google Cloud Apigee | Google Cloud documents API proxies with policies for security, quota checks, access control, rate limiting, transformation, and mediation. See Understanding APIs and API proxies. | The example shows that a product called an API proxy can include policy features commonly associated with gateways. |
| Kong Gateway | Kong describes Kong Gateway as a reverse proxy and documents plugins that extend gateway behavior, including authentication and rate limiting. See Kong Gateway documentation. | Its description illustrates the overlap between reverse proxying and API gateway functions. |
What should you know about gateway throttling?
Throttling is not necessarily a hard cap. AWS says Amazon API Gateway throttling targets are best effort: configured request-rate and burst limits may be exceeded, and requests may receive HTTP 429 responses when limits are exceeded. If you use this service, design client retry behavior for throttling responses and verify the details for your API type in AWS’s HTTP API throttling documentation. Other gateways may use different algorithms and guarantees.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

