
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Authentication proves which credential is making a screenshot-service request; authorization determines which resources and actions that credential can access. Those are separate controls. A capture API might accept a key that can render a URL, while an administrative role may govern identities, keys, products, or usage. Before issuing credentials, check the exact scope and action set the provider documents, then grant only what the integration needs.
Separate screenshot capture from API management
A screenshot service usually exposes an operational API: send a page URL and capture options, receive an image or PDF. Its management surface, when provided, governs administrative resources such as keys, roles, quotas, products, or usage. These surfaces are related but not interchangeable. The available vendor documentation does not establish one standard management API model for screenshot services.
For example, Screenshot API documents GET and POST capture endpoints and a batch POST endpoint. Its request options include output format, viewport size, full-page capture, delays, and cache behavior, and its reference describes error codes. Those are details of that provider’s API contract, not universal conventions. Screenshot API reference
When assessing any provider, ask two questions independently: what can this credential do at the capture endpoint, and what can its principal administer? Do not infer administrative access from the fact that a key can take screenshots—or assume that a screenshot key has narrowly limited capture permissions.
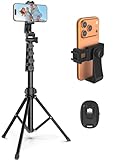
#1 Best Overall

- 62" Phone Tripod & Selfie Stick Combo: Extendable phone tripod for iPhone and Android, combining a tripod stand and selfie stick in one lightweight design for selfies, photos, videos, vlogging, live streaming, and family gatherings.
- Adjustable Height & 360° Rotation: The tripod extends up to 62 inches to support standing shots, group photos, video calls, and content creation. The 360° rotating phone holder allows vertical or horizontal shooting.
- Stable Phone Holder for Daily Recording: Designed for hands-free video recording, online meetings, tutorials, livestreams, and social content. The phone holder keeps your device positioned securely for clear, steady shots.
- Wide Compatibility with Phones and Cameras: Fits most smartphones from 2.8" to 5.7" wide and includes a universal 1/4" screw mount for compatible cameras, action cameras, webcams, and camcorders.
- Wireless Remote & Complete Kit: Includes 1 phone tripod/selfie stick, 1 universal phone holder, 1 adapter, and 1 wireless remote shutter. Backed by 12-month after-sales support for everyday shooting needs.
Authentication identifies the caller; scope limits authority
An API key or bearer token authenticates a request. A scope, role, or permission determines the resources and operations it authorizes. A credential can therefore be valid but lack permission for a requested operation; conversely, a broadly authorized credential can be a security risk even if its calls are authenticated correctly.
Providers express scope in different ways. ScreenshotOne says its API keys are scoped to an organization. Cloudflare’s URL Scanner screenshot operation accepts API tokens with URL Scanner Read or URL Scanner Write permissions. Azure API Management uses service and workspace roles, and supports custom roles with finer-grained scope, including an individual API. These labels refer to different products and authorization models; an organization-scoped key, a resource role, and an operation permission are not directly equivalent. ScreenshotOne API keys · Cloudflare URL Scanner screenshot operation · Azure API Management roles
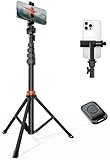
Rank #2

- 100% LIFETIME PROTECTION: Enjoy reliable performance with lifetime coverage, guaranteeing your tripod is always protected against any defects or issues.
- Ultimate Materials & Engineerin: EUCOS's phone tripod utilizes modified Nylon PA6/6 for all-weather durability. The engineered polymer delivers exceptional crush/shear resistance and toughness, achieving optimal rigidity-flexibility balance.
- Rapid Extension Tripod for Phone: Glide the rod in a single, fluid motion to convert it from a compact tripod into a full 62" selfie stick. Achieve instant elevation for dynamic filming.
- Studio-Grade Phone Rig: Safely harness phones from 2.2" to 3.6" wide with pro-level clamping and effortless framing. Built-in cold shoe expands your creative options with lights and mics.
- Hands-Free Control: The Wireless remote enables instant pairing with smartphone and remote capture from up to 33ft/10m. Ensures rock-solid stability for blur-free photography and Start/Stop video recordings effortlessly—all without device contact.
Compare documented permission models without assuming parity
| Provider and surface | Documented credential or scope | What to take from it |
| ScreenshotNeo | A website screenshot API and MCP server. The stated product information does not specify granular management roles or credential scopes. | Do not assume unlisted role controls. Review the current documentation and dashboard before choosing an integration credential. |
| ScreenshotOne API | API keys scoped to an organization. | Organization scope is the documented boundary; verify which actions the issued key permits. |
| Cloudflare URL Scanner screenshot operation | API tokens; URL Scanner Read or URL Scanner Write permissions are listed for this operation. | These permissions concern Cloudflare’s URL Scanner operation, not screenshot rendering at other vendors. |
| Azure API Management | Built-in Contributor, Reader, and Operator service roles; workspace roles; custom roles. Assignments can be scoped at subscription, resource group, or individual API Management instance level, with finer-grained custom-role scope including an individual API. | Scope role assignments to the smallest appropriate resource and assess the role’s actual actions, not just its name. |
Sources: ScreenshotOne, Cloudflare, and Microsoft Learn. The table compares what these documents describe; it does not imply that their scopes, actions, or credential lifecycles are equivalent.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteChoose the narrowest useful credential route
- Define the integration’s job. Record whether it only captures pages, submits batches, reads status or usage, or changes administrative configuration. Avoid asking for management access if the integration only needs the capture endpoint.
- Identify the protected resource. Determine whether the provider scopes access to an organization, service, workspace, API, or named operation. Where multiple levels are available, select the smallest that still supports the workflow.
- Match actions to the task. Separate read, write, invoke, and administrative actions where the provider exposes them. Do not pick a broader role merely because its name is familiar; read the documented action set.
- Check the exact credential’s behavior. Confirm where the key is created, which requests it authorizes, how it is revoked or replaced, and whether it can be used from a public client. The evidence here does not establish that every provider supports per-user keys, OAuth consent, rotation, audit logs, or host restrictions.
- Store and transmit it safely. Keep credentials out of source code, browser JavaScript, public pages, and logs. Prefer the provider’s recommended header or other private transport, and use a secrets manager or protected environment variable for server-side applications.
- Test the intended boundary. Verify that the integration succeeds for its required operation and fails for actions it should not perform. Recheck after changing roles, keys, or resource scope.
Protect credentials used to render target websites
Some integrations pass credentials for the target site being captured—such as cookies, headers, or basic-auth data. These are not the same as the credential authorizing a call to the screenshot provider. Treat them as separate secrets with separate audiences and access policies.
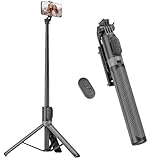
Rank #3
- 【Sturdy and Stable】: Made of premium aluminum alloy and stainless steel, Liphisy phone tripod with remote keeps your device stay securely in place for still shots and video recording.
- 【Multi-angle Shot】: With a max height of 64”, this tripod stand with a 210-degree rotation head and 360-degree rotation holder allows you to capture shots from any angle, catering to different photography needs.
- 【Wireless Remote Included】: Package includes a wireless remote that connects to your cell phone easily, making it a breeze to snap photos or video recordings.
- 【Height Adjustable】: The height of this cell phone tripod with remote can be adjusted from 17” to 64” and the easy lock mechanism makes it really easy to set up. It gives you an excellent vantage point for capturing photos and videos.
- 【Wide Application】: Compatable with different phone and camera, this tripod is great for photography and video recording, perfect for travel and home use.
Screenshot-api.net documents cookies, headers, and basic authentication scoped to the target host. It recommends POST when target credentials are present because query strings can be written to access logs. It also cautions that a page available only in a user’s own browser session is a different use case. These are that service’s documented behaviors, not guarantees about all screenshot APIs. Screenshot API documentation
Screenshot API documents bearer authorization and an X-API-Key header, and also permits a query parameter as a convenience; its documentation recommends headers. ScreenshotOne allows keys in a query string, POST JSON body, or header, and advises treating a key like a password, storing it in an environment variable or secrets manager, and not exposing it on public pages. Screenshot API reference · ScreenshotOne API keys
Rank #4
- Steel-Reinforced Steadiness:Featuring a tri-functional design, this 66-inch aluminum phone tripod stand integrates a steady base, telescoping arm, and multi-angle phone holder - an all-in-one solution for content creation, from overhead product shots to full-body portraits
- Intuitive Angle Control: Precision-engineered locking flanges enable instant switching between portrait, landscape, and 45° angled shots. Universally compatible with mobile phones ranging from 2.2" to 3.6" widths without slippage, making it a versatile addition to your Tripod & Monopod Accessories
- True Mobile Rig Flexibility:Engineered for steady everyday use rigidity, this adaptable cell phone tripod mount ensures rock-solid grip on smartphones. Its built-in Cold-Shoe slot enables seamless attachment of vlogging accessories like LED panels or mics
- Vibration-Free Content Creation: Integrated wireless Bluetooth remote (10m range) eliminates touchscreen interference. Perfect for capturing crisp stills or initiating smooth video recordings hands-free – an essential tool among modern Tripod & Monopod Accessories for solo creators
- In the Box: 66" Metal iphone tripod stand, 360° rotatable phone mount, 10m range phone camera remote, Includes 36 months of technical support and product coverage
- Do not put provider keys or target-site secrets in client-side code that visitors can inspect.
- Avoid query-string secrets when a header or POST body is available: URLs may be recorded in logs or other systems.
- Restrict target credentials to the intended host and purpose where the provider supports such restrictions.
- If a key is exposed, follow the provider’s revocation or replacement process. ScreenshotOne specifically recommends replacing an exposed key.
Azure API Management: write access can expose credentials
Azure API Management documents a caveat that matters when protecting credential-bearing entities: removing the listSecrets permission alone does not necessarily hide credentials from a principal that already has write access to the parent entity. A write-capable principal may update the credential and receive the full updated entity in the response. Microsoft advises designing protection around write access to those entities, rather than relying only on withholding list-secrets access. Microsoft Learn: Azure API Management role-based access control
Apply that lesson when reviewing any administrative platform: inspect what a write operation returns and what entities the role can modify. A permission named “read secrets” is not the only possible path to secret exposure if write access returns credential-bearing data.
Best Value
- [Versatile Design] RISEOFLE 71'' Phone Tripod and Selfie Stick combo is the perfect accessory for all your cell phone photography needs.The high-quality aluminum alloy telescopic pole allows you to extend effortlessly and smoothly, and turns into a tripod with just one pull. Its sturdy yet lightweight design provides stability and reliability, ensuring that your phone or camera stays safe during use. Ideal for Selfies/Live/Video Recording/Travel
- [Extra Tall 71" Adjustable Phone Tripod] This selfie stick tripod features a 7-section adjustable aluminum telescoping pole that adjusts from 12.2 in (31 cm) to 70.86 in (180 cm). Provides exceptional flexibility for shooting a variety of shots. Whether you're taking a selfie, a group photo or shooting a video, the adjustable height ensures you get the best angle every time.
- [Compact & Portable Design] The RISEOFLE phone tripod stand With a folded length of only 31cm (12.2 in) and a weight of 264g (0.58 lb), extremely portable and easy to store, it can be effortlessly placed into your backpack or carry-on luggage, making it the perfect companion for your travels. Wherever you go, it allows you to capture amazing footage with ease.
- [360° Rotation & Wide Compatibility] Featuring a 360° rotating phone holder, this selfie stick tripod allows you to easily switch between portrait and landscape modes for the best viewing angle. The universal holder fits smartphones with widths of 2.6''-3.6'' (4''-7'' screen size) and is compatible with most cameras, action cams, and webcams via the 1/4” screw mount (Note: the remote control function only applies to cell phones, the camera cannot use the remote control function).
- [Perfect for Content Creation] Ideal for selfies, vlogging, and social media content creation, the RISEOFLE Tripod comes with a wireless remote control for hassle-free shooting. Whether you're on Instagram, YouTube, TikTok, or Twitter, this phone stand for filming helps you capture professional-quality photos and videos with ease.
ScreenshotNeo alternative for capture integrations
If the requirement is to capture web pages rather than administer another screenshot platform, ScreenshotNeo is a website screenshot API and MCP server from Yorker Media. Its product information describes one GET request that returns a PNG, JPEG, WebP, or PDF. This capture API is distinct from a management-role system; consult the current docs for credential handling and available controls.
Example request (replace the URL with the page to capture and keep your API key server-side):
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpSee the ScreenshotNeo API documentation for request options and integration details. ScreenshotNeo also provides an MCP server with take_screenshot, get_page_info, and capture_pdf tools for Claude, Cursor, and other MCP clients. Its documented cleanup can accept cookie or consent banners and remove more than 60 known consent platforms, newsletter popups, and chat widgets before capture; each step can be turned off. The service says bot checks/CAPTCHAs, blank pages, timeouts, failed loads, and cache hits are not billed, and responses identify page verdict and billing through headers.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →ScreenshotNeo’s free plan includes 1,000 shots per month with no card; paid plans start at $5 for 3,000 shots. Sign up for 1,000 free screenshots a month, with no card.
Quick Recap
Troubleshooting access and credential failures
- Authentication failure: Check that the key or token is present, current, and sent using the provider’s supported method. Confirm whether the provider expects a bearer token, a named header, or another format.
- Authenticated but forbidden: The credential may be valid while its scope or action set excludes the operation. Check the exact required permission for that endpoint, then request the smallest additional grant needed.
- Capture works but administration fails: A capture key is not necessarily an administrative credential. Use the documented management role or API, if the provider offers one, rather than assuming capture access implies account-management authority.
- Target page returns an authentication wall: Provider authentication and target-site authentication are separate. Check whether the service supports target cookies, headers, or basic auth, and follow its guidance for sending sensitive values.
- Secret appears in logs or a URL: Remove query-string credentials where possible, switch to a documented header or POST pattern, inspect relevant logs, and revoke or replace an exposed key according to the provider’s process.
- Unexpected secret visibility in Azure API Management: Review write access to the parent credential-bearing entity; removing
listSecretsalone may not prevent a write-capable principal from receiving updated entity data.
Operational checks before deployment
- Document the owner, purpose, scope, required actions, and storage location for each credential.
- Keep capture credentials on a trusted server or worker rather than in a public browser application.
- Separate provider API credentials from target-site cookies and authorization headers.
- Check provider limits, batch behavior, cache rules, and failure responses in the current API reference; these vary by service.
- Establish a revocation and replacement procedure before launch. The cited documentation does not establish a common rotation or audit-log capability across providers.
- Review permissions when an integration’s purpose changes, and remove access that is no longer required.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

