
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →The best digital forensics tools and techniques in 2026 depend on the evidence source: Autopsy suits budget computer examinations, Cellebrite targets supported mobile devices, Volatility 3 analyzes RAM, and Wireshark examines packets. No single product is best for every case; defensible investigations combine acquisition, specialized analysis, validation, and independent corroboration.
A disk imager is not a mobile-extraction platform, a packet analyzer is not an endpoint-investigation suite, and an automated report is not proof that a person performed an action. The right choice depends on the device state, operating system, evidence type, budget, legal authority, and required reporting standard.
| # | Preview | Product | Price | |
|---|---|---|---|---|
| 1 |
|
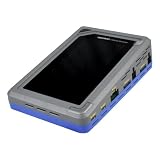
OpenText Forensic (Tableau) TD4 Forensic Duplicator Kit | $2,599.00 | Buy on Amazon |
| 2 |

|
OpenText Forensic (Tableau) TX2 Forensic Imager | $5,999.00 | Buy on Amazon |
| 3 |

|
Tableau TD2u Forensic Duplicator Kit | $398.00 | Buy on Amazon |
| 4 |

|
SiForce Tableau Forensic Bundle (FAU External T356789iu Bridge, FAU Kit) | $2,099.99 | Buy on Amazon |
This list combines nine products and techniques because professional digital forensics requires both. Commercial platforms can accelerate processing and broaden parser coverage, while open-source tools often provide transparency, low-cost training, and useful independent checks.
Key takeaways
- There is no universally best digital-forensics product in 2026; the strongest workflow matches tools to computers, mobile devices, memory, networks, cloud sources, or other evidence.
- Work from a verified forensic image or preserved copy, use write protection where appropriate, calculate hashes, and document the acquisition before analysis.
- Autopsy, The Sleuth Kit, Volatility 3, Wireshark, Plaso, Timesketch, and specialized Windows parsers can form a capable low-cost learning and analysis stack.
- Mobile extraction is highly dependent on device model, operating-system version, patch level, lock state, encryption, and the licensed acquisition method.
- Commercial coverage claims, “full extraction,” AI classifications, and “court-proven” marketing statements require case-specific validation rather than automatic acceptance.
How were these digital forensics tools and techniques selected?
The shortlist prioritizes evidence-source coverage, acquisition depth, repeatability, reporting, current support, validation opportunities, cost, learning requirements, and the ability to corroborate important findings with another tool or raw artifact.
#1 Best Overall
- TD4 Forensic Duplicator Kit includes: TD4 Forensic Duplicator, TP6 Power Supply, US Power Cord, (x3) TC4-8-R4 Unified SATA/SAS Signal and Power Cable (Molex), TC-PCIE4-8 PCIe Adapter Cable, 8" (Gen3 x4), TA-PCIE-PCIE4 Adapter (adapts between PCIe Gen2 and Gen3+), (x2) TCA-USB3-AC USB 3.0-A to USB 3.1-C Cable Adapter, Velcro Cable Ties (TPKG-VCT-5), Microfiber Cloth (TPKG-CLOTH), Quick Reference Guide
- Image data anywhere—native support for SATA, SAS,PCIe, and USB-C.
- Intuitive, seamless workflows—custom-built UI on color, touchscreen interface.
- Fast, efficient targeted acquisitions with local imaging capability.
- Wipe, format, and encrypt options for destination media.
NIST’s Computer Forensics Tools & Techniques Catalog categorizes tools by functions such as disk imaging, deleted-file recovery, memory analysis, mobile acquisition, cloud services, file carving, hash analysis, live response, browser forensics, Registry analysis, and tool validation. NIST says catalog inclusion is not testing or endorsement. The catalog page identifies an update date of June 24, 2026, but readers should still confirm current product releases and support matrices before purchasing.
NIST’s scientific-foundation review also describes important limits: investigators may not recover every item, deleted-file recovery can produce irrelevant material, and changing operating systems and applications can change the meaning of artifacts over time.
Which tool or technique fits each investigation?
| Need | Strong first choice | Lower-cost or open alternative | Main caution |
|---|---|---|---|
| Disk imaging | FTK Imager, X-Ways Imager, or a vendor acquisition tool | dd, dc3dd, Guymager |
Confirm the source, destination, write protection, hashes, and image integrity. |
| Computer forensics | Magnet AXIOM, OpenText Forensic, FTK, or X-Ways Forensics | Autopsy and The Sleuth Kit | Automated parsing still needs examiner verification. |
| Mobile acquisition | Cellebrite Inseyets UFED | Logical acquisition, backups, Oxygen, or MSAB XRY | Device and operating-system support changes rapidly. |
| Mobile analysis | Cellebrite Physical Analyzer, AXIOM, or Oxygen | Specialized parsers where available | Acquisition and analysis are separate capabilities. |
| Memory forensics | Volatility 3 | Maintained focused scripts or alternative frameworks | The capture must be compatible with the analysis workflow. |
| Network packets | Wireshark | tshark or Zeek |
Visibility depends on capture location, timing, packet loss, and encryption. |
| Windows artifacts | Eric Zimmerman tools plus a general suite | Open-source parsers and scripts | Timestamps and user attribution are easy to misinterpret. |
| Timeline correlation | Plaso, Timesketch, AXIOM, or Autopsy | Open-source timeline tooling | A timeline organizes evidence but does not prove identity or intent. |
| Validation and reporting | Tool-native reports plus independent review | Documented scripted exports | A product report cannot replace chain-of-custody records. |
1. Why is forensic imaging the first essential technique?
Forensic imaging creates a preserved working copy of a drive or removable medium before examination. FTK Imager is a widely used option, but Guymager, dc3dd, dd, X-Ways Imager, OpenText TX1 Imager, Magnet Acquire, and vendor-specific acquisition tools can also fit particular workflows.
- Isolate and photograph or otherwise document the evidence.
- Record identifiers, physical condition, date, time, examiner, and destination storage.
- Use a hardware write blocker when the evidence and acquisition method permit it.
- Acquire a raw, E01/Ex01, AFF4, or another validated forensic image format.
- Calculate and record cryptographic hashes.
- Verify the completed image and preserve the verification result.
- Perform examination against the verified copy, not the original media.
U.S. government procurement material lists FTK Imager alongside dd/dc3dd, EnCase Imager, AXIOM Acquire, and other acquisition products; the procurement document does not make every listed product universally suitable or independently validated.
Strengths: Imaging preserves a repeatable source for analysis and allows separate examiners or tools to work from the same data. Limitations: Imaging cannot repair failed hardware, defeat encryption, recover data destroyed by TRIM, or compensate for an unprotected write path. A commercial product does not make an acquisition automatically admissible; process, validation, examiner competence, documentation, and jurisdictional rules remain important.
Illustrative command only: confirm the device identifier and destination before using any imaging command. Never copy this command unchanged onto an unknown system.
sudo dc3dd if=/dev/sdX of=/evidence/case001/disk001.dd
hash=sha256 log=/evidence/case001/disk001.log
sha256sum /evidence/case001/disk001.ddDevice identifiers, permissions, filesystem support, output formats, and tool versions vary. A wrong if or of path can destroy evidence or the destination, so controlled procedures and a second-person check are appropriate.
2. Is Autopsy and The Sleuth Kit good for computer forensics?
Autopsy and The Sleuth Kit are strong no-cost starting points for disk-image analysis, education, independent examinations, and small teams. Autopsy supplies a graphical case workflow built around The Sleuth Kit and related modules.
Autopsy can support file-system examination, deleted-file review, keyword searches, hash-set filtering, browser artifacts, timelines, email and media review, file carving modules, case management, and reporting. The official installation documentation reviewed for this article describes Autopsy 4.20.0 and Windows installers plus ZIP distributions for Linux and macOS. Because that page is release-specific, confirm the current release and operating-system requirements before deployment.
Best fit: students, new examiners, budget-conscious teams, and investigators examining ordinary computer images. Advantages: accessible, free/open-source, and useful for learning how artifacts relate to filesystems and timelines. Limitations: parsing coverage, module quality, and performance vary by artifact and operating system; important findings may require manual interpretation or a second parser. Autopsy is not a substitute for comprehensive modern mobile extraction and should not be presented as a universal encryption-bypass tool.
Preserve the image, record the Autopsy and module versions, save case logs and exports, and independently inspect material findings. Free software still requires storage, training, analyst time, and a defensible process.
3. When is Magnet AXIOM the right commercial platform?
Magnet AXIOM is designed for investigations that combine computer, mobile, cloud, browser, communication, multimedia, and other sources in one review workflow. NIST’s catalog lists Magnet AXIOM across functions including cloud services, deleted-file recovery, disk imaging, file carving, hash analysis, image analysis, memory, mobile acquisition and analysis, social media, and browser forensics.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchMagnet’s official AXIOM product page explains the vendor’s integrated workflow, while the NIST catalog entries should be read as catalog information rather than independent performance testing.
Rank #2
- TX2 Forensic Imager Kit Includes: TX2 Forensic Imager, TP8 Power Supply, US Power Cord, (x4) TC4-8-R4 Unified SATA/SAS Signal and Power Cable (Molex), (x2) TC-PCIE4-8 PCIe Adapter Cable, 8", (x2) TCA-USB3-AC USB 3.0-A to USB 3.1-C Cable Adapter, Velcro Cable Ties (TPKG-VCT-5), Microfiber Cloth (TPKG-CLOTH), Quick Ref Guide
- LIGHTNING-FAST PROCESSING AND IMAGING: Powered by parallel hash verification and concurrent imaging, the TX2 is up to 3.8x faster than its predecessor. Capture and verify evidence in record time across multiple jobs.
- STREAMLINED RECONFIGURATION PROCESS: The TX2 makes it easy to pivot between tasks with a simplified reconfiguration process. Wipe, format, or encrypt all in one.
- UNLIMITED CONCURRENT OR CONSECUTIVE QUEUEING: The TX2's architecture is built for multitasking, allowing for unlimited concurrent or consecutive queueing. Stack jobs back-to-back or run several at once.
- OPTIMAL POWER ALLOCATION: The TX2 intelligently allocates power with dynamic resource assessment to maintain peak performance during heavy workloads. Its dynamic power management evaluates task demands in real time, ensuring every imaging job runs at optimal speed.
Best fit: professional labs and corporate or law-enforcement teams that value integrated processing, cross-source correlation, reporting, and vendor support. Trade-offs: commercial licensing, training, storage, processing requirements, and the risk that a polished automated result appears more certain than the underlying evidence supports.
Cloud and mobile results depend on lawful access, device state, credentials, provider returns, source availability, and current parser support. Validate consequential results against raw artifacts, another tool, or a documented manual method.
Public official list pricing was not verified. A 2026 third-party comparison estimated approximately $3,000–$15,000 annually depending on licensing and scope, but that estimate is not a quotation; request pricing and a demonstration using representative evidence.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →4. What can Cellebrite Inseyets UFED and Physical Analyzer do?
Cellebrite Inseyets UFED is primarily a lawful mobile-device acquisition platform, while Physical Analyzer processes and interprets extractions. The distinction matters: acquiring a supported phone and analyzing an extraction are related but separate capabilities.
Cellebrite describes UFED as supporting logical, file-system, and physical extraction workflows where supported, including iOS and Android collection and after-first-unlock workflows. The vendor’s UFED page makes those claims, but a current device-support matrix is the authority for a particular model, operating-system version, patch level, lock state, and licensed method.
Cellebrite Physical Analyzer is intended to ingest UFED and other supported extractions and provides application decoding, selective decoding, media categorization, and reporting.
Best fit: lawfully examining smartphones, tablets, SIM cards, removable media, and related mobile sources in a professional lab. Critical limitations: lock state, recent unlock state, encryption, security configuration, battery, operating-system updates, unsupported applications, and remote-wipe risk can materially change the result. “Full extraction” does not guarantee recovery of every user-created or deleted artifact. Cloud data may require separate legal authority and provider cooperation.
Free tools Windows power users keep installed
One-click scans. No signup required.
MSAB XRY, Oxygen Forensic Detective, Magnet mobile products, and supported logical acquisition from backups or consent-based exports are alternatives. Public official list pricing was not verified; a 2026 third-party estimate placed UFED at approximately $15,000–$20,000 annually, but actual costs vary by region, modules, support, and contract.
5. How does Volatility 3 support memory forensics?
Volatility 3 analyzes a preserved RAM capture for volatile evidence such as processes, injected code, network connections, loaded modules, handles, credentials, and malware indicators. Volatility 3 is distinct from older Volatility 2 workflows, and current plugin, symbol, and operating-system requirements should be checked in the official Volatility 3 documentation.
- Decide whether live memory acquisition is justified and authorized.
- Capture RAM with a validated tool appropriate to the operating system.
- Document system state, acquisition conditions, time, and operator.
- Preserve and hash the memory image.
- Confirm the symbol and operating-system requirements for analysis.
- Examine processes, network state, modules, credentials, and malware-related indicators.
- Correlate memory findings with disk, event logs, identity records, and network data.
Live acquisition changes system state and may create artifacts, but shutting down a running system can destroy decrypted keys, active sessions, RAM-resident malware, and network context. A capture can also be incomplete or incompatible; anti-forensics, paging, virtualization, encryption, and kernel protections can limit conclusions.
Volatility 3 is a strong specialist and learning tool, not a point-and-click replacement for a complete case platform. Record the framework version, symbols, plugins, commands, errors, and interpretation.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
6. Why use Wireshark for network forensics?
Wireshark provides packet-level inspection for reconstructing protocol activity, investigating suspicious connections, and testing network-based hypotheses. Preserve the original PCAP or PCAPNG file, hash it, and record the capture point, time zone, clock accuracy, filters, and known collection gaps.
The Wireshark User’s Guide and official project site are the appropriate references for current display filters and behavior. Useful examination steps include filtering by host, port, protocol, DNS name, TLS metadata, or time range; following TCP or application streams; and exporting derived evidence while retaining the original capture.
Rank #3
- Natively images USB 3.0, SATA, and IDE/PATA storage devices.
- Acquisitions of USB 3.0, SATA, and IDE/PATA devices can be directed to either USB 3.0 or SATA output devices. No special adapters or additional costs for USB 3.0 support are required.
- TD2u’s color LCD user interface provides crisp, easy-to-view operational and device status information. The color UI presents an at-a-glance visual of devices connected and ready for imaging.
- 1-Year Manufacturer Warranty
tshark -r evidence.pcapng -Y 'dns or http or tls'The command is illustrative and reads the capture without replacing the original. A capture only shows what was visible at its collection point and time. Missing packets, asymmetric routing, NAT, clock drift, sampling, and encryption can make conclusions incomplete. Encrypted traffic may expose metadata without exposing content. Correlate packets with endpoint, DNS, firewall, proxy, identity, and cloud logs.
Wireshark is not a complete endpoint-forensics, enterprise case-management, or evidence-collection platform. Zeek can complement packet inspection with network telemetry, while tshark is useful for scripted extraction from captures.
7. Which tools are best for Windows artifact analysis?
Specialized Windows parsers, including Eric Zimmerman’s tools, are useful for examining Registry hives, event logs, Amcache, Shimcache, Prefetch, ShellBags, LNK files, Jump Lists, browsers, and other execution traces. The official project page is the source for current tools and distribution details.
Use specialized parsers to expose underlying fields and provide an independent check on a general-purpose suite. Preserve original artifacts, export parsed results separately, and record the parser name, version, command line, time zone, and output format.
Windows artifact interpretation has recurring failure modes. Timestamps can represent UTC, local time, daylight-saving transitions, or application-specific values. Retention and overwrite behavior varies by artifact. Parser support can lag behind new Windows builds. A single Prefetch, Registry value, or browser record rarely proves who performed an action.
Compare multiple artifacts and distinguish direct observations from inferences. The absence of an artifact is inconclusive unless collection conditions, retention behavior, and system state support a stronger conclusion.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errors8. How do timeline analysis and cross-source correlation work?
Timeline analysis organizes events from filesystems, Registry data, event logs, browsers, email, memory, networks, and cloud sources so investigators can test what happened and when. Timeline creation is a technique rather than a single product; Plaso, Timesketch, Autopsy, AXIOM, OpenText Forensic, custom scripts, and specialized parsers can contribute.
- Normalize timestamps and document the selected time zone.
- Collect events from all relevant sources without discarding collection failures.
- Build a super timeline.
- Group events by user, device, process, IP address, account, and artifact source.
- Separate direct observations from interpretations and hypotheses.
- Identify time gaps, clock drift, conflicting records, and duplicate synchronization events.
- Corroborate material conclusions with at least two independent sources where possible.
Plaso documentation covers timeline generation, and the Timesketch project supports timeline exploration and collaboration. NIST SP 800-86, published in August 2006, discusses integrating computer and network forensics into incident response while noting that it is not an all-inclusive procedure or legal advice.
A timeline can show that an account, process, or device generated an event. A timeline alone does not prove that a particular person performed the action, establish intent, or prove an exact deletion time.
9. Why are hashing, validation, and reporting as important as the software?
Evidence validation and reporting make findings reproducible, reviewable, and defensible; the best software cannot compensate for an undocumented or unrepeatable process.
Recommended Free Tools
- Use write blockers where appropriate and preserve original evidence read-only.
- Hash original media, forensic images, exports, and important evidence files.
- Record tools, versions, configuration, commands, processing dates, time zones, and errors.
- Maintain chain-of-custody records and contemporaneous examiner notes.
- Preserve negative findings and collection failures instead of reporting only successful results.
- Use peer review or a second tool for material conclusions.
- Export reports in a format that supports later review and preserve the underlying data.
- Label automated classifications, examiner interpretations, and unresolved hypotheses separately.
NIST’s catalog distinguishes the existence of a tool from independent testing. NIST’s scientific-foundation review emphasizes limitations and changing software environments. “Forensically sound” should therefore describe the acquisition and validation process, not merely a product label.
Automated image, message, and artifact classification can reduce review time but can produce false positives and false negatives. Record the tool or model version, configuration, thresholds, and human-review process whenever automated classification affects a consequential conclusion.
How should a toolchain change by evidence source?
| Evidence source | Acquisition or preservation priority | Analysis combination | Special risk |
|---|---|---|---|
| HDD, SSD, NVMe, USB | Controlled image, write protection, identifiers, hashes | Autopsy, AXIOM, FTK, OpenText Forensic, X-Ways, specialized parsers | TRIM, wear leveling, encryption, hardware failure |
| Live Windows, macOS, or Linux system | Document state; consider authorized RAM and live-response capture | Volatility 3, endpoint logs, disk image, artifact parsers | Collection changes the system and shutdown destroys volatile evidence |
| iOS or Android device | Document lock and unlock state, connectivity, battery, and remote-wipe risk | UFED/Inseyets, Physical Analyzer, XRY, Oxygen, AXIOM | Device, patch, encryption, and application support changes rapidly |
| Cloud storage or SaaS | Preserve provider exports, administrative logs, and legal records | Cloud-capable suites, provider tools, endpoint correlation | Retention, jurisdiction, provider metadata, and synchronization gaps |
| RAM | Validated live capture and hash-preserved image | Volatility 3 plus endpoint and network correlation | Incomplete capture, symbols, paging, anti-forensics |
| PCAP or PCAPNG | Retain original capture, hash, source, clock, and capture point | Wireshark, tshark, Zeek, endpoint and DNS logs |
Encryption, packet loss, NAT, asymmetric routing, sampling |
| Email, browser, vehicle, drone, IoT, or GPS data | Preserve source export and metadata | Artifact-specific parsers plus a general case platform | Format changes, provider conventions, incomplete exports |
NIST’s taxonomy includes many of these categories, including cloud, mobile, memory, vehicle, drone, browser, Wi-Fi, and Registry forensics. Catalog coverage does not guarantee that a particular tool supports a particular device, file, application, or version.
Rank #4
- Included Tableau Cables/Adapters: TC4-8-R2 Unified SATA/SAS Signal & Power Cable, TC2-8-R2 Molex to 3M Drive Power Cable, TC6-8 IDE Data Cable, TC-USB3 USB 3.0 A to B Cable, TC7-9-9 9-pin to 9-pin Firewire Cable, TDA3-3 mSATA/M.2 SATA SSD Adapter, TKA-PCIE-5PC (Gen3 x4) 5 Piece PCIe Adapter Kit
- Additional Accessories: SiForce USB 3.0 Media Card Reader, USB C Female to USB A Male Adapter, USB A Female to USB C Male Adapter, Power Supply and Power Cable, SiForce Rugged Case with Foam Protection
What is a practical beginner digital-forensics stack?
A practical low-cost learning stack combines Autopsy/The Sleuth Kit, Volatility 3, Wireshark, Plaso, Timesketch, and specialized Windows-artifact tools. Use legally obtained test images, sample PCAPs, and controlled systems rather than real evidence for experimentation.
- Disk: Autopsy and The Sleuth Kit for filesystem, browser, keyword, hash, and timeline work.
- Memory: Volatility 3 for compatible RAM images and plugin-based investigation.
- Network: Wireshark or
tsharkfor PCAP review. - Timelines: Plaso for event extraction and Timesketch for review and collaboration.
- Windows: Eric Zimmerman tools for focused artifact parsing and independent checks.
- Process: Document every version, command, hash, time zone, result, and limitation.
The software may be free or open source, but a real lab still needs storage, acquisition hardware, training, secure evidence handling, backup, and analyst time. Open source does not automatically mean independently validated, and commercial software does not automatically mean correct.
What does a professional lab stack look like?
A professional lab normally combines controlled acquisition, computer analysis, mobile capabilities, specialist tools, evidence management, and peer review rather than relying on one license.
- Hardware write blockers and a validated acquisition tool.
- A commercial computer-forensics platform such as Magnet AXIOM, OpenText Forensic, FTK, or X-Ways Forensics, selected after testing representative evidence.
- A mobile acquisition and analysis combination, such as Cellebrite UFED/Inseyets and Physical Analyzer, MSAB XRY, Oxygen Forensic Detective, or another supported platform.
- Volatility 3 and validated memory-capture procedures.
- Wireshark, Zeek, and endpoint telemetry for network investigations.
- Specialized Windows parsers and timeline tooling for independent validation.
- Evidence-management, reporting, access-control, backup, and peer-review procedures.
Before buying, request a current device and artifact support matrix, a demonstration using representative evidence, licensing and renewal terms, update policy, training costs, sample reports, processing requirements, and documentation of independent validation. Quote-based enterprise licensing makes public price comparisons unreliable.
Which tool should you choose for common scenarios?
| Scenario | Recommended starting approach | Why |
|---|---|---|
| One seized Windows laptop | Write-blocked image, Autopsy or a commercial suite, plus Windows artifact parsers | Separates preservation from analysis and permits corroboration. |
| Encrypted corporate endpoint | Authorized live-response and memory capture when justified, followed by preserved disk acquisition | Live state may contain keys, active sessions, and decrypted volumes, but changes the system. |
| Suspected malware infection | Volatility 3, endpoint logs, disk artifacts, and network captures or telemetry | Correlates volatile processes with persistence and communications. |
| Smartphone examination | Supported mobile acquisition platform plus a separate analysis workflow | Device model, lock state, OS, and method determine available evidence. |
| Cloud-account investigation | Lawful provider or administrative export, preserved logs, and synchronized-endpoint correlation | Cloud content, metadata, identity logs, and retention are separate sources. |
| Large eDiscovery collection | Scalable commercial processing, deduplication, search, review, and documented exports | Volume, legal hold, repeatability, and review controls matter as much as parsing. |
| Network intrusion | Wireshark for packets, Zeek or telemetry for scale, and endpoint/log correlation | Packet visibility depends on capture placement and encryption. |
| Student or small-business budget | Autopsy, Volatility 3, Wireshark, Plaso/Timesketch, and Windows parsers | Provides broad learning coverage without enterprise licensing. |
How should teams score competing forensic products?
Score each candidate against the evidence and workload the organization actually handles. A product with broad marketing coverage can still be a poor choice if the required device, operating system, license module, or export format is unsupported.
- Evidence coverage: Does the product handle the organization’s real devices, filesystems, applications, cloud sources, and traffic?
- Acquisition depth: Does it acquire, analyze, or both? What happens when the device is locked or encrypted?
- Validation: Can the team inspect raw artifacts, reproduce results, and compare another parser?
- Repeatability: Are versions, configurations, logs, and exports preserved?
- Reporting: Can another examiner understand the source, processing, interpretation, and limitations?
- Scale: Does processing time, storage, automation, and concurrency fit expected volumes?
- Cost: Include licenses, renewals, modules, hardware, training, support, storage, and analyst labor.
- Legal and policy fit: Are collection methods authorized and appropriate to the jurisdiction and investigation?
- Update cadence: Can the vendor or project keep up with operating-system, application, and device changes?
- Corroboration: Can findings be checked using raw data, an independent tool, or a second examiner?
What can digital-forensics tools not prove?
Digital-forensics tools report artifacts and interpretations; they do not automatically prove a person’s identity, intent, knowledge, or complete absence from an evidence source.
- An account name or profile does not by itself prove which person used the device.
- A file timestamp does not necessarily establish the exact time a person created, viewed, or deleted a file.
- A deleted-file recovery result may be incomplete, reconstructed, or mixed with extraneous data.
- No recovered artifact does not prove that an event never happened.
- A cloud export may omit content or metadata because of provider retention, export design, permissions, or legal limitations.
- A mobile “full extraction” remains limited by the supported device, OS, lock state, method, and parser.
- An AI or automated classification can be wrong and requires human review.
- Different tools may disagree because they use different parser logic, time-zone handling, application-version support, or interpretations of partial records.
When tools disagree, preserve the original artifact, compare raw data with each parser’s output, document the disagreement, and state the uncertainty rather than selecting the more convenient result.
Bottom line: what are the best digital forensics tools and techniques in 2026?
Choose by evidence source, not by a universal ranking. Use controlled imaging and hashing for storage media; Autopsy or a commercial suite for computer evidence; Cellebrite, MSAB, Oxygen, or another supported platform for mobile work; Volatility 3 for RAM; Wireshark and Zeek for network evidence; specialist Windows parsers for artifact validation; and Plaso or Timesketch for timelines.
The defensible principle is simple: match the toolchain to the evidence, preserve the original, validate the process, document limitations, and corroborate important findings.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Frequently Asked Questions
Is there one best digital forensics tool for every investigation?
No. There is no universally best digital forensics tool in 2026 because acquisition and analysis requirements differ between disks, mobile devices, RAM, networks, cloud accounts, and specialized artifacts. A validated multi-tool workflow is usually stronger than a single-product ranking.
Are free digital forensics tools reliable enough for professional work?
Free tools such as Autopsy, The Sleuth Kit, Volatility 3, Wireshark, Plaso, Timesketch, and specialized Windows parsers can provide useful professional capabilities. Reliability depends on validation, documentation, examiner competence, source quality, and corroboration—not simply on whether software is free or commercial.
Can digital forensics recover every deleted file?
No. Deleted-file recovery can be limited by SSD TRIM, flash wear leveling, overwriting, filesystem behavior, encryption, corruption, and the acquisition method. A successful image does not guarantee recovery of previously deleted data.
What is the difference between Cellebrite UFED and Physical Analyzer?
Cellebrite UFED is primarily used to acquire supported mobile-device data, while Physical Analyzer is used to ingest and interpret extractions from UFED and other supported sources. Acquisition depth and analysis results depend on the device, operating system, lock state, license, and supported method.
Does a forensic software report automatically make evidence admissible?
No. Admissibility depends on the jurisdiction and the complete process, including lawful authority, preservation, acquisition, hashing, documentation, validation, examiner competence, reporting, and applicable rules. A commercial product’s report is not a substitute for those controls.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

