
Recommended Free Tools
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
You usually cannot confirm from the outside whether a doctor’s office or hospital was hacked. A service outage, delayed appointment, or switch to paper records is a reason to contact the provider—not proof of a cyberattack. Use a phone number or patient portal you already trust, and rely on the provider’s official updates to learn what is affected and whether your information may be involved.
What signs might suggest a provider’s systems were compromised?
Some warning signs are visible to the provider’s employees or security team, not patients. The U.S. Department of Health and Human Services (HHS) lists possible ransomware indicators including:
- A workforce member realizes they may have clicked a malicious link, opened an attachment, or visited a harmful website.
- Unexplained increases in computer processor or disk activity.
- Files becoming inaccessible, or being encrypted, deleted, renamed, or moved unexpectedly.
- Suspicious communications between malware and an attacker’s command-and-control servers. HHS says IT personnel would most likely identify these through intrusion-detection or similar tools.
These are clues for an organization’s investigation, not a diagnostic checklist for patients. You cannot confirm a provider’s network is compromised by scanning your own device or trying to inspect its systems.
What patients may notice
You may encounter an unavailable portal, canceled appointments, delayed prescriptions, or a temporary change in how the provider handles records. Such disruptions have many possible causes, including routine technical problems. Unless the provider or another reliable official source confirms a cyber incident, do not treat an outage or changed workflow as proof of hacking.
#1 Best Overall
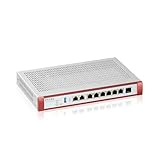
- GOLD SECURITY PACK INCLUDED (2 YEARS): Anti-malware, sandboxing, IPS 2,500 Mbps, web filtering, DNS/IP/URL reputation, app patrol, AI SecuPilot, and full UTM for 24 months from day one
- OFFLINE-CAPABLE SETUP AND UPDATES: Configure via Nebula portal wizard; update firmware offline via FTP on the local network, while the web interface remains fully accessible without internet after each update
- RACK-MOUNT FANLESS DESIGN: with SPI 6,500 Mbps firewall throughput, 2,500 Mbps IPS, 1,200 Mbps VPN, the firewall supports up to 100 users, 600,000 concurrent sessions, 100 IPSec tunnels, 50 SSL VPN users, and 32 VLANs
- MULTI-GIG FLEXIBLE PORTS: 6 x 1G plus 2 x 2.5G RJ-45 ports assignable as WAN or LAN, WAN load balancing, active-backup failover, 32 VLAN interfaces, Link Aggregation, and Device HA
- NEBULA MANAGEMENT AND VPN: Centralized policy control, real-time monitoring, and SD-VPN orchestration; supporting IKEv2/IPSec, SSL, Tailscale VPN, 100 IPSec tunnels, 50 SSL VPN users, and up to 40 managed APs
What should you do if care or services are disrupted?
- Contact the provider through a known channel. Use a phone number from a previous bill, the provider’s established website, or a patient portal you have used before. Ask whether appointments, prescriptions, records access, or other services are affected.
- Check for an official update. Look on the provider’s established website or for a direct notice. Be cautious with unexpected messages: verify a link or phone number independently before using it.
- Follow the provider’s care instructions. Ask how to reschedule, obtain a prescription, or access records if the usual process is unavailable. Follow any confirmed alternate procedure the provider gives you.
- Keep any incident notice. If the provider says personal information may be involved, retain its notice and use the contact details and protective steps it specifies. Do not assume which data was exposed or decide on your own that a reportable breach occurred.
These are practical steps for patients and caregivers. The technical response is the provider’s responsibility: HHS advises covered organizations to activate their incident-response plan, assess the incident’s scope and spread, contain it, remove malware, recover systems, and review what happened afterward. Depending on the circumstances, the organization may isolate affected systems to prevent further spread.
How can you tell whether medical records were exposed?
A system disruption and an exposure of protected health information (PHI) are separate questions. In the United States, HHS considers ransomware or other malware on a HIPAA-regulated entity’s systems a security incident. That finding alone does not establish that PHI was accessed or disclosed, or that a reportable breach occurred. The provider’s investigation and applicable rules determine what happened.
Rank #2

- MULTI-LAYERED SECURITY HARDWARE: Reputation filtering (IP/DNS/URL) and SecuReporter visibility included in Entry Defense Pack, while the optional Gold Security Pack license unlocks anti-malware, sandboxing, web filtering, IPS, and full UTM
- OFFLINE-CAPABLE SETUP AND UPDATES: Configure via Nebula portal wizard; update firmware offline via FTP on the local network, while the web interface remains fully accessible without internet after each update
- RACK-MOUNT ENTERPRISE DESIGN: with SPI 15,000 Mbps firewall throughput, 7,000 Mbps IPS, and 3,000 Mbps VPN, the firewall supports up to 500 users, 2,000,000 sessions, 1,000 IPSec tunnels, 500 SSL VPN users, and 128 VLANs
- MULTI-GIG PORTS WITH 10G SFP+ AND POE+: featuring 8 x 1G + 2 x 2.5G + 2 x 10G SFP+ ports; while ports 3 and 4 support PoE+ (30W total), WAN load balancing, failover, Link Aggregation, and Device HA
- NEBULA MANAGEMENT AND VPN: Centralized policy control, threat monitoring, and SD-VPN orchestration; supporting IKEv2/IPSec, SSL, Tailscale VPN, 1,000 IPSec tunnels, 500 SSL VPN users, and up to 520 managed APs
For a HIPAA breach assessment, HHS identifies four factors an entity considers when evaluating whether there is a low probability that PHI was compromised:
- The nature and extent of the PHI, including identifiers and the likelihood of re-identifying an individual.
- Who used or received the information without authorization.
- Whether the PHI was actually acquired or viewed.
- The extent to which the entity mitigated the risk.
Under the HIPAA Breach Notification Rule, covered entities and business associates must provide notification following a breach of unsecured PHI. An impermissible use or disclosure is generally presumed to be a breach unless the applicable entity demonstrates a low probability of compromise through the required assessment. A ransomware message, rumor, or outage by itself does not tell you whether that assessment found a breach.
Rank #3
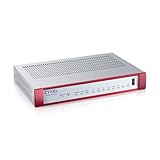
- MULTI-LAYERED SECURITY HARDWARE: Reputation filtering (IP/DNS/URL) and SecuReporter visibility included in Entry Defense Pack, while the optional Gold Security Pack license unlocks anti-malware, sandboxing, web filtering, IPS, and full UTM
- OFFLINE-CAPABLE SETUP AND UPDATES: Configure via Nebula portal wizard; update firmware offline via FTP on the local network, while the web interface remains fully accessible without internet after each update
- COMPACT FANLESS DESIGN WITH POE+: with SPI 4,000 Mbps firewall throughput, 1,500 Mbps IPS, 900 Mbps VPN, the firewall supports up to 50 users, 300,000 concurrent sessions, 50 IPSec tunnels, and PoE+ (30W) through port number 8
- FLEXIBLE SOFTWARE-DEFINED PORTS: 8 x 1G RJ-45 ports (port 8 supports PoE+) assignable as WAN or LAN, WAN load balancing, active-backup failover, 16 VLAN interfaces, and Link Aggregation for resilience
- NEBULA MANAGEMENT AND VPN: Centralized configuration, monitoring, and SD-VPN orchestration; supporting IKEv2/IPSec, SSL, Tailscale VPN with 50 IPSec tunnels, 25 SSL VPN users, and up to 24 managed APs
How should you read a provider’s incident notice?
Use the notice to understand what the provider has confirmed and what you need to do; do not try to make your own technical or legal determination. Look for:
- Whether the provider confirms a cyber incident or is still investigating.
- Which services are affected and how to arrange care or access records.
- Whether the notice says PHI was involved, and which information categories and dates it specifies.
- What steps the provider recommends and how to contact it with questions.
HHS’s July 29, 2026 announcement quoted OCR Director Paula M. Stannard: “An accurate and thorough HIPAA risk analysis is not only required by law, but it is also necessary to protect health information and prevent or mitigate ransomware attacks.” Separately, an HHS Office for Civil Rights announcement on April 23, 2026 described four settled ransomware investigations affecting over 427,000 individuals. That is an enforcement-announcement total, not a measure of the likelihood that any particular provider has been compromised.
Rank #4

- MULTI-LAYERED SECURITY HARDWARE: Reputation filtering (IP/DNS/URL) and SecuReporter visibility included in Entry Defense Pack, while the optional Gold Security Pack license unlocks anti-malware, sandboxing, web filtering, IPS, and full UTM
- OFFLINE-CAPABLE SETUP AND UPDATES: Configure via Nebula portal wizard; update firmware offline via FTP on the local network, while the web interface remains fully accessible without internet after each update
- RACK-MOUNT FANLESS DESIGN WITH POE+: with SPI 6,500 Mbps firewall throughput, 2,500 Mbps IPS, 1,200 Mbps VPN, the firewall supports up to 100 users, 600,000 sessions, 100 IPSec tunnels and PoE+ (30W) through the 2.5G port
- MULTI-GIG FLEXIBLE PORTS: 6 x 1G plus 2 x 2.5G RJ-45 ports (port 2 PoE+) assignable as WAN or LAN, WAN load balancing, active-backup failover, 32 VLAN interfaces, Link Aggregation, and Device HA
- NEBULA MANAGEMENT AND VPN: Centralized configuration, monitoring, and SD-VPN orchestration; supporting IKEv2/IPSec, SSL, Tailscale VPN with 100 IPSec tunnels, 50 SSL VPN users, and up to 40 managed APs
What does this mean outside the United States?
The breach and notification discussion above is specific to U.S. HIPAA rules. Other countries may use different definitions, regulators, and reporting procedures. Wherever you are, contact the provider through a verified channel and follow its official instructions; check the relevant local regulator’s guidance if you need to understand your rights.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

