
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
The contract ends on Friday. By Tuesday, the former vendor’s directory account still works, its VPN certificate has not expired, an OAuth grant can reach a customer portal, and a delegated administrator role remains active. Nothing in the business system automatically tells every identity system that the relationship is over.
Partner access persists because onboarding is tied to a clear business event, while offboarding usually depends on someone remembering to send a notification and finding every copy of that partner’s access. The result is a legitimate-looking attack surface that can survive a termination, project close or partner transfer.
The missing link is between relationship status and identity state
Procurement records the contract, legal records termination terms, and a project owner knows when the work is complete. Identity and access systems, however, often receive none of those authoritative signals. Provisioning has an obvious trigger—contract signature, onboarding or project kickoff. Deprovisioning has no equivalent trigger unless the organization deliberately creates one.
SC Media’s October 14, 2026 analysis describes this asymmetry as the central cause: provisioning responds to business events, but deprovisioning does not. External identities also lack the authoritative human-resources record used for employee access reviews. A periodic certification can therefore show that an account is valid in a directory without revealing that the underlying partnership expired months earlier.
#1 Best Overall

- Control 4 doors, get in the door by swiping card or key fob, get out door by push to exit button. Can store/download/check history entry records and generate report by professional management software.
- Control of memory up to 20,000 user / up to 100,000 logs. Auto open/close at any pre-set time during any day. Support "who" can enter which door at certain time, authorized access control.
- The FRID reader is waterproof, 5-10cm read range. The electric magnetic lock is with 600lbs holding force. Control board is TCP/IP based communication, provide professional designed power cabinet box.
- Have smart phone APP( iOS & Android) to open door remotely. Desktop USB reader,read card number into software so that easy programming/register user. Detail video guide and wire diagram make all easily, you can DIY.
- Network communication via TCP/IP. Software Supportable Database: Access & SQL Server. Support Win7/Win8/Win10/Win11 both 32 & 64 bit ALL Windows system.
One relationship creates many technical paths
A partner may be represented simultaneously in Active Directory or another directory, a VPN, collaboration tools, customer portals, application programming interfaces, cloud resources and synchronized identity stores. Procurement, project management and IT may each know about only part of that footprint.
Disabling a directory account can leave non-directory paths intact. API tokens, OAuth grants, certificates, shared secrets, file-store permissions, delegated roles, shared mailboxes, inherited groups and connected applications each need their own review. A closed ticket or signed termination is therefore evidence of a business decision, not proof that authentication and authorization have stopped.
Rank #2

- Control 4 doors, get in door by swiping card, get out door by exit button or by swiping card,support 4 readers.Can Store/download/check Entry Detail records.
- User capacity: 20,000 user, record capacity:100,000. Auto open/close at any pre-set time during any day. Support "who" can enter which door at certain time, authorized access control.Also support swipe 4 times continuously to keep door open.
- Record never lost in case of power failure.The power supply box with 110-240V input, 5A output, powers the whole system,also act as the cabinet for the control board.Input format of reader Wiegand 26/Wiegand34 (all card reader with compatible protocol, RFID/Mifare/HID).
- Network communication via TCP/IP. Software supportable database: access & SQL server. Support Win7/Win8/Win10/Win11 both 32 & 64 bit ALL Windows system.
- This is Core part of a complete access control system, if you need full kits for lock/reader/exit button, etc,contact us freely, we have 20 years experience.
Why stale partner accounts are difficult to spot
Former partner access often looks safer than it is. A stale account has a history of legitimate use, may originate from a familiar location and can operate during normal business hours. Those signals resemble routine vendor activity rather than an intrusion.
A compromise through a trusted vendor or managed service provider can blend into that traffic. MITRE ATT&CK identifies compromise through a trusted relationship as technique T1199. The risk is not limited to a forgotten username: an attacker may inherit the partner’s tokens, certificates, delegated administration or access to connected services.
Rank #3

- Security: The electromagnetic lock provides reliable access control security, preventing unauthorized entry.
- Convenience: The remote access control system allows authorized personnel to conveniently unlock the door remotely, for example, using a remote control.
- Flexibility: The electromagnetic lock can release immediately upon receiving the unlock signalled, allowing for quick access.
- Automation: The electromagnetic lock can be integrated into an automatic access control system, streamlining the entry and exit process.Multiple authorization methods: Access control systems typically support various authorization methods, such as passwords, card access, and fingerprint recognition, offering a range of access management options.
- Practicality: The electromagnetic lock is easy to install, requires minimal space, and is suitable for various access control scenarios.
Periodic access certification helps only when the reviewer has a complete inventory and current relationship data. If the reviewer sees a valid-looking guest account but not an expired contract, an API key or an inherited group, the certification can approve access that should have disappeared.
What the current numbers say about readiness
Kiteworks’ Data Security and Compliance Risk: 2026 Forecast Report highlights how common the control gap is. These are report findings, not universal rates:
Rank #4
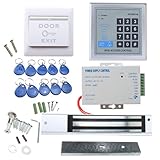
- [Modern Technology for Home Security] This RFID Proximity door access control system kit is one of the modern electronic access control systems
- [Safely and Reliable] The state-of-the-art CPU and integrated circuit techniques are applied to keep all the data from loss due to power failure.
- [Easy To Access] AGPtEK door security system is powerful and can open the door using proximity cards, passwords, or the hybrid.
- [More Convenient] The rfid lock kit access controller can provide users with more convenience by connecting to terminals, including the button for opening the door, doorbell, and electric lock that is normally open or closed.
- [Wide Application] The door lock installation kit offers a method for controlling access safely and automatically, qualifying it as ideal equipment for businesses, offices, factories, and communities. Get the full set of door security system to update your home security!
| Control measured | Finding reported by Kiteworks (2026) | What it means |
|---|---|---|
| Automated partner-access kill switch | 84% lacked one | Termination still depends on manual action across systems. |
| External identity and lifecycle management | 60% lacked it | Organizations may not connect partner status to account state. |
| Joint incident-response playbook with partners | 87% lacked one | Roles and actions during a vendor compromise are undefined. |
| Practiced incident response with third-party vendors | 89% had never practiced it | Even documented procedures may fail under pressure. |
How to offboard a partner everywhere
Complete offboarding is a chain of inventory, revocation, rotation and proof. NHI Mgmt Group’s guidance includes direct users and the less visible credentials that often survive account closure.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →- Name one accountable owner. Assign a person who owns the relationship end state, not merely the termination ticket. That owner should coordinate procurement, the project team, IT, security and application owners.
- Freeze new access and enumerate existing paths. Export the partner’s users, groups, shared mailboxes, service accounts, API tokens, OAuth grants, certificates, shared secrets, file-store permissions, delegated roles, synchronized directory objects and connected applications. Include customer portals, VPNs, cloud resources and collaboration systems.
- Revoke identities and privileges. Disable or remove direct accounts, guest objects, legacy security groups, delegated administration and project-specific roles. Remove inherited memberships rather than assuming a parent account change will do it.
- Revoke or rotate machine credentials. Invalidate API tokens and OAuth grants; revoke certificates; rotate shared secrets; and update applications that depended on those credentials. A token that remains valid after a user is deleted is still an authentication path.
- Reconcile assets and ownership. Confirm that files, repositories, cloud resources, automation jobs, integrations and customer data have an internal owner. Transfer assets before removing the final partner administrator, and record exceptions with an expiry date.
- Test denial. Attempt authentication and authorization through each material path, including a retired user, a previously issued token, a delegated-admin route and a connected application. The expected result is a logged denial or an invalid credential, not merely an absent account in one directory.
- Preserve evidence. Keep the termination record, inventory, revocation and rotation timestamps, test results, approver and any exception decision. NHI Mgmt Group recommends evidence that the retired path can no longer authenticate or authorize access.
What changes during a partner transfer
A transfer to a new partner is not a reason to leave the outgoing partner’s access in place “temporarily.” Microsoft’s partner-transfer guidance treats secure cutover as two linked actions: transfer assets while removing residual access.
Best Value

- It's ANSI heavy duty electric door strike lock,widely used in North American. Note that 1).It's installed within your door frame,need to Cut Door Frame if have no existing hole. 2).It's NOT for PUSH Bar,it's for Knob lock or Mechanic Lock which has handle. 3).Lock Length is 4.84 in. Make sure size is sutiable for your door before purchase. 4)1000kg Force, Keep locked in case of power failure by default(fail secure mode), also can adjust to Fail Safe mode.
- Control 4 doors.Get in the door by swiping card or password, and get out door by turning lock handle or knob. Can store/download/check entry records and generate report by professional management software.Powerful and professional management software makes the system have many extended control functions.Have smart phone APP to open lock remotely. App support operate system: iOS( iPhone),Android.
- User capacity: 20,000 user / up to 100,000 records. Auto open/close at any pre-set time during business hour or any day. Support "who" can enter which door at certain time, authorized access control.
- The keypad reader is outdoor waterproof, supports card, PIN, card + PIN. Card type: EM-ID card. Less than 0.2 second response speed, 5-10cm proximity range. Desktop USB reader,read card number into software so that easy programming/register user. We provide detail video guide and wire diagram to you, so that you can easily DIY to setup the whole system. We also provide live support for ever.
- Network communication via TCP/IP, software supportable database: Access & SQL Server. Support Win7/Win8/Win10/Win11 both 32 & 64 bit ALL Windows system. After programming done, it's fully stand alone running system, no need network connection, no need hook to computer.
Outgoing partner
- Remove outgoing partner accounts and delegated-administrator privileges.
- Delete legacy security groups and stale guest objects.
- Revoke tokens, certificates, OAuth grants and shared secrets tied to the outgoing relationship.
Incoming partner
- Reconcile assets and ownership before granting access.
- Issue named accounts and least-privilege roles rather than copying the previous partner’s permissions.
- Increase monitoring after the transfer so unexpected use is investigated while the new arrangement stabilizes.
Make the end date an enforceable identity event
The durable fix is to convert a relationship deadline into an automatic identity action. Microsoft Entra access packages provide the practical pattern: a policy can set an expiry, and on expiry the associated resource access is revoked, group membership is removed, and the guest account can be removed. Audit logs are retained, and notifications can confirm completion.
Expiry does not replace an immediate termination procedure. It is a backstop for relationships that end without a timely notification and a way to prevent indefinite standing access. High-risk roles still need prompt revocation, credential rotation and a denial test.
Manual notification versus event-driven control
| Decision area | Manual notification | Event-driven expiry and revocation |
|---|---|---|
| Trigger | A person sends a ticket or email after termination. | A contract or access-package end date drives an identity action. |
| Coverage | Usually the systems the requester remembers. | Defined resources, groups and external identities covered by policy. |
| Privilege model | Existing standing rights may be copied or left unchanged. | Least-privilege roles can be issued for a bounded period. |
| Proof | Paper confirmation or a closed ticket. | Revocation logs, notifications and tested denial. |
| Failure mode | Missed notification, forgotten token or unclear ownership. | Policy misconfiguration or an unconnected system, which an inventory must expose. |
Controls that keep partner access bounded
- Use named ownership: every partner relationship, application connection and exception needs an accountable internal owner.
- Set an expiry at issuance: avoid open-ended guest access, delegated administration and project roles.
- Prefer least privilege: grant only the resources and actions required for the current work, then remove them when the work changes.
- Inventory non-human credentials: include service accounts, API keys, OAuth grants, certificates and shared secrets in the same lifecycle process as user accounts.
- Reconcile systems: compare procurement and project records with directory, cloud, application and secrets inventories so an external identity cannot hide in an unowned system.
- Monitor the transition: review partner activity after a transfer or termination, especially use of administrative roles and previously trusted locations.
- Practice with the partner: define who can revoke access, rotate credentials, preserve logs and communicate during an incident, then rehearse those actions.
When can an organization say offboarding is complete?
Completion requires more than disabling a user. The accountable owner should be able to show that every identified authentication and authorization path was revoked or rotated, assets were reassigned, the retired credentials failed a deliberate test, and the evidence is retained for audit or incident response.
If any system cannot confirm its state, treat that path as an unresolved exception with a named owner and a short, explicit deadline. The governing principle is simple: a partnership’s end date must become an identity event, not just a line in a procurement record.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

