
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Sovereign AI infrastructure is not a data-center location or a marketing label. It is a set of demonstrable controls over jurisdiction, data and model handling, compute hardware and software, operations, connectivity, security, and exit. To buy it responsibly, define the control your organization requires, map each workload and legal obligation, then demand contractual and technical evidence from every provider and subcontractor.
The European Union is a useful case study, but EU rules do not govern every buyer. The same procurement method works elsewhere: separate where data sits from who can access it, who operates the stack, which laws can compel disclosure, how the system can be moved, and whether your organization can keep running it during a provider or network failure.


What “sovereign AI infrastructure” means
There is no single worldwide legal definition of sovereign AI infrastructure. The European Commission describes tech sovereignty as “Europe’s ability to act independently in the digital world by developing and controlling key technologies, data, and infrastructure, while reducing reliance on non-EU providers.” That is an official EU policy definition, not a universal procurement test. You can read the Commission’s definition in Strengthening Europe’s Tech Sovereignty.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →For a buyer, sovereignty is best treated as an evaluable control objective. A service is more sovereign when your organization can establish, with evidence, who controls the legal entity, data, keys, administrators, hardware, software supply chain, support process, network paths, and recovery plan. A service can have a server in your country and still expose data to foreign ownership, foreign support personnel, foreign legal compulsion, uncontrolled telemetry, or an impractical exit path.
Conversely, an on-premises cluster is not automatically sovereign if the organization cannot patch it, replace failed accelerators, verify firmware, manage privileged access, or continue operating when a critical supplier is unavailable. The right level of control depends on your threat model, workload, jurisdiction, operational capability, and continuity requirements.
What sovereignty does not prove
- A regional cloud location does not, by itself, establish control over the provider, staff, support accounts, legal exposure, or onward transfers.
- A “sovereign” product name does not prove that prompts, outputs, logs, backups, telemetry, or model artifacts remain under your rules.
- A locally purchased GPU accelerator card is only one component; it does not constitute a compliant server, cluster, network, operating model, or exit plan.
- Compliance with one regime does not discharge duties under another. GDPR transfer analysis, Data Act obligations, and AI system obligations address different questions.
Turn sovereignty into a control checklist
Use the following dimensions in your request for proposal (RFP), architecture review, and contract. For each dimension, require a named owner, an auditable artifact, and a remedy if the commitment is missed.
| Control area | Questions to answer | Evidence to request |
|---|---|---|
| Jurisdiction and corporate control | Which legal entities own and operate the service? Where are they incorporated and managed? Which foreign laws could compel access? Where are operational decisions made? | Entity chart; ownership and control disclosures; governing-law terms; government-request procedure; notification, challenge, and escalation commitments. |
| Data and model governance | Where are training, fine-tuning, retrieval, inference, logging, backups, and telemetry performed? Which people or systems can see prompts, outputs, datasets, and weights? | Data-flow diagrams; retention and deletion schedules; access-control model; backup and observability handling; model and dataset licensing statements. |
| Operations and support | Who administers the platform? From which countries? Is support remote, on-site, or subcontracted? Can privileged access be approved, recorded, and revoked by you? | Staff and subcontractor list; access-procedure runbooks; session logs; background-screening and training requirements; service-management and escalation terms. |
| Compute and supply chain | What accelerators, servers, firmware, drivers, orchestration layers, inference frameworks, and model components are used? Can they be replaced without a single-source dependency? | Bill of materials; provenance and serial-number records; software and firmware signing process; vulnerability and patch policy; lead times and replacement commitments. |
| Technology autonomy | Can you operate, audit, export, and maintain the stack without proprietary control planes or unavailable vendor tools? | Documented interfaces; source or escrow terms where applicable; supported open standards; administrator training; offline or degraded-mode procedures. |
| Security and compliance | How are identities, keys, networks, secrets, workloads, and audit records protected? Which party is responsible for each legal and contractual duty? | Responsibility matrix; independent audit reports; key-management design; vulnerability-management records; incident and breach procedures; audit rights. |
| Resilience and exit | What happens during a region, provider, hardware, software, or network failure? What can be exported, in which formats, at what cost, and within what time? | Business-continuity plan; recovery objectives; tested export and restore; transition assistance; retrieval windows; termination and deletion certificates. |
| Connectivity | Can the network move your data and synchronize training or storage at the required rate and latency? Are routes, peers, encryption, segmentation, and failover understood? | Measured service commitments; route and peering information where material; redundancy design; workload-specific test results; failure-mode documentation. |
| Capacity and environment | Are power, cooling, land, water, staffing, and hardware available for the growth you forecast? What constraints apply at each site? | Power and cooling plan; capacity-reservation terms; staffing coverage; hardware lead-time data; water and environmental-impact information; scaling procedure. |
Choose an operating model against your threat model
There is no universally most sovereign architecture. Compare the options against the sensitivity of each workload and the people and capital you can commit to operating it.
Free tools Windows power users keep installed
One-click scans. No signup required.
| Option | Where it can provide strong control | Trade-offs to test |
|---|---|---|
| On-premises infrastructure | Direct control of physical access, network boundaries, keys, administrators, hardware custody, and data location. | Your organization carries power, cooling, staffing, patching, spare parts, capacity planning, and disaster-recovery responsibilities. A supplier may still control firmware, drivers, or support access. |
| Locally operated sovereign cloud | Local operations and facilities can reduce cross-border exposure while providing pooled capacity and managed services. | Verify the operator’s ownership, support personnel, subcontractors, control plane, telemetry, government-request process, and ability to export workloads. |
| Dedicated or isolated cloud environment | Physical or logical isolation can limit co-tenancy and give you dedicated networks, keys, and administrator boundaries. | Isolation does not remove the provider’s legal control or software dependencies. Confirm who can enter the environment, how isolation is evidenced, and how shared management systems are handled. |
| Hybrid or federated design | Places the most sensitive data or models under tighter control while using external capacity for burst, disaster recovery, or less-sensitive inference. | Every data movement, identity trust, model synchronization, and failover path becomes a sovereignty boundary. Test degraded operation and prevent accidental replication into a less-controlled site. |
Start with workload tiers
- Classify information. Separate personal data, regulated records, classified or mission-critical material, proprietary training data, model weights, prompts, outputs, logs, and operational telemetry.
- Classify the AI activity. Distinguish training, fine-tuning, retrieval-augmented generation, batch inference, real-time inference, evaluation, and experimentation. Each has different movement and retention patterns.
- State the threat model. Record concerns such as foreign legal compulsion, insider access, supply-chain tampering, service interruption, network isolation, or loss of a provider.
- Set recovery and performance objectives. Define acceptable recovery time and data loss, synchronization frequency, inference latency, throughput, and maintenance windows from the workload rather than from a generic marketing tier.
Connectivity: buy for the workload, not a slogan
The European Commission says its proposed Digital Networks Act is intended to support investment in high-capacity fibre, 5G, and future networks. That is policy direction, not a universal bandwidth or latency specification. The appropriate target depends on data volume, movement patterns, user geography, training synchronization, storage traffic, inference latency, recovery objectives, and cross-site dependencies. The Commission’s technology-sovereignty policy page is at https://digital-strategy.ec.europa.eu/en/policies/eu-tech-sovereignty.
Specify measurable network requirements
- Training and fine-tuning: quantify dataset ingress, checkpoint size, synchronization interval, and the maximum time allowed for a failed worker to rejoin.
- Inference: define end-to-end latency, concurrency, jitter tolerance, and the proportion of requests that can run asynchronously.
- Storage and backup: calculate sustained and peak transfer rates, replication distance, encryption overhead, and restore windows.
- Users and sites: map user geography, private links, internet exposure, cross-border routes, and dependencies on identity, key-management, and monitoring services.
- Resilience: specify independent paths, carriers, network equipment, power domains, and the behavior when a route or peering relationship fails.
Questions for a connectivity proposal
- Request measured service commitments for the paths your workload will use, not only a port speed.
- Ask for route and peering information where a jurisdiction, interception, or outage risk makes it material.
- Require encryption in transit, network segmentation, tenant isolation, and administrative access controls.
- Ask the provider to demonstrate a failed link, degraded throughput, and a recovery without bypassing your security controls.
- Run a representative workload test that includes dataset transfer, distributed training synchronization, inference traffic, logging, and a restore. Record the test date, topology, software versions, and results in the contract’s service baseline.
Do not adopt one latency or bandwidth number as a definition of sovereignty. A system can satisfy a network target and still fail the legal, operational, or supply-chain controls that matter to your organization.
Compute and supply-chain control
A vendor technical overview from NVIDIA describes four sovereign-AI pillars: data and benchmarks, models, hardware infrastructure, and frameworks. It says infrastructure may be on-premises or cloud-based but should be inside national borders and subject to robust governance and security. This is NVIDIA’s technical guidance, not a legal test; the overview is available at https://www.nvidia.com/en-us/lp/industries/global-public-sector/sovereign-ai-technical-overview/.
Inventory the complete stack
- Hardware: accelerator models, host servers, networking, storage, power systems, firmware, replacement stock, and country of manufacture where relevant.
- Software: operating systems, drivers, orchestration, schedulers, inference frameworks, registries, monitoring, and update channels.
- Models and data: base-model origin, weights, tokenizer and evaluation artifacts, dataset licences, fine-tuning records, and restrictions on redistribution or commercial use.
- People and suppliers: integrators, maintenance contractors, remote-support teams, logistics providers, and any party with privileged access.
A GPU accelerator card can be an illustrative compute component, but purchasing a card does not establish sovereign operation. Confirm that the full server, cluster interconnect, firmware, drivers, scheduler, cooling, power, support, and compliance controls can be acquired and run under your required authority.
Reduce hidden dependencies
- Require a current bill of materials and a change-notification period for hardware, firmware, software, and subcontractors.
- Define how security patches are validated, signed, staged, rolled back, and applied when a vendor service is unavailable.
- Specify replacement availability, compatible alternatives, and maximum hardware lead times for critical components.
- Document which control-plane functions stop working if a licence, internet connection, vendor account, or external registry is unavailable.
- Arrange independent vulnerability assessment and provenance checks for firmware, container images, model packages, and update artifacts.
Data and model governance that survives an audit
Draw a separate data-flow for every stage: collection, preprocessing, training, fine-tuning, retrieval, inference, logging, backup, support, evaluation, and deletion. Do not assume that “customer data” covers prompts, outputs, embeddings, traces, crash dumps, or model checkpoints.
Contractual controls
- State the permitted purposes for each dataset, prompt, output, model artifact, and log.
- Prohibit undisclosed training, product improvement, advertising, or benchmarking use.
- Set retention periods and deletion methods for primary storage, replicas, backups, caches, observability systems, and support tickets.
- Assign ownership and licence rights for fine-tuned weights, adapters, prompts, evaluation sets, and generated outputs.
- Require prior approval for new subprocessors, processing locations, support countries, and telemetry destinations.
- Give your organization the ability to approve privileged sessions, inspect logs, rotate keys, and revoke access.
Technical verification
Verify deletion with evidence from storage, backup, and monitoring systems rather than accepting a statement that an account was closed. Test whether a provider can export model weights, configurations, metadata, logs, and access records in usable formats. Confirm that the exported artifacts can be restored in a second environment with the documented dependencies.
EU compliance as a concrete case study
EU sources illustrate why sovereignty cannot be reduced to residency. They are not automatically the rules for organizations outside their scope, and legal applicability depends on the organization, data, service, and activity.
Rank #3
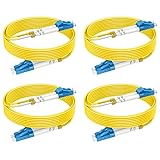
- 【6ft/2m 4pack OS2 Fiber Optic Patch Cable】 As AI continues to advance at an unprecedented pace, having reliable and efficient connectivity is crucial.RamboCables offers a cost-effective solution for your AI infrastructure with the 4-Pack OS2 LC-LC Single Mode Fiber Patch Cables. These high-quality fiber optic patch cords are designed to provide reliable and efficient connectivity for your AI applications.
- 【Wide Application】Whether you're using AI for data processing, machine learning, or other applications, the OS2 LC-LC Single Mode Duplex Fiber Patch Cable is ideal for connecting high-speed transceivers such as 10G SR, 40G BIDI SR, QSFP+, SFP+, and more. It is suitable for 1G/10G/40G/100G/400G Ethernet connections, making it a versatile choice for data centers, cloud storage networks, server farms and any other environments where reliable fiber optic connectivity is essential.
- 【Max Transmission Distance】With the OS2 Single Mode Optic Fiber Cable, you can transmit data for up to 10km at 1310nm or up to 40km at 1550nm. It offers excellent bandwidth at 1310nm-1550nm, with a low attenuation rate of 0.36 dB/km-0.22 dB/km, and can operate in a wide temperature range of -20~70°C, ensuring reliable performance even in harsh environments.
- 【Industry Standard】The OS2 LC-LC Fiber Patch Cords are built to industry standards. With LSZH (Low Smoke Zero Halogen) jacket, LC/UPC to LC/UPC connectors, 9/125μm high-rated fiber cladding, and a 2.0mm cable diameter, feature an LSZH environmentally friendly jacket, Zirconia Ceramic Ferrule, and 15mm minimum bend radius, all in accordance with EIA/TIA 604-2 standards, ensuring optimum insertion loss (IL) and return loss (RL) performance.
- 【Standards & Reliability】With over 15 years of experience manufacturing fiber patch cords, RamboCables are dedicated to supplying high-quality products and services. Our fiber patch cables comply with industry standards to enable efficient network transmission.
GDPR international transfers
GDPR Article 44 requires transfers of personal data to a third country to meet the GDPR’s international-transfer chapter, with the aim that the protection level is not undermined. Assess storage location, access by support staff, remote administration, onward transfers, subprocessors, and the transfer mechanism together. Article 44 is available at https://eur-lex.europa.eu/legal-content/EN/TXT/?qid=1671832038722&uri=CELEX%3A32016R0679.
Data Act switching and third-country access
The Data Act includes cloud-switching and interoperability provisions covering contractual switching conditions, export of data and digital assets, provider assistance, and measures for interoperability. It also addresses certain third-country governmental access to non-personal data held in the Union. Check the actual service scope and applicable obligations; these provisions do not promise frictionless migration. Read the Data Act.
AI Act responsibilities
The Commission describes the AI Act as a risk-based framework and says enforcement by the AI Office and national authorities began on 2 August 2026. A sovereign hosting location does not itself discharge duties that attach to an AI system’s provider, deployer, or user. Confirm your role, the system’s classification, its purpose, and the current applicable law with qualified counsel. The Commission’s policy overview is at https://digital-strategy.ec.europa.eu/en/policies/european-approach-artificial-intelligence; the consolidated text is at https://eur-lex.europa.eu/legal-content/en/ALL/?qid=1790822129312&uri=CELEX%3A02024R1689-20260727.
Cloud and AI Development Act proposal
The Commission describes the Cloud and AI Development Act (CADA) as a proposed act. Its page presents four proposed assurance levels:
- Union-based data storage and processing.
- Added independence from third countries and software-supply-chain transparency.
- EU ownership and control plus additional criteria.
- Full transparency and control over the software supply chain, with no third-country interference.
These levels are the Commission’s proposed framework description, not a settled procurement rule or enacted law. The proposal also sets a policy goal of at least tripling EU data-centre capacity within five to seven years, while identifying energy, land, water, and financing as constraints. Treat that as a target, not a delivered outcome. See the Commission’s Cloud and AI Development Act page.
Recommended Free Tools
Commission sovereign-cloud procurement figures
The Commission reports that its April 2026 sovereign-cloud procurement awarded a EUR 180 million contract to four providers. Its framework evaluated 48 criteria across eight categories. These are figures from that Commission procurement account, not market-wide statistics. The framework explanation is at https://commission.europa.eu/news-and-media/news/sovereign-cloud-framework-explained-2026-06-01_en.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Build the RFP and contract in stages
- Write the sovereignty objective. State the jurisdictions, legal exposures, data classes, operator boundaries, and failure scenarios you must control. Avoid an untestable requirement such as “fully sovereign.”
- Publish workload facts. Include dataset sizes, model and checkpoint sizes, training topology, inference profile, user locations, growth forecast, recovery objectives, and maintenance constraints.
- Require architecture disclosure. Request facility locations, legal entities, ownership, staff and subcontractors, data flows, network routes, control-plane dependencies, hardware bill of materials, and software supply-chain details.
- Score evidence, not labels. Give credit for verifiable contracts, logs, tests, audits, diagrams, and demonstrations. Treat unsupported sovereignty claims as unanswered requirements.
- Run a controlled proof of concept. Test ingress, training or inference, key rotation, administrator approval, logging, incident response, failover, export, and restoration with representative data.
- Negotiate remedies. Define service credits or other remedies, notification periods, audit access, breach escalation, subcontractor controls, government-request handling, and termination assistance.
- Test exit before production. Export data, model artifacts, configurations, logs, and metadata; restore them elsewhere; measure elapsed time, missing dependencies, and operator effort.
- Review continuously. Reassess ownership, legal exposure, support countries, routes, firmware, software versions, capacity, and applicable law at scheduled intervals and after material changes.
Evidence and contract schedule
Attach a schedule that turns each promise into a reviewable artifact. A practical schedule includes:
- Current facility and processing-location list, including backup and disaster-recovery sites.
- Legal-entity, ownership, control, governing-law, and government-request disclosures.
- Named operators, subcontractors, access countries, privileged-access workflow, and session-retention period.
- Data-flow maps for training, inference, logging, telemetry, support, and deletion.
- Hardware and software bill of materials, provenance records, patch process, and replacement commitments.
- Network topology, measured workload results, route and peering details where material, segmentation, encryption, and failover behavior.
- Audit reports, control mappings, incident-notification deadlines, evidence-preservation duties, and customer audit rights.
- Export formats, interfaces, assistance hours, retrieval windows, fees, deletion verification, and tested restoration results.
- Power, cooling, staffing, capacity-reservation, environmental, and scaling assumptions.
Capacity, energy, and operating reality
AI capacity is constrained by more than accelerator count. Verify available power, cooling method, rack density, water constraints, land, permits, trained staff, hardware lead times, and maintenance coverage at every proposed site. Ask how the provider scales during a demand spike and what happens when expansion equipment is delayed.
The Commission’s CADA page identifies energy, land, water, and financing as constraints while proposing at least tripling EU data-centre capacity within five to seven years. That target does not guarantee capacity for your workload or location. Obtain a site-specific capacity reservation, expansion trigger, and contingency plan.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesCommon failure modes and corrective actions
“The data is in our country, so we are sovereign.”
Correct the assumption by mapping ownership, administrator access, support countries, legal compulsion, telemetry, backups, and onward transfers. Add contractual controls and technical evidence for each path.
“The provider passed a security audit, so the AI workload is covered.”
Check the audit scope and shared-responsibility boundary. Confirm that model weights, prompts, training data, orchestration, accelerators, and privileged operations are included or separately controlled.
“Portability is guaranteed because an export button exists.”
Export a representative workload, including metadata, configurations, logs, model artifacts, and dependencies. Restore it in another environment and record what failed, what required assistance, and how long it took.
“A dedicated environment removes foreign-control risk.”
Review the owner of the control plane, licence servers, update channels, remote-support tools, and emergency-access process. Logical or physical dedication does not change legal control by itself.
“The network has enough bandwidth.”
Replace the claim with workload tests covering peak transfer, synchronization, inference latency, backup, route failure, encryption, and recovery. Record the exact topology and date so later changes are detectable.
“A proposed EU framework is already a binding certification.”
Label CADA’s assurance levels and capacity goal as proposed Commission descriptions. Verify the law and procurement rule that actually applies when you buy.
A decision rule for buyers
Select the architecture that gives your organization the required control without creating an operating burden it cannot sustain. For each workload, reject an option if any critical control lacks an owner, evidence, contractual remedy, or tested fallback. Then compare the remaining options on legal exposure, data and model handling, operator control, supply-chain dependency, connectivity, resilience, capacity, energy, staffing, and exit effort.
Document the decision and its assumptions. Sovereignty is not a permanent property of a product: a change in ownership, support location, network route, firmware, model service, law, or subcontractor can change the risk. Continuous evidence collection and an exercised exit plan are therefore part of the infrastructure, not paperwork added after deployment.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

