
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
Configure an AI network-change system as a controlled change-management pipeline, not as an unrestricted command runner. Give the agent narrowly scoped authority to prepare a versioned proposal; check that proposal against policy and the approved configuration baseline; test it before production; obtain approval from the accountable reviewer when its risk requires it; block execution until that approval is recorded; and retain evidence of the decision, implementation, and observed result.
This approach follows NIST configuration-management and DevSecOps guidance. Firewalls, routers, gateways, switches, controllers, and their configuration files are controlled items. An AI-generated recommendation is an input to the process, not production authorization.
What guardrails must accomplish
A useful guardrail is an enforceable control around an AI agent’s ability to propose or execute a network change. It should constrain the target, identity, timing, command set, and maximum effect of an action. It should also make unsafe or unreviewed work impossible to run through the production execution path.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →NIST configuration-management guidance treats network components as configuration items. Your process therefore needs to define which changes are controlled, assess their security and operational impact, document approved work, restrict access, and monitor activity. NIST’s DevSecOps reference model adds a critical rule for AI output: generated corrective actions remain proposed inputs and must not modify configurations or system state without review and approval through established processes.
#1 Best Overall

- SonicWall TZ270W Appliance Only - No Service Subscription (02-SSC-2823) - Combines enterprise-grade firewalling with integrated 802.11ac Wave 2 Wi-Fi to deliver secure wired and wireless connectivity in one compact device for small offices and clinics.
- Blocks zero-day threats and ransomware with Capture ATP sandboxing enhanced by RTDMI, plus IPS and anti-malware scanning for layered protection.
- Eliminates the need for separate access points in smaller spaces thanks to built-in high-speed wireless that is simple to deploy and manage.
- Supports VPN, SD-WAN, and TLS 1.3 decryption to secure hybrid cloud access and remote workers while maintaining usability and performance.
- Delivers gigabit performance with up to 750,000 concurrent connections to handle growth in users, devices, and SaaS applications.
Human experts remain responsible for governance, approval, and mission outcomes. AI can accelerate analysis, draft commands, identify drift, or prepare a rollback, but it does not become the accountable change owner merely because its output passed a model confidence check.
Separate the control layers
Do not rely on a single prompt, model policy, or vendor feature. Use independent layers so that a mistake in one layer does not directly become a production change.
| Layer | Purpose | Examples of enforceable controls |
|---|---|---|
| Agent scope | Limit what the AI is allowed to inspect or propose | Read-only inventory access, named device groups, approved change types, maximum object counts, and an explicit operating window |
| Proposal format | Make every suggestion reviewable and attributable | Versioned change record containing target, intended state, rationale, dependencies, impact, validation, and recovery information |
| Policy and baseline checks | Reject proposals that violate deterministic rules | Configuration baseline comparison, authorization checks, prohibited commands, segmentation rules, maintenance-window checks, and scope limits |
| Preproduction validation | Find syntax, compatibility, and security problems before production | Linting, simulation, lab or staging tests, reachability checks, peer review, and documented test results |
| Approval gate | Require the designated decision before execution | Risk-based routing, recorded approval tied to an exact proposal version, expiration, escalation, and execution blocking |
| Execution boundary | Prevent bypass of the workflow | Restricted service identity, approved controller or automation interface, just-in-time credentials, and a check that approval still matches the proposal hash |
| Observation and recovery | Detect unexpected effects and restore service | Post-change verification, telemetry, alerts, versioned configurations, tested recovery procedures, and a complete audit trail |
AI guardrails and network policy enforcement are related but different. For example, Microsoft Foundry’s documented Network control governs a hosted agent’s outbound connections; it is an egress control, not a general approval system for changing routers or firewalls. A network policy engine, controller, or access-control layer must enforce authorization at the point where a change would actually be applied.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Step 1: Define scope, ownership, and authority
Start with an inventory of the components and configuration items the agent could affect. Include physical and virtual routers, switches, firewalls, gateways, load balancers, VPN concentrators, wireless controllers, cloud network objects, and the repositories that hold their intended configuration.
Write the scope in operational terms
- List permitted targets by environment, site, device group, account, subscription, or project.
- List permitted change types, such as adding a documented firewall rule, changing a route in a test segment, or updating a switch description.
- Identify prohibited operations, including disabling security controls, changing management-plane access, altering identity sources, or touching an unowned device.
- Specify which identities may initiate proposals and which restricted identity may execute an approved change.
- Define maintenance windows, blackout periods, emergency handling, and conditions that require immediate escalation.
- Name the accountable technical approver and the business or service owner for each important network segment.
Use least privilege. The proposal-generating agent normally needs broad read access but narrowly bounded write capability, if any. Workflow automation should force requests through approved interfaces rather than allowing the model to open an arbitrary session to a device. NIST identifies logical access controls, workflow automation, and change windows as possible restrictions; your organization must select the controls appropriate to its architecture and risk tolerance.
Step 2: Require a structured, versioned proposal
Have the agent create a change request instead of emitting an untracked sequence of commands. Store the request in a system that assigns an immutable identifier and revision. A reviewer should be able to tell exactly which proposal was tested and approved.
| Proposal field | What to record |
|---|---|
| Identity and provenance | Agent or service identity, initiating user, model or workflow version, creation time, and source event |
| Target | Device or cloud object identifiers, environment, site, owner, and dependency map |
| Current and intended state | Relevant baseline values and the precise resulting configuration |
| Rationale | Incident, ticket, policy requirement, capacity need, or other traceable reason |
| Impact analysis | Services, trust boundaries, availability, security exposure, and affected users |
| Implementation | Normalized commands or API operations, ordering, prerequisites, and estimated duration |
| Validation | Tests to run, expected results, pass/fail evidence, and reviewer notes |
| Recovery | Device-specific restoration or reversal steps, prerequisites, owner, and estimated recovery time |
| Expiration | Maintenance window, approval expiry, and conditions that invalidate the request |
Hash or otherwise bind the approval to the exact proposal revision. If the target, command set, scope, or validation evidence changes materially, create a new revision and require a new decision. Do not let a workflow silently substitute a later AI output for the artifact a reviewer approved.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteStep 3: Check policy and baseline before asking for approval
Run deterministic checks before a human spends time reviewing the proposal. Compare the requested state with the approved baseline and test both authorization and safety constraints.
Rank #2
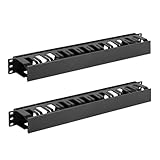
- Space-saving: This server rack cable management is made of plastic, lightweight,easy to assemble and disassemble,can save space and manage cables
- Muti-access: Rack mount cable management has 12 slots and 2 back accesses to organize and distinguish countless cables separately
- User-friendly Design: Removable Top Cover makes this 1u cable management easy to add or remove bundled cables
- Easy to use:This rack mount cable management is easy to install,with instructions or videos for reference;Accessories including 12-24 Cage nut and Screw×8,10-32 Screw×8,you can choose according to the actual installation
- Widely Applicable: Rack cable management is suitable for 19in wide AV/IT/Data/Audio racks and server cabinets in home office, studio and other workplaces
Useful pre-approval checks
- Target check: confirm that every object is in the agent’s permitted inventory and belongs to the stated environment.
- Identity check: verify the requester, service account, and required ownership relationships.
- Change-type check: reject commands outside the allowed operation set or containing prohibited verbs and fields.
- Baseline check: detect drift between the recorded current state and the live device before calculating a change.
- Security check: evaluate segmentation, exposure, authentication, encryption, logging, and least-privilege policies.
- Dependency check: identify routes, address objects, certificates, interfaces, applications, and other changes that must precede or follow the request.
- Window check: verify that the requested implementation time is permitted and that required personnel are available.
- Completeness check: fail closed when impact, validation, owner, or recovery information is missing.
Reject or escalate a proposal that exceeds scope, fails validation, conflicts with the baseline, or cannot be assessed with adequate confidence. A model’s assertion that an action is safe is not a policy decision. NIST requires security-impact consideration, testing, validation, and controlled access, but does not prescribe a particular policy engine; select one that can produce repeatable, reviewable results in your environment.
Step 4: Validate in a representative environment
Testing belongs before operational implementation. Use the strongest environment available for the change: a lab that mirrors production, a simulator, a staging segment, or a controller’s dry-run and commit-check function. The less representative the test, the more conservative the approval tier should be.
Validation sequence
- Capture the relevant live state and verify that it matches the proposal’s recorded starting point.
- Render the intended configuration or API operations in a normalized form that a reviewer can inspect.
- Run syntax, schema, dependency, and policy validation.
- Apply the change in a representative lab, simulator, or staged environment where feasible.
- Exercise service reachability, routing, authentication, logging, and security-control tests that correspond to the affected segment.
- Record test inputs, software and device versions, timestamps, outputs, failures, and the person or service that evaluated the results.
- Require technical peer review for a meaningful blast radius, novel behavior, or security-sensitive control.
NIST IR 8011 describes testing, validating, documenting, requesting approval, and recording implementation as distinct workflow activities. Although its example concerns software vulnerability management and the publication dates to 2020, those control behaviors translate well to network changes when adapted to the actual devices and topology. NIST’s DevSecOps model likewise calls for peer review and security validation of AI-generated outputs.
Step 5: Design risk-proportionate approval tiers
There is no universal NIST threshold that tells every organization which network changes may run automatically. Define tiers through your own impact and risk analysis, then publish the criteria so the agent and reviewers apply them consistently.
| Illustrative tier | Typical characteristics | Required decision |
|---|---|---|
| Preapproved, low impact | Reversible, narrowly scoped, well tested, no security-boundary change, and within an explicitly approved pattern | Automated approval may be permitted by policy; retain the proposal, checks, and result for audit |
| Standard review | Limited production effect, a known procedure, moderate dependency or service impact, or incomplete automation coverage | Explicit approval from the designated technical reviewer before execution |
| High impact | Multiple sites, core routing, broad firewall policy, identity or management-plane access, sensitive segments, or a difficult recovery | Named accountable authority, documented validation, and any additional service-owner or security approval required locally |
| Novel or uncertain | Unfamiliar device behavior, conflicting telemetry, failed tests, out-of-scope target, or insufficient recovery evidence | Block execution and escalate for analysis; do not downgrade the request merely to keep automation moving |
Score or classify requests using factors such as potential operational and security impact, reversibility and recovery time, confidence and completeness of preproduction validation, execution privileges, affected scope, and uncertainty. Treat a material change in any of those factors as a reason to recalculate the tier.
Human oversight must also be sustainable. AWS guidance for agentic AI warns that routing every action to a person can produce fatigue and rubber-stamping. Reserve mandatory review for actions whose consequences justify it, while preserving automatic controls for trivial, well-bounded work. That balance is a local governance decision, not a vendor-defined universal policy.
Step 6: Enforce the approval gate in the execution path
Approval is meaningful only when the executor cannot bypass it. Put the gate between the approved workflow and the network controller, API, or device session. The executor should verify all of the following immediately before applying the change:
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errors- The request is in an approved state and has not expired.
- The approver is authorized for the target and risk tier.
- The approval references the exact proposal revision or hash.
- All required policy and validation checks are still passing.
- The target’s current state has not drifted from the state that was reviewed.
- The maintenance window and required operational conditions are active.
A timeout must not silently count as approval. Define overdue-decision flags, escalation recipients, and cancellation behavior. If a reviewer rejects the request, record the reason and prevent retries from changing the proposal without a new revision. NIST IR 8011 describes automated approval notifications, overdue flags, blocking until designated approval, implementation records, and completion notifications; those behaviors are directly useful when implementing a network workflow.
Rank #3
- What You Will Get: 20pcs of self adhesive hook and loop cable ties in black color, Each cable organizer is 1.13 x 3.55 in/2.88 x 9 cm, suitable to meet your various cable management on or under desk needs
- Strong Adhesive Backing: Designed with strong adhesive backing, they cord holders are easy to use. They can be firmly adhered and keep the cable tidy for a long time, which increases its reliability
- Reliable Quality: Made of premium nylon material, these cable straps have excellent insulation and wear resistant, which can support for a long time
- Reusable and Adjustable: You can adjust the adhesive appliance cord organizer according to your different cable management needs. Reusable and practical, help you to organize the messy cables and keep them neat and orderly
- Wide Application: These self-adhesive hook and loop cable ties for organizing cords suitable for home, office, computer room, kitchen, studio, game competition, workshop and so on
Step 7: Execute narrowly and observe the result
Use a restricted execution identity and an approved automation interface. Do not give the language model a reusable administrator credential or an unrestricted shell. The workflow should submit the already-approved operation, capture the device or controller response, and stop if a prerequisite or expected state is missing.
- Re-read the target state and perform the final approval and drift checks.
- Acquire short-lived or otherwise tightly scoped credentials for the approved target.
- Apply only the normalized operations in the approved order.
- Record each operation, response, return code, timestamp, and execution identity.
- Run the post-change tests defined in the proposal.
- Compare observed state and service telemetry with the intended result.
- Send completion or failure notifications to the responsible staff and change record.
Monitor for side effects after the command reports success. Watch reachability, routing convergence, interface health, authentication, error rates, security alerts, and the services named in the impact analysis. A successful API response proves only that the interface accepted a request; it does not prove that the network achieved the intended operational state.
Step 8: Make recovery an operational procedure
Recovery must match the platform, topology, and failure modes. A guardrail configuration rollback is not necessarily the same as restoring a changed firewall, router, or cloud network object. Before approval, identify the authoritative previous state, the person or service that can restore it, required access, dependencies, and the maximum acceptable recovery time.
Rehearse recovery in a controlled environment. Test device configuration restore, controller commit reversal, route withdrawal, access restoration, and any service-specific remediation that the change could require. Keep versioned configuration and guardrail definitions so you can identify which version was active when the failure occurred. AWS recommends versioned guardrails, monitoring of guardrail interventions, and rollback in its agentic-AI guidance; those recommendations are a general pattern, not a universal device-level network recovery standard.
Build an audit record that can reconstruct the change
Retain enough evidence for an operator, auditor, or incident responder to reconstruct what happened without relying on model memory. At minimum, capture:
- Immutable request identifier, proposal revision, and content hash.
- Initiating user, agent identity, model or workflow version, and creation time.
- Target inventory identifiers, environment, owner, and baseline snapshot.
- Policy, authorization, scope, and drift-check results.
- Test and validation evidence, including failures and reviewer comments.
- Risk classification, approver identity, decision, timestamp, and any conditions.
- Execution identity, exact operations submitted, device responses, and completion status.
- Notifications, post-change observations, alerts, and recovery actions.
- Links to the related incident, ticket, service owner, and configuration versions.
Protect the record from alteration and set retention according to your compliance and incident-response requirements. NIST configuration-management guidance calls for documenting and monitoring controlled changes; the detailed field list above is an implementation design that makes those requirements practical for AI-assisted work.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Choose a workflow pattern deliberately
Organizations commonly combine three patterns. Compare them against the same decision axes rather than choosing one because it appears more automated.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →| Pattern | Strengths | Risks and safeguards | Best fit |
|---|---|---|---|
| Direct human approval | Clear accountability and useful context for unusual work | Slow queues and reviewer fatigue; use escalation, expiration, and concise evidence | High-impact, novel, or security-sensitive changes |
| Preapproved automation | Fast and consistent for repeatable work | Pattern drift or hidden scope expansion; constrain targets, parameters, and blast radius and retain complete logs | Low-impact, reversible changes with strong tests and an explicit policy exception |
| Risk-tiered approval | Balances speed with oversight by routing work according to impact and uncertainty | Misclassification can bypass review; make classification deterministic where possible and escalate ambiguous cases | Mixed environments with enough change history to define reliable tiers |
For every pattern, evaluate potential impact, reversibility and recovery time, validation quality, execution privileges, reviewer workload and timeout behavior, and audit-trail quality. The cited NIST and AWS guidance supports these axes but does not prescribe a universal scoring formula.
Rank #4

- Compact and Efficient Design: The FortiGate 40F is designed for small to mid-sized businesses and enterprise branch offices, featuring a compact, fanless desktop form factor that ensures quiet operation and minimizes space usage.
- Robust Connectivity Options: Equipped with 5 GE RJ45 ports, including 1 WAN port and 4 internal ports, this model provides essential connectivity and flexibility for various network configurations in a small-scale environment.
- High-Performance Security: Offers up to 1 Gbps IPS throughput and 600 Mbps threat protection throughput, using Fortinet’s purpose-built security processor technology to deliver industry-leading performance and protection for SSL encrypted traffic.
- Advanced Threat Protection: Integrated with Fortinet’s AI-powered FortiGuard Labs, the FortiGate 40F offers comprehensive cybersecurity, identifying and mitigating both known and unknown threats to maintain robust security across your network.
- Simplified Management and Deployment: Features a user-friendly management console that provides comprehensive network automation and visibility, coupled with Zero Touch Integration with Fortinet’s Security Fabric for easy deployment.
Common failure modes and fixes
The agent can reach devices directly
Remove unrestricted credentials and route all writes through a broker or controller that checks the request state, target scope, and approval binding. Keep direct access for emergency procedures separately governed and logged.
The reviewer approves a description, not the actual commands
Show normalized operations, before-and-after state, dependencies, test evidence, and the proposal hash. Invalidate approval when any material element changes.
A stale baseline causes an apparently safe diff
Read the live state immediately before execution and fail closed on drift. Recalculate the proposal and repeat review when the starting point changed.
Every request is sent to a person
Define a preapproved tier for genuinely low-impact, reversible, well-tested patterns. Keep deterministic checks, logging, and post-change monitoring; do not use automation merely to hide missing governance.
A timeout becomes an implicit yes
Represent pending, approved, rejected, expired, and cancelled as separate states. Escalate overdue decisions and block execution until an authorized approval exists.
Rollback means only restoring the AI policy
Document and test restoration for the actual network platform. Guardrail rollback can prevent future actions but may not undo a route, rule, interface, or access change already applied to a device.
Implementation checklist
- Inventory controlled network components and define owners.
- Publish permitted targets, operations, identities, windows, and escalation conditions.
- Implement a versioned proposal schema with impact, validation, and recovery fields.
- Run deterministic scope, authorization, baseline, security, dependency, and window checks.
- Test in a representative lab, simulator, or staging environment and record evidence.
- Define local risk tiers and approvers; do not treat model confidence as authorization.
- Bind approval to an immutable proposal revision and enforce the gate at execution.
- Use restricted credentials and approved interfaces for implementation.
- Verify live state before and after execution and monitor service effects.
- Rehearse device-specific recovery and retain versioned configurations.
- Preserve proposal, decision, execution, notification, and observation records.
- Review metrics such as rejected proposals, drift failures, approval latency, rollback frequency, and unplanned impact to improve the tiers.
The Bottom Line
Let AI prepare and analyze network changes, but keep authorization, validation, execution, and recovery inside your existing configuration-management controls. Scope the agent tightly, enforce deterministic checks and an approval gate, scale human review to risk, and retain evidence from proposal through post-change monitoring.
Free tools Windows power users keep installed
One-click scans. No signup required.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

