
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
AI is changing biometric security in both directions: machine learning can support identity matching and fraud detection, while generative AI can create or alter media used to fool remote identity checks. A face match alone does not prove that an image came from a live person or an authentic capture. Effective protection depends on the entire identity workflow—from capture and transmission to automated analysis, human review, privacy safeguards, and recovery.
Biometric identity proofing and authentication are different jobs
Biometric systems use physical or behavioral characteristics—such as a face or fingerprint—to support a decision about identity or access. The role of that comparison depends on the workflow.
| Process | What it is trying to establish | Where biometrics may fit |
|---|---|---|
| Identity proofing | Whether a person is who they claim to be, often as part of enrollment or account creation. | A biometric may be compared with an image or other evidence associated with the claimed identity. |
| Authentication | Whether someone attempting to access an account or service is authorized to do so. | A biometric may unlock or provide access to an authenticator, or serve as one part of an authentication process. |
A match is an output from a system, not proof that every preceding step was trustworthy. In remote identity proofing, the submitted media might be forged, altered, or substituted before it reaches the comparison system. In authentication, the biometric may simply be the convenient way a user accesses an authenticator; it does not automatically make that authenticator phishing-resistant.
How AI can improve identity systems—and add risk
AI and machine learning can help identity services compare biometric samples, validate evidence or identity attributes, detect suspected fraud, and assist users through a process. These capabilities can make identity workflows more automated, but the decision still depends on the data, model, thresholds, and process around it.
#1 Best Overall

- FIDO-ONLY FUNCTIONALITY: Supports FIDO2 (passkeys) and FIDO U2F protocols for passwordless and second-factor authentication. Does not support OTP, TOTP, Smart Card (PIV), or other advanced features - upgrade to YubiKey 5 Series for extended functionality
- SECURE AND CONVENIENT: Passwordless MFA login with the YubiKey Bio authenticator and biometric information using a fingerprint, with a PIN as a fallback. Simply plug in via USB and use your fingerprint to authenticate
- DEVICE & OS COMPATIBILITY: Compatible with Windows, macOS, ChromeOS, and Linux. Works seamlessly with supported services like Google and Microsoft accounts, and major password managers. See the full compatibility list at "Works With YubiKey"
- DURABLE & RELIABLE: Resistant to tampering, water, and crushing. No batteries or network connectivity required, offering dependable authentication without any downtime. Securely manufactured in USA & Sweden
- Yubico Authenticator App - Fingerprint enrollment, passkey management and PIN configuration available via the app app - Upgrade to YubiKey 5 Series to generate one-time-passwords (OTP) via Yubico Authenticator and for advanced compatibility (OATH, PIV)
NIST’s Digital Identity Guidelines, SP 800-63-4, published in July 2025, describe AI/ML uses and associated expectations for identity systems. The guidelines address identity proofing, authentication, and federation for people interacting with government information systems over networks. They supersede SP 800-63-3; they are not a universal legal rule for every organization.
For organizations within the guidance’s scope, AI/ML use is not just a model-selection issue. NIST calls for communicating relevant use of AI/ML and documenting privacy-risk assessments for personal information processed by these systems. The guidance also addresses information such as model training, datasets, updates, and testing that should be made available to relying organizations.
How deepfakes, spoofing, and injection target remote checks
Presentation attacks
A presentation attack happens when someone presents a fake sample at a sensor—for example, an image or another spoof intended to be mistaken for the person being checked. Liveness detection is one approach used to counter such attacks. It is a defense to evaluate, not a guarantee that every spoof will be detected.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsRank #2

- POWERFUL SECURITY KEY: The YubiKey 5C NFC is the most versatile physical passkey, protecting your digital life from phishing attacks. It ensures only you can access your accounts
- WORKS WITH 1000+ ACCOUNTS: Compatible with popular accounts like Google, Microsoft, and Apple. A single YubiKey 5C NFC secures 100+ of your favorite accounts, including email, password managers, and more
- FAST & CONVENIENT LOGIN: Plug in your YubiKey 5C NFC via USB and tap it, or tap it against your phone (NFC), to authenticate. No batteries, no internet connection, and no extra fees required
- MOST SECURE PASSKEY: Supports FIDO2/WebAuthn, FIDO U2F, Yubico OTP, OATH-TOTP/HOTP, Smart card (PIV), and OpenPGP. That means it’s versatile, working almost anywhere you need it
- PRIMARY & SPARE KEYS: Just like having a spare house key, we recommend buying two YubiKeys - one for daily use and one as a spare. That way you’ll never get locked out of your accounts
Forged or AI-modified media
Generative AI can produce or modify images and video that may be used against document validation, biometric operations, or a human reviewer. NIST’s identity-proofing guidance discusses deepfakes in these contexts. A convincing media sample can challenge both automated checks and people, so a face comparison by itself is not a complete defense.
Digital injection
With digital injection, forged or modified media is inserted after capture but before the component that analyzes or reviews it. The capture device, software path, and data channel therefore matter alongside the matcher. NIST states that “A biometric comparison performed with a captured sample does not prevent these attacks.”
Face morphing
Face morphing combines facial images into a single image. NIST researcher Mei Lee Ngan has described it as a possible identity-fraud mechanism, including the risk that more than one person could use a passport bearing a morphed photo. This illustrates an attack path; it does not establish how common morphing attacks are.
Rank #3
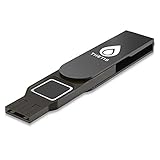
- Embedded Fingerprint Sensor - Advanced embedded fingerprint sensor which facilitates a world-class one-of-a-kind password-less experience. A powerful security chip with state-of-the-art cryptographic algorithms ensures protection of online accounts and passwords.
- Password-less Future - Created with FIDO2 certification, experience a password-less future in an interoperable authentication process and make daily log-in experiences easy, instant, and protective for an advanced and revolutionary style of password-less security. **Note: FIDO2 does not support Mac log-in.
- U2F Backwards Compatibility - Thetis FIDO2 Fingerprint Key is backwards compatible with any and all websites that follow U2F protocols and work side-by-side with the newest Chrome browser and other popular operating systems such as: Windows, MacOS, Linux, and more. Note: Only Enterprise Users using Azure Active Directory can access Windows Hello log-in via Thetis FIDO2 Fingerprint Security Key.
- Multi-layered Authentication - Created with world-renowned HOTP (One Time Password) technology which creates a password-less solution to standard tokens. The leading multi-factored authentication process is with Thetis security key.
- Take It Anywhere - Designed to be small and compact to fit and be taken anywhere: car keys, pocket, purse, etc.
Build defenses around capture, analysis, and review
A stronger remote identity workflow does not rely on one detector or one successful match. NIST’s SP 800-63A-4, Identity Proofing and Enrollment, points to controls that address different stages of the process:
- Test for manipulation. Analyze submitted media for signs of modification or forgery. Document which attack artifacts were tested and the system’s false-negative rates, rather than describing detection as comprehensive without supporting evidence.
- Protect the media path. Use authenticated channels for remote media. Consider passive manipulation detection as well as sensor authentication or device attestation, which can help establish whether capture hardware is trusted.
- Test against both attacks and genuine media. Evaluate detection methods using attack artifacts and genuine samples. A detector that flags attacks but also wrongly rejects legitimate people can create operational and access problems.
- Use human review where appropriate. Trained reviewers can provide an escalation path when automated checks are uncertain. For attended remote collection, NIST describes randomized cues such as asking a person to move or to move an object between the sensor and their face.
- Plan for errors. Define what happens when a match or liveness check fails, is inconclusive, or conflicts with other evidence. The process should offer a controlled review or recovery route rather than treating every automated result as final.
These measures address different weaknesses: liveness checks focus on presentation at a sensor, media analysis looks for signs of manipulation, and authenticated capture paths help reduce opportunities to substitute data after capture. None should be represented as eliminating all remote identity fraud.
Evaluate accuracy, privacy, and performance across groups
Security evaluation should include both error rates and the conditions under which those rates were measured. False acceptance and false rejection performance are relevant to the system’s intended use, and the evaluation should include demographic testing. For covered biometric performance testing, NIST SP 800-63A-4 requires conformity with ISO/IEC 19795-1:2021 and ISO/IEC 19795-10:2024, including demographic testing.
Rank #4

- POWERFUL SECURITY KEY: The Security Key C NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key C NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key C NFC via USB-C and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
Privacy belongs in the same evaluation. Biometric information and AI-generated inferences can create risks involving re-identification, expanded insights about individuals, or uses beyond the original purpose. The FTC has also identified deepfake-enabled impersonation as a concern associated with biometric information. An organization should be able to explain what it collects, why it needs it, how it is handled and retained, and what reuse is permitted. NIST’s AI/ML guidance calls for documented privacy-risk assessments for personal information processed by identity systems using these methods.
NIST’s older biometric technology material also discusses template-protection approaches intended to make a compromised biometric template revocable. Such approaches can reduce some consequences of compromise, but they do not erase the need to protect biometric data or limit its use.
Recommended Free Tools
Biometrics do not automatically make an authenticator phishing-resistant
A biometric can be a convenient way to unlock an authenticator without being the property that makes the authenticator secure against phishing. In its April 2024 supplement announcement, NIST says correctly implemented syncable authenticators provide a phishing-resistant authenticator and describes native biometrics as one possible consumer-friendly platform feature. The distinction matters: the security claim applies to the correctly implemented authenticator, not to every login that happens to use a face or fingerprint.
Best Value

- Passwordless Login with Fingerprint Security: imKey Pass S6 is a FIDO2-certified hardware security key designed for passwordless authentication. Simply plug in the device and verify with your fingerprint to securely sign in to supported services. This physical passkey protects your accounts from phishing, password leaks, and unauthorized access.
- Strong Two-Factor Authentication (2FA) Protection: Supports FIDO2 and FIDO U2F protocols, allowing you to enable strong hardware-based 2FA on popular platforms including Google, GitHub, Amazon, X and Binance. Replace SMS codes or authenticator apps with a safer hardware login method.
- Fingerprint + PIN Dual Protection: Built-in fingerprint sensor provides fast local identity verification, while an optional PIN adds an additional layer of protection. Even if the device is lost, unauthorized users cannot access your accounts without biometric verification.
- Universal Compatibility with Modern Systems: Works with Windows, macOS, and major browsers including Chrome, Edge, Safari, and Firefox that support WebAuthn and Passkey authentication standards. A single key can secure multiple online accounts and services.
- Compact, Durable & Easy to use: Designed as a portable USB-C security key that easily attaches to your keychain. No battery, no charging, and no software installation required. Just plug in and authenticate with a fingerprint.
When assessing an authentication design, consider the authenticator’s security properties, how the biometric is used to access it, and how users can recover access. A biometric check should be understood as one element of that design, not as a substitute for evaluating the full authentication method.
Questions to ask before adopting biometric identity verification
Use these questions to compare systems and providers. NIST supports these as evaluation dimensions, but it does not provide a vendor-by-vendor product comparison in the guidance cited here.
- What performance evidence is available? Ask for measured false acceptance and false rejection results, the test conditions, and demographic performance testing.
- Which attack types have been evaluated? Look for evidence covering presentation attacks, forged or modified media, and digital injection. Ask which artifacts were tested and how false negatives are documented.
- How is capture protected? Establish how devices and data channels are authenticated, and what controls help detect substitution or manipulation between capture and analysis.
- What happens when automation is uncertain? Identify when trained reviewers intervene, how decisions are escalated, and what recovery or fallback path is available.
- What privacy controls apply? Review the documented privacy-risk assessment, collection and retention practices, access controls, and restrictions on reuse.
- What AI/ML evidence can the provider supply? Ask about relevant training data, datasets, model updates, and testing, as well as how AI/ML use is communicated to organizations relying on the service.
The answers should describe the deployed workflow, not just the accuracy of a matching component. A capable matcher cannot compensate for an untrusted capture path, weak review procedures, or unclear privacy practices.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

