
Reliable embedded fault detection is not a choice between static analysis and runtime monitoring. Start with a fault model and safety requirements, prevent and find defects before execution, monitor residual risks on the target, and use controlled fault injection to verify that detection leads to the required response. Each monitor needs a defined detection deadline, safe state, and diagnostic record; each test needs evidence tied to the product’s applicable safety requirements.
Start with the faults the system must handle
“Fault” can mean several different things in embedded software. A coding defect may be systematic and reproducible; a hardware fault may be transient; a timing overrun may occur only under particular load; a communication fault may corrupt or delay data; and tampering may change firmware or configuration. A single checker is unlikely to cover all of these.
For each credible fault, connect the fault analysis to a specific safety requirement and response. FMEA/FMECA, fault-tree analysis, and freedom-from-interference analysis can help identify scenarios to address. For each scenario, record:
- Fault and affected function: what can fail, and which behavior or safety goal is at risk.
- Detection deadline: how quickly the fault has to be detected for the required response to remain effective.
- Required response: whether the system must isolate a component, reconfigure, recover, or enter a defined safe state.
- Evidence: what diagnostic record, test result, or analysis will show that the requirement was met.
This mapping prevents a common design gap: a system may detect an anomaly without specifying what it must do next, or may define a safe response without showing that the fault will be detected in time.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall
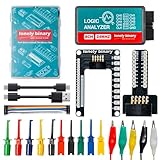
- 【High-Speed 8-Channel Analysis】Captures digital signals at up to 24MHz across 8 channels, enabling precise debugging of complex protocols like I2C, SPI, and UART—ideal for advanced STEM projects without the limitations of basic 4-channel models.
- 【User-Friendly Design】Base module and breakout board simplify connections to breadboards, microcontrollers, and other setups.
- 【Logic Level Expansion Board】Breaks out all 8 channels to 2.54mm male pins and pads for alligator clips, enabling flexible and secure connections in diverse projects.
- 【Logic Level Breadboard Adapter】 Easily connects the logic analyzer to breadboards, providing direct and convenient access to all 8 channels for prototyping and testing.
- 【Dual USB Connectivity】Comes with both USB-A and Type-C cables for universal compatibility with older PCs, modern laptops, and devices, ensuring hassle-free plug-and-play across Windows, Mac, Linux, and Ubuntu.
Prevent and detect defects before execution
Use coding rules as a foundation, not a proof of safety
MISRA C defines a constrained C subset and coding rules intended to make automated checking and formal analysis more tractable in safety- and security-critical embedded software. Roberto Bagnara, Abramo Bagnara, and Patricia M. Hill discuss that role in their 2018 paper. MISRA compliance can reduce exposure to certain defect patterns, but it does not establish that a product is free of faults or that its safety mechanisms work.
Pair the project’s selected MISRA rule set with static analysis and documented review of deviations. The 2026 MDPI survey identifies model checking, abstract interpretation, data-flow analysis, and symbolic execution as core static-analysis families used in embedded systems. Depending on the method, implementation, and configuration, these approaches can help find issues such as memory-safety violations, data-flow errors, races, and coding-rule violations before deployment.
Make analysis repeatable
Static-analysis results are only useful as project evidence if another engineer can understand what was checked. Keep the analysis configuration with the results, including:
Rank #2

- ✅ High-Performance 16-Channel Logic Analyzer: Cost-effective LA1010 USB logic analyzer with 16 input channels and 100MHz sampling rate per channel, featuring portable design and included KingstVIS PC software.
- 🌐 Real-Time Signal Visualization: Simultaneously capture 16 digital signals and convert them into clear digital waveforms displayed instantly on your PC screen for precise analysis.
- 🔍 Protocol Decoding & Data Extraction: Decode 30+ standard protocols (I2C, SPI, UART, CAN, etc.) to extract human-readable communication data, accelerating debugging.
- 🛠️ Multi-Application Tool: Ideal for developing/debugging embedded systems (MCU, ARM, FPGA), testing digital circuits, and long-term signal monitoring with low power consumption.
- 💻 Cross-Platform Compatibility: Supports Windows 10/11 (32/64bit), macOS 10.12+, and Linux – drivers auto-install, no configuration needed.
- Tool name and version, selected checks, and the MISRA edition or project rule set in use.
- Compiler and target configuration relevant to the analysis.
- Suppressions and deviations, with review decisions and rationale.
- Findings, dispositions, and any changes that require analysis to be rerun.
Direct checks toward the project’s fault model as well as its coding rules. Typical targets include undefined behavior, buffer bounds, null or invalid pointers, integer overflow, uninitialized data, infeasible control paths, races in interrupt-driven code, and project-specific invariants. Static methods analyze source or models; they do not, by themselves, demonstrate that a particular runtime fault will be detected within its deadline.
Use runtime monitors for faults that depend on operation
Some faults depend on hardware state, actual timing, inputs, configuration, or execution history. Runtime monitoring can detect these during startup or operation, but every monitor consumes resources and can itself share failure causes with the software it checks. Select monitors from the fault model rather than adding checks indiscriminately.
Choose monitor coverage deliberately
Useful monitor targets include:
- Firmware and configuration integrity: detect changes to code or configuration that are relevant to the safety case.
- Control-flow and sequence integrity: check that critical functions or operations occur in an expected sequence.
- Task timing: check periodic-task timing and deadlines, including watchdog behavior where relevant.
- Communication and peripheral state: detect relevant peripheral or communication anomalies.
- Data and interface invariants: check ranges, plausibility, and inter-task contracts that are meaningful to system safety.
SecMonQ’s 2020 published design illustrates why runtime monitoring should extend beyond control flow: it combines firmware-integrity, peripheral, periodic-task timing, and critical-function sequence monitoring, with safe-state recovery within a defined fault-tolerant time. That example describes a particular design; it is not a universal coverage guarantee for other products.
Rank #3

- The logic for each channel sampling rate of 24M/s. General applications around 10M, enough to cope with a variety ofoccasions; 8-channel
- Sampling rate up to: 24 MHz , can be 24MHz. 16MHz, 12MHz, 8MHz, 4MHz, 2MHz, 1MHz, 500KHz, 250KHz, 200KHz, 100KHz, 50KHz, 25KHz;
- The logic for each channel sampling rate of 24M/s. General applications around 10M, enough to cope with a variety ofoccasions;
- Input voltage range: -0.5V to 5.25V; Input Low Voltage: -0.5V to 0.8V; Input High Voltage: 2.0V to 5.25V
- Input Impedance: 1Mohm || 10pF (typical, approximate); Crystal: +/-20ppm, 24MHz
Budget monitor cost and common-mode risk
Measure the monitor’s CPU, memory, interrupt, and worst-case execution-time impact on the actual target and configuration. Consider whether the monitor depends on the same code, data, clock, or execution path as the component it is intended to check. Shared dependencies can allow a fault to affect both the function and its monitor, weakening detection independence.
A statically tailored kernel can reduce vulnerable runtime state and provide dependability-oriented fault-avoidance and detection mechanisms. The dOSEK project describes this design rationale for OSEK/AUTOSAR systems. Kernel tailoring is an architectural option, not a substitute for product-specific analysis of monitor coverage and resource cost.
How static analysis, runtime monitoring, and fault injection differ
These techniques answer different questions. Static analysis examines software before execution; runtime monitors observe selected properties on the running system; fault injection tests how the implemented system responds when a representative fault is introduced. Use them together where the safety requirements call for prevention, detection, and demonstrated response.
Rank #4
- 16 channels dual-mode support: ①Stream mode captures and transfers data in real time for long sample duration; ②Buffer mode captures and stores data temporarily for high sample rate
- USB 2.0 Type-C interface with up to 16G sample depth in stream mode
- Support for adjustable threshold and shielded wires for a better, cleaner waveform
- 256Mbits on-board SDRAM memory with multiple buffer modes
- Compatibility with WinXP-Win10, macOS, and Linux, supporting nearly 100 protocol decoders, and being open-source on Github
| Technique | When it acts | What it can contribute | Key limitation to assess | Evidence to retain |
|---|---|---|---|---|
| Static analysis | During development, before deployment | Finds classes of source, data-flow, memory-safety, race, or rule violations covered by the chosen methods and configuration | Does not demonstrate detection of every operational fault or prove a runtime response works | Tool and rule configuration, findings, suppressions, reviews, and dispositions |
| Runtime monitoring | At startup or while the system operates | Checks selected integrity, timing, control-flow, peripheral, communication, or invariant properties on the target | Coverage, latency, resource cost, and monitor independence depend on the implementation and target | Monitor-to-requirement mapping, measured overhead, detection behavior, and response records |
| Fault-injection campaign | During verification and validation on a controlled test setup | Tests whether selected injected faults are detected and whether isolation, reconfiguration, recovery, logging, or safe-state behavior follows | Results apply to the fault model, injection locations, and configuration tested; they do not establish universal coverage | Fault cases, injection method and location, observed detection and response, latency, and perturbation overhead |
The values that matter are project-specific: fault-model coverage, detection latency, recovery time, false-positive rate, missed or latent faults, and resource overhead. There is no universal fault-detection percentage established for embedded systems by the sources cited here.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Verify the safety mechanism with fault injection
Fault injection is a verification technique, not merely an extra test. An SAE technical paper from 2015 describes ISO 26262-oriented fault injection as a technique for assessing safety mechanisms and demonstrating correct implementation of safety requirements, within a process that extends from requirements through verification and validation. Its relevance does not remove the need to confirm which ISO 26262 edition and requirements apply to a particular product.
Build cases from the fault model
- Select a safety requirement and fault scenario. Choose a representative fault identified in the system’s analysis, such as data corruption, a control-flow deviation, a timing overrun, a communication error, or a selected hardware or OS fault.
- Define where and how to inject it. Record the injection location, trigger, duration or persistence where applicable, and the conditions under which the case runs. Keep the method controlled and repeatable.
- State the expected outcome before the test. Specify the required detector, detection deadline, isolation or reconfiguration action, recovery behavior, safe state, and diagnostic record.
- Run the test on the intended configuration. Preserve the relevant target, compiler, operating system, AUTOSAR layer if applicable, and test setup details so the result is not generalized beyond the configuration exercised.
- Compare observation with requirement. Record whether the fault was detected, whether the response was correct and timely, and whether there were false alarms, missed or latent faults, or unexpected behavior.
ASFIT, a 2020 AUTOSAR fault-injection approach, demonstrates deriving injection locations through executable static analysis and emphasizes respecting hard real-time overhead constraints. Injection tooling can perturb the system it is testing, so overhead must be measured and considered when interpreting a result.
Best Value

- ★The logic for each channel sampling rate of 24M/s. General applications around 10M, enough to cope with a variety ofoccasions; 8-channel.
- ★Sampling rate up to: 24 MHz , can be 24MHz. 16MHz, 12MHz, 8MHz, 4MHz, 2MHz, 1MHz, 500KHz, 250KHz, 200KHz, 100KHz, 50KHz, 25KHz.
- ★Input voltage range: -0.5V to 5.25V; Input Low Voltage: -0.5V to 0.8V; Input High Voltage: 2.0V to 5.25V.
- ★Input Impedance: 1Mohm || 10pF (typical, approximate); Crystal: +/-20ppm, 24MHz.
- ★UART, SPI, IIC and other communication debugging, let you get twice the result with half the effort. 24M sampling rate, can automatically analyze UART, IIC, SPI and many other standard protocols.
Report coverage without overstating it
For each campaign, report results by fault class and tested configuration. Include detection latency, recovery time, false alarms, missed or latent faults, and injection or monitoring overhead where measured. A result from one ECU, compiler, fault model, or set of injection locations is evidence about that tested setup—not a general detection rate for embedded software.
Connect the evidence to the applicable safety case
Keep a traceable chain from each safety requirement to the fault scenario, prevention or detection mechanism, expected response, and verification evidence. Static-analysis records show what was checked in code under a stated configuration; monitor measurements show behavior and cost on the target; injection results show how selected faults and responses behaved under test. None of these evidence types should be presented as proving more than it actually covers.
ISO 26262, AUTOSAR, MISRA C, and tool-qualification expectations vary with product class, safety integrity level, edition, and jurisdiction. Verify applicability and edition before making a compliance claim. In practice, a defensible design uses prevention to reduce avoidable defects, selective runtime checks for operational risks, and fault injection to test the safety mechanisms that the requirements depend on.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Recommended Free Tools

