
Free tools Windows power users keep installed
One-click scans. No signup required.
iTechGuides is reader-supported. When you buy through links on our site, we may earn an affiliate commission. As an Amazon Associate I earn from qualifying purchases. Learn more
The biggest recovery mistake is treating a backup restore as the end of a ransomware incident. If attackers still have access—or malware that enabled the attack remains in the environment—restoring too soon can bring the compromise into systems you are trying to clean. Contain the incident and check the recovery environment before restoring.
Why restoring a backup too early can make things worse
A backup can contain usable files without proving that the systems or accounts involved in the attack are safe. If an attacker’s access remains, or precursor malware is still present, restoring into an unverified environment risks continuing the compromise. The joint #StopRansomware Guide says: “Care must be taken to identify such dropper malware before rebuilding from backups to prevent continuing compromises.” The guide was revised on October 19, 2023, and reflects operational guidance from CISA, MS-ISAC, NSA, and FBI.
In practical terms, the answer to “How do I restore backups after ransomware without bringing the attacker back?” is: isolate affected systems, investigate the scope and foothold, contain ongoing access, and then restore verified data into a clean recovery environment.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWhat to do before restoring
1. Isolate impacted systems
Disconnect affected systems from networks to limit further spread. Then triage which systems and services need recovery. CISA’s response checklist puts isolation and triage ahead of restoration.
#1 Best Overall

- Use RDX Manager software and RDX systems to securely encrypt business data, with support for FIPS 140-2 validated standards.
- The RDX HDD data cartridges are shockproof, rugged and secure
- Backup, bare metal restore, and air-gap to deter ransomware deliver a secure and flexible safety net for remote workers
- Removable cartridges for quick secure off-site backup, disaster recovery, data transfer and archiving
- Support for DropBox and Google Cloud
2. Investigate the scope and possible foothold
Review logs and detection systems for other affected systems, accounts, and malware that may have enabled or preceded the ransomware activity. Identify which systems and accounts were involved in the breach. Do not assume that the visibly encrypted machines are the only ones at risk.
3. Contain continued access
Address the incident and ongoing access before reconnecting systems or restoring data. Avoid adding unverified systems to a clean recovery network: one unsafe device can undermine the environment intended for recovery.
Rank #2
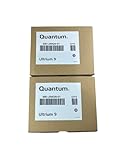
- LTO 9 Tape (MR-L9MQN-01) with storage capacity of 18TB native and up to 45TB compressed capacity
- Supports transfer speeds of 400 MB/s (native), 1,000 MB/s (2.5:1) with Generation 9 tape drives
- Barium Ferrite (BaFe) technology
- Support for tape drive hardware encryption
- Compatible with Linear Tape File System (LTFS)
How to assess backups before using them
A backup is not automatically clean or safe to restore. Check the backup and the recovery plan against these practical questions, which reflect CISA’s recommendations rather than a formal scoring framework:
Recommended Free Tools
- Is it offline and encrypted? Offline, encrypted backups reduce exposure to ransomware and protect stored data.
- Has restoration been tested? Check both the backup’s integrity and whether the restoration process works, rather than relying only on the fact that a backup job completed.
- Is the source known to be clean? Consider whether the backup contains only data or also a system image that may include the original foothold or other malware. Investigate before rebuilding from it.
- Does the restore order respect dependencies? Restore according to critical-service priorities so dependent systems are brought back in a workable order.
Restore in a controlled order
After the incident has been addressed, reconnect systems and restore data from offline, encrypted backups according to the priority of critical services. Follow the order established during triage, and reconnect only systems that have been checked and are clean. Restoration is one stage of recovery; it does not by itself establish that the compromise has ended.
Rank #3

- Minimalist design
- 64-bit Cortex-A55 quad-core 2.0 GHz CPU
- 64-bit Cortex-A55 quad-core 2.0 GHz CPU
- Protect your data from ransomware threats with Snapshots
- QNAP TS-233, 2GB Memory, 1x Gb LAN
Keep external backup drives protected
An external drive can support offline backups, but it is not a complete ransomware defense or incident-recovery plan on its own. CISA advises disconnecting an external drive when it is not actively backing up; if it stays attached, ransomware may reach it too. See CISA’s device and data protection guidance for this advice. Keep backup media offline when not in use, encrypt it, and test that you can restore from it.
What the guidance does—and does not—establish
The joint guide provides organizational recommendations, not a single sequence guaranteed to fit every incident. It does not say that a backup drive alone ensures a clean recovery, and it does not supply a ransomware recovery statistic to apply across organizations. The useful principle is narrower: establish the scope, remove continued access, and protect the recovery environment before bringing systems and data back online.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

