
For most Android app developers, using a trusted execution environment (TEE) means asking Android Keystore to create and use cryptographic keys—not installing code inside the TEE. Keystore keeps key material out of your app process and may use a TEE or StrongBox, depending on the device and the requested key configuration. Check the key’s reported security level, set only the authorizations your app needs, and treat custom TEE software as platform-level work.
What a TEE means for an Android app
A TEE is an isolated secure context intended to protect sensitive operations and data from the main Android environment. In ordinary app development, you generally do not communicate directly with that environment. You use public Android APIs—especially Android Keystore—to request cryptographic operations.
When a key is hardware-backed, Android’s app-facing AndroidKeyStore implementation forwards requests to the keystore daemon. The daemon manages key blobs created through KeyMint; the KeyMint hardware abstraction layer delegates sensitive operations to a trusted application in a secure environment, commonly TrustZone on ARM. Apps use the higher-level Java cryptography APIs; KeyMint itself is a low-level platform interface, not an app API. The Android Open Source Project explains this architecture in its hardware-backed Keystore documentation.
Android Keystore does not make every key hardware-backed. Whether secure hardware is available depends on the device and on whether it supports the requested algorithm, mode, digest, key size, and other parameters.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
#1 Best Overall

- 【Strong Adsorption】The inspiration of the silicone phone suction case comes from the adhesive force of the octopus. Each suction cup phone mount is 3.15 inches long and 2.17 inches wide, with 24 independent suction cups providing a stronger and more stable suction force, so you don't have to worry about your phone falling during use.
- 【Back of Phone Suction Grip】Remove the adhesive film on the phone suction cup and stick it on the phone case. You can then fix the phone on any smooth surface, which is very convenient. (The phone suction cup cannot be removed and reused after being attached to the phone case. It is recommended to attach it to a regular phone case, not a valuable one.)
- 【Widely Used】Our non-slip silicone phone sticky grip mount attaches to almost any flat phone case and make it compatible with common mobile phones such as iPhone and Android.You can shoot, watch videos or video calls in the kitchen, gym, dance studio, bathroom and other places.
- 【Capture the Wonderful Picture】Whether you are a TikTok creator or just like to share videos and photos, this phone suction cup can help you hands-free capture wonderful videos and photos for sharing with friends.
- 【Note】You can fix the phone suction cup on a smooth surface such as a mirror or glass. If necessary, wipe the suction cup with a damp cloth to obtain stronger suction. Before releasing your hand, make sure the phone is firmly fixed. (Not applicable to rough walls, wooden surfaces, and other uneven surfaces)
Use Android Keystore for app-level keys
Create a Keystore key for the specific operations your app needs, then use it through Android’s cryptographic APIs. Define the key’s intended purposes and parameters when creating it: key authorizations cannot be changed afterward. Depending on the key configuration and device, Android can enforce allowed purposes, algorithms, modes, padding, digests, validity periods, and user-authentication requirements.
Key material does not enter your app process during cryptographic operations, as the Android Keystore system guide explains. That is protection against extraction, not a promise that a compromised app or operating system cannot ask the device to perform an operation the key permits. Also, secure hardware may not enforce every authorization—for example, temporal limits may depend on a secure clock that the device does not have.
Check where the key is protected
Do not infer hardware backing from the fact that a key is in Android Keystore. Inspect its KeyInfo security level:
Rank #2

- SUPERIOR COMFORT — Unlike traditional circular ear buds, the design of EarPods is defined by the geometry of the ear. Which makes them more comfortable for more people than any other ear bud–style headphones.
- HIGH-QUALITY AUDIO — The speakers inside EarPods have been engineered to maximize sound output and minimize sound loss, which means you get high-quality audio.
- BUILT-IN REMOTE — EarPods with USB-C plug also include a built-in remote that lets you adjust the volume, control the playback of music and video, and answer or end calls with a pinch of the cord.
- COMPATIBILITY — Works with all devices that have a USB-C port.
- INTEGRATED MICROPHONE — A built-in microphone precisely captures your voice while you’re on the phone, taking a FaceTime call, or summoning Siri — so you’re always heard loud and clear.
- For apps targeting Android 10 (API 29) or later, call
KeyInfo.getSecurityLevel(). A result ofTRUSTED_ENVIRONMENTorSTRONGBOXindicates secure hardware. - For apps targeting Android 9 (API 28) or lower, use
KeyInfo.isInsideSecurityHardware().
Use the result to make a decision consistent with your security policy. If a hardware-backed key is mandatory, do not silently treat a software-backed key as equivalent.
Choose Android Keystore or KeyChain
Use Android Keystore for credentials owned by your individual app. Use KeyChain when a credential may need to be shared system-wide under the user’s control and choice.
Decide whether to request StrongBox
StrongBox is an optional, more isolated secure-hardware implementation for Keystore keys. Devices running Android 9 (API 28) or later can include StrongBox KeyMint, but availability is not guaranteed. The Android Keystore guide characterizes StrongBox as slower, more resource-constrained, and capable of fewer concurrent operations than TEE-backed implementations; it says StrongBox is unnecessary for most apps and should be assessed against the threat model.
Rank #3

- Secure Hold: Our PopSockets adhesive phone grip gives your cell phone a secure, comfortable hold in hand to help prevent drops while texting, taking photos, or scrolling on the go. Designed to stick firmly to most phone cases and devices.
- Hands-Free Made Easy: Easily turn your PopSocket into a phone stand to prop up your phone anywhere, perfect for watching videos, video calls, or following recipes. A must-have phone holder that keeps your device secure and ready for anything.
- Compatibility: Works with all phones, tablets, and Kindles. Sticks best to smooth, hard plastic cases and may not adhere to silicone or textured cases. Easily swap your PopTop to change up your style.
- Black PopSockets: Simple, refined, and endlessly versatile. A timeless essential for any phone.
- Travel Must-Have for People On the Go: A must-have travel accessory for flights, flying, airports, air travel, airplanes, planes, international trips, cruises, and long travel days. Key gadget for your airport haul, travel accessories and must-haves.
| Choice | Availability and security level | Trade-offs |
|---|---|---|
| TEE-backed Keystore key | Depends on device support and the requested key configuration. Inspect KeyInfo; hardware backing is reported as TRUSTED_ENVIRONMENT. |
Typically a better fit than StrongBox when its protection meets the threat model and the app needs broader capability or more operational capacity. |
| StrongBox-backed Keystore key | Optional on devices running Android 9 (API 28) or later. Inspect KeyInfo; the reported level is STRONGBOX. |
Offers stronger isolation, but is slower, more constrained, supports fewer algorithms, and may support fewer concurrent operations. |
Before requesting StrongBox, check for PackageManager.FEATURE_STRONGBOX_KEYSTORE. StrongBox’s documented algorithm subset includes RSA 2048; AES 128/256; ECDSA and ECDH P-256; HMAC-SHA256 with 8–64 byte keys; Triple DES; and extended-length APDUs. Support can vary with the device and Android version, so verify the capabilities relevant to your app rather than assuming every request will work.
An unsupported algorithm or key size can result in StrongBoxUnavailableException. Handle that exception deliberately: fall back to a non-StrongBox Keystore key only if your application’s security policy permits it. If StrongBox is a hard requirement, fail the operation clearly rather than creating a less protected key without the user or system knowing.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →When custom TEE-side development is appropriate
Writing a trusted app that runs inside a TEE is different from using Android Keystore. AOSP describes Trusty as one TEE implementation, comprising a secure OS, Android-kernel drivers, and libraries that let Android-side software communicate with trusted apps. The TEE processor may be a separate microprocessor or a virtualized instance of the main processor, isolated using hardware memory and I/O protections. Other TEE operating systems are possible; Trusty is not the only implementation.
Rank #4

- [360 ° Flexible Rotation Design] Comes with a rotatable lanyard ring that supports 360 ° free rotation, effectively solving the problem of twisted and tangled lanyards
- [Wide compatibility] The ultra-thin 0.02-inch design does not block the charging port at all, and both wired and wireless charging can be used directly without removing the pad. Compatible with most smartphones such as iPhone, compatible with various wristbands, lanyards, crossbody straps, and keychains
- [Durable and Portable Material] Premium rust-resistant stainless steel material with good flexibility, which not only avoids scratching the phone case, but also has excellent anti rust and anti fading performance
- [Multi scenario Practical] Paired with a lanyard or wristband, hands-free use can be achieved. The phone is within reach and not easily dropped, ideal for daily commuting and outdoor activities. Suitable for full coverage phone cases, does not support half coverage phone cases
- [Quality Service] If you find any damage or other issues with the product upon receipt, please contact us immediately. We will handle it quickly
In the documented Trusty model, Android-side applications exchange messages with trusted apps through Trusty APIs, while the message format and meaning are defined by the application protocol. Trusty trusted apps are isolated processes, written in C or C++ (with limited C++ support in the documented version).
However, AOSP’s Trusty documentation states: “Third-party application development is not supported in this version of Trusty.” It explains that trusted apps are developed by one party and packaged with the Trusty kernel image, which is signed and verified at boot. Adding a trusted app also expands the trusted computing base and may expose device secrets. Custom TEE-side code is therefore a platform integration matter requiring the relevant OEM or platform authority; an ordinary Play-distributed app should not assume it can install code into Trusty.
Use app-level Keystore APIs when your goal is to protect an app’s keys or perform cryptographic operations. Consider TEE-side development only when you are working with the platform or device vendor and have a requirement that cannot be met through public Android APIs. AOSP’s Trusty TEE documentation provides the platform-level model and its limitations.
Best Value
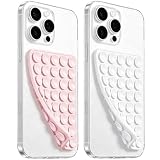
- 【PKYAA Double Sided Silicone Suction Phone Case Mount】PKYAA With Double Sided 40 Strong and Reliable individual suction cups, PKYAA provides a thicken and upgraded universal silicon suction mount for your phone.
- 【Friendly to Content Creators】If you are a content creator or an online influencer, you can create videos anywhere with this suction mount completely hands free with this silicone cell phone mount for cases.
- 【HANDS-FREE & Adhere to Mirrors】This Double Sided silicone suction phone case mount allows you to stick your phone to the mirror easily. No longer holding your phone in one hand to watch video tutorials while making up.
- 【Strong Grip on the Smooth Surface】You can easily hang your phone anywhere with a smooth surface. All you do is you clean off your phone and smooth surface. It is STURDY and it not only sticks to mirrors, it also sticks to windows, it sticks to refrigerators, tiles and other clean, flat surfaces.
- 【Press Down Firmly Every 30 Minutes】Use your palm or fingers to press the phone down firmly and check it's secure before letting go. Apply even pressure for a few seconds to allow the suction cup to adhere properly. To maintain the grip and prevent accidental falls, it's a good practice to periodically reapply pressure to the suction cup.
Understand what the TEE does—and does not—guarantee
Android’s security overview describes several platform uses of trusted hardware and related protections: Gatekeeper performs device PIN, pattern, or password authentication in a TEE; hardware-backed keys can require user authentication; and Trusty is isolated from Android through hardware and software. The same overview discusses SELinux mandatory access controls and Verified Boot, whose chain extends from a hardware-protected root of trust through boot partitions. These platform features do not mean that an arbitrary app can call every protected service directly.
AOSP lists protected-content DRM, mobile payments, secure banking, full-disk encryption, multi-factor authentication, device-reset protection, replay-protected storage, protected wireless display, secure PIN or fingerprint processing, and malware detection as examples of TEE uses. These are examples of platform or device capabilities, not a menu of services that every third-party app can invoke.
For app design, distinguish the protection of key material from the security of the entire operation. Hardware-backed non-exportable keys can make extraction harder, but an attacker who controls a compromised app or operating system may still be able to invoke operations allowed by the key’s authorizations. Keep those permissions narrow and require user authentication when the threat model calls for it. For more detail on Android’s broader controls, see the Android security features overview.
Quick Recap
A practical decision checklist
- Use Android Keystore when an app needs to create or use its own cryptographic key without exposing key material to its process.
- Set key purposes, algorithms, modes, digests, validity, and authentication requirements at creation time; request only what the app needs.
- Inspect
KeyInfoand base any hardware-backing claim or policy on the reported security level. - Request StrongBox only when its additional isolation addresses a real threat and the device supports the necessary feature and key parameters.
- Define a fallback policy before handling an unavailable or unsupported StrongBox request.
- Use
KeyChainrather than app-owned Keystore credentials when system-wide credential sharing under user choice is the requirement. - Approach trusted-app code as OEM or platform integration, not as a deployable extension of a normal Android app.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Recommended Free Tools

